
Change log of the Cyberwatch software
16.0 (2026-10-06)
Cyberwatch 16.0 brings artificial intelligence into the daily work of security teams. An integrated assistant answers questions about your assets. CVEs can include concise summaries, and the executive summary provides prioritized recommendations. This release also measures asset network exposure, extends analysis to assets managed by Microsoft Defender, and makes the application available in Italian
AI features are currently offered free of charge. To request activation, contact Cyberwatch support
The Cyberwatch documentation has a fresh new look and can now be searched using a public MCP server. For configuration instructions tailored to your MCP client, see the Access the documentation via MCP page
The legacy noreply@cyberwatch.fr sender address is no longer offered by default, and emails sent using an address in the Cyberwatch domain will eventually be rejected. Configure an address from your own domain in the SMTP settings. Until you configure an address, the legacy address will continue to be used, and administrators will see a warning
Highlighted features:
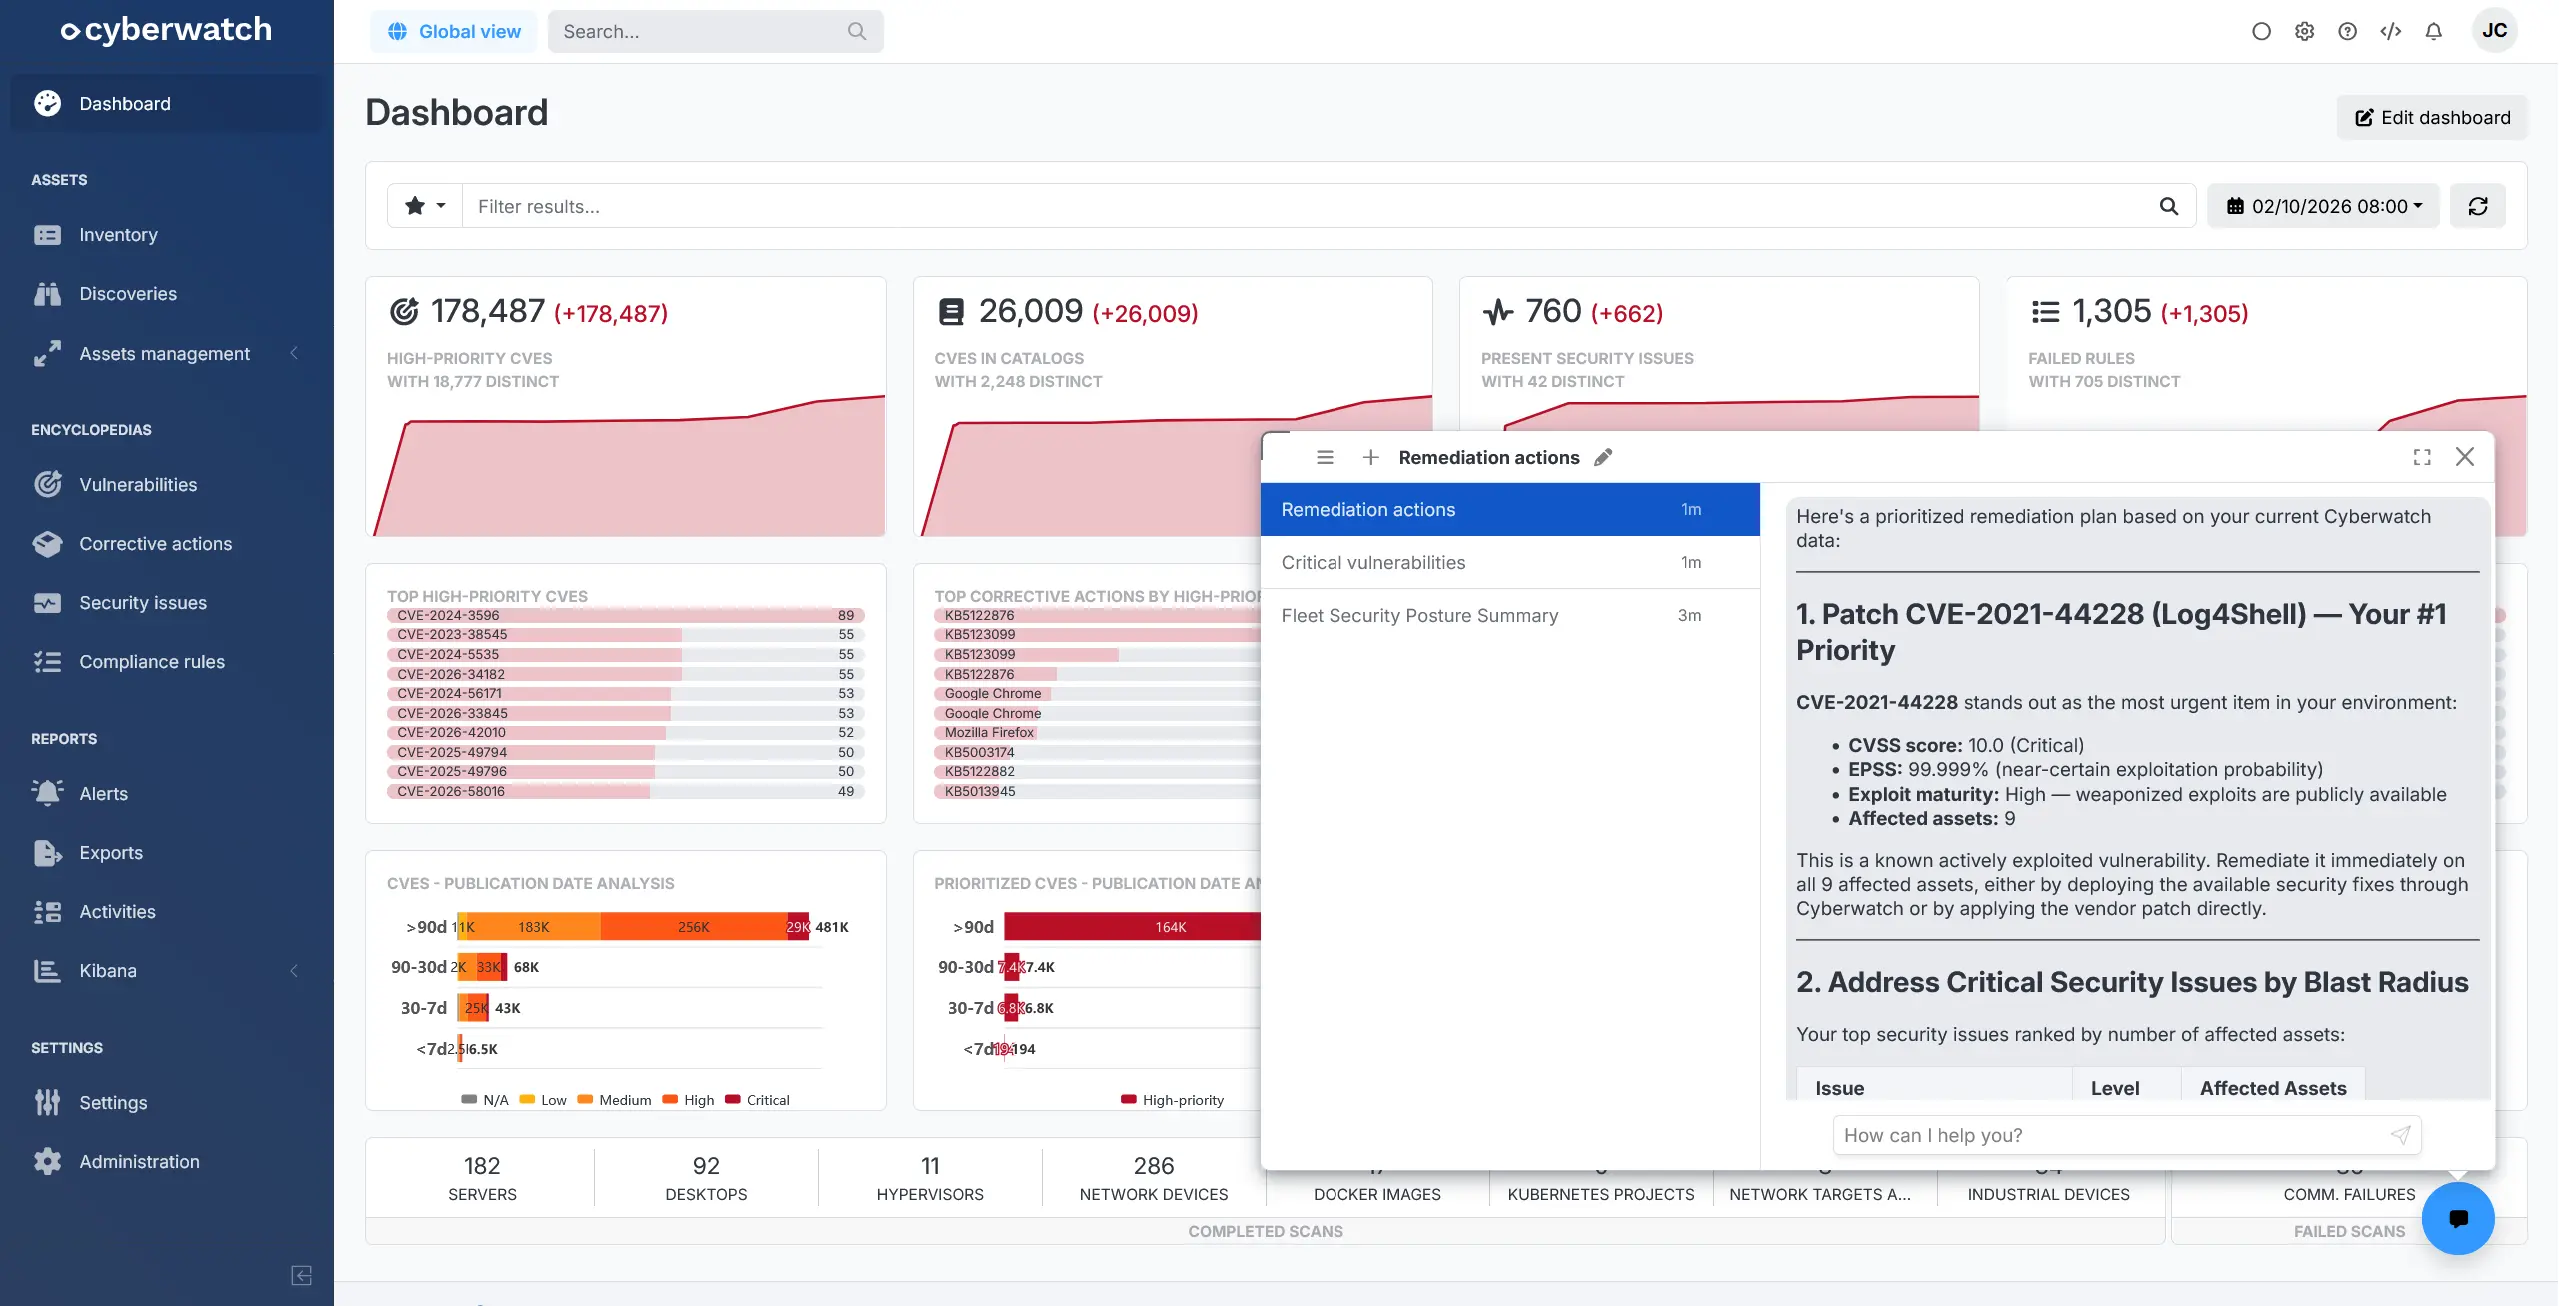
- AI: added a conversational assistant integrated into the application. It answers questions in natural language using the assets, vulnerabilities, security issues and corrective actions available to the user. It takes the current page into account, respects user permissions and keeps a conversation history (preview)
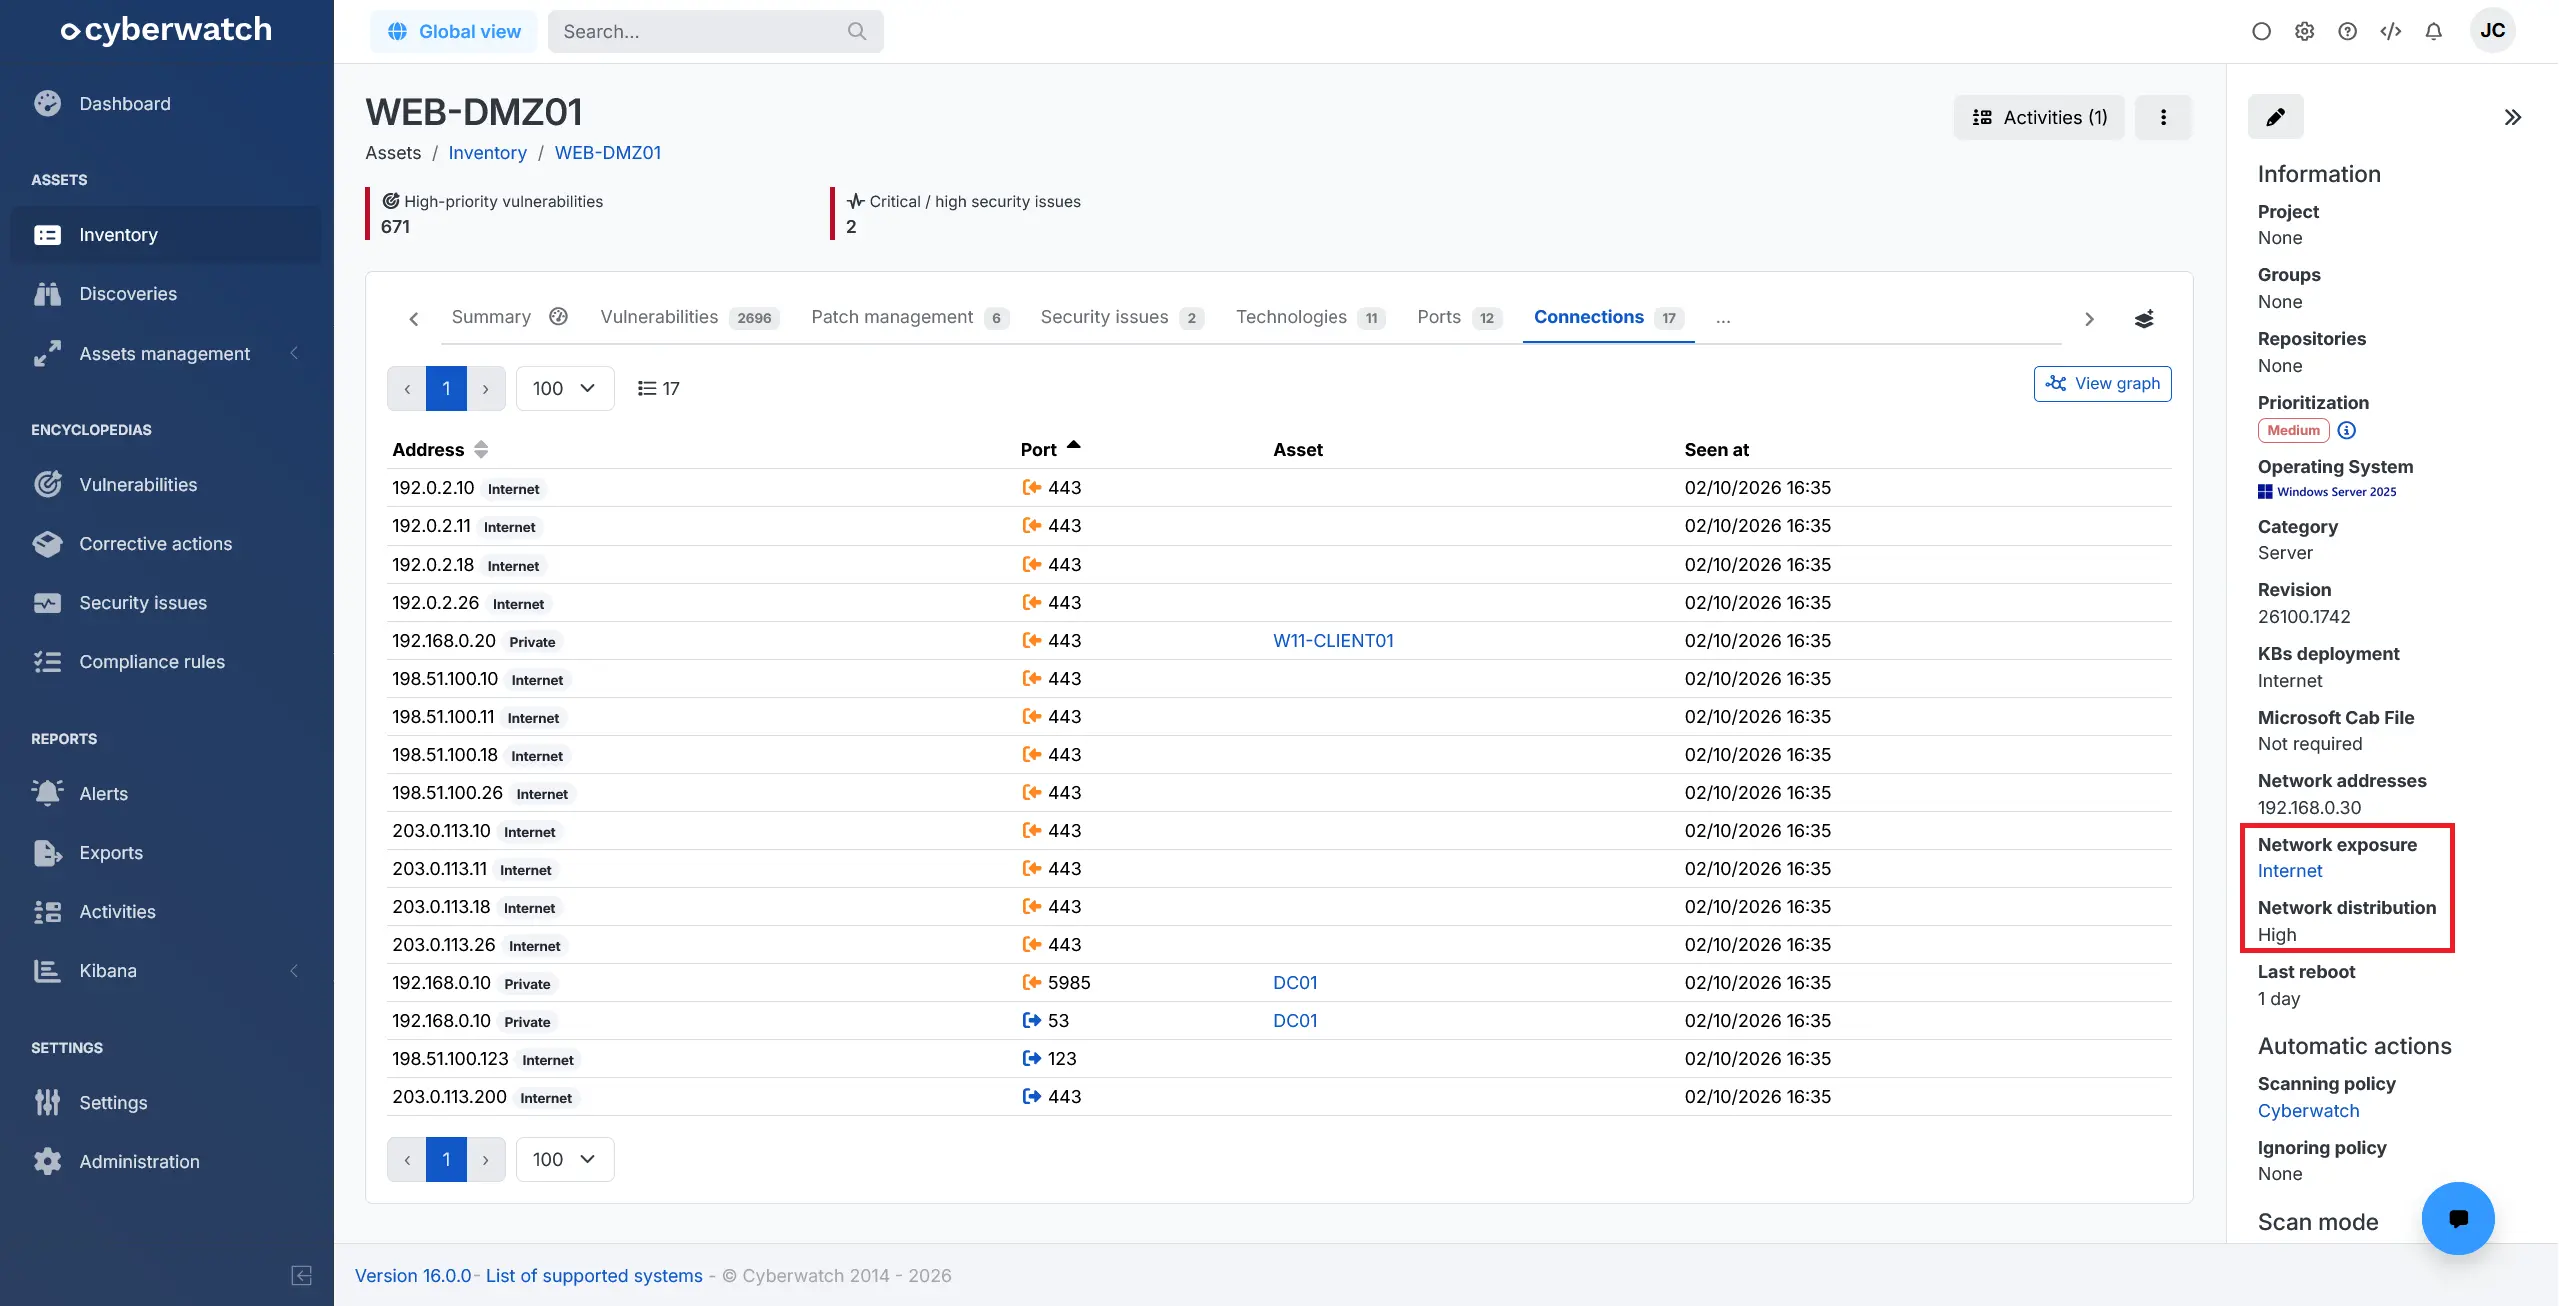
- Assets: two new indicators help position each asset within the network. Network exposure identifies where its incoming connections originate, while network distribution indicates how frequently it is contacted. This information is available in the inventory, in the asset details and in exports. Assets and vulnerabilities can also be filtered by network exposure (preview)
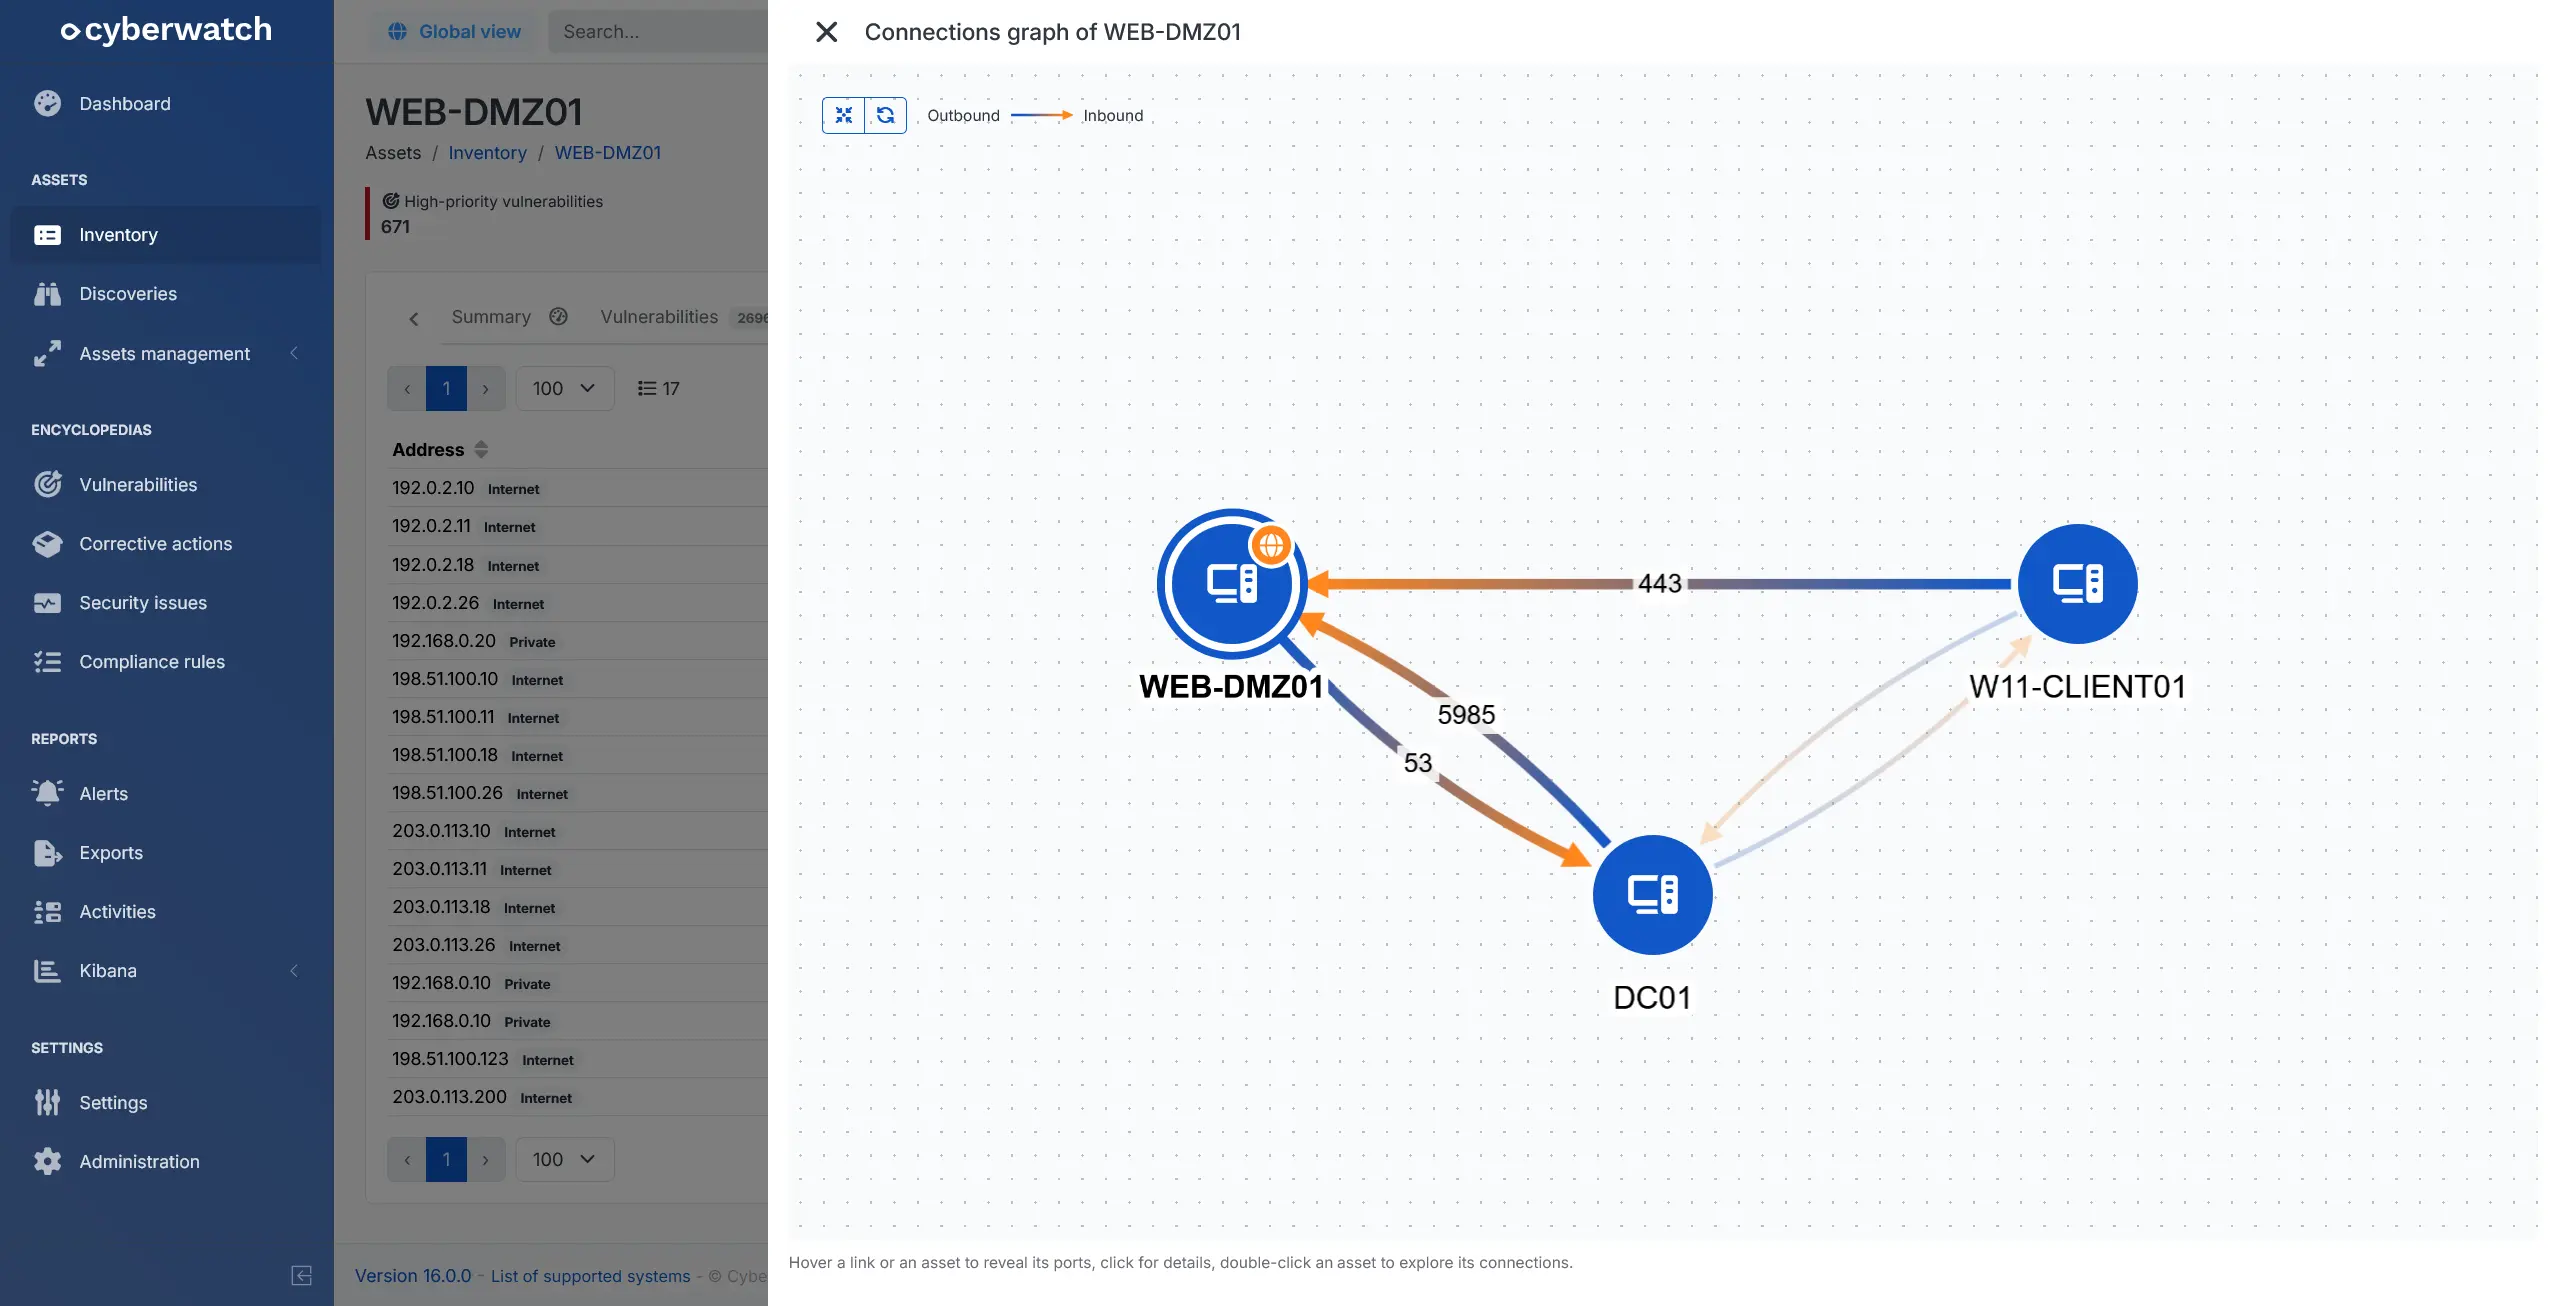
- Details of an Asset: added an interactive graph showing asset connections with the rest of the environment and highlighting exposed incoming connections. It can be opened from the “Connections” tab or from the inventory when a single asset is selected (preview)
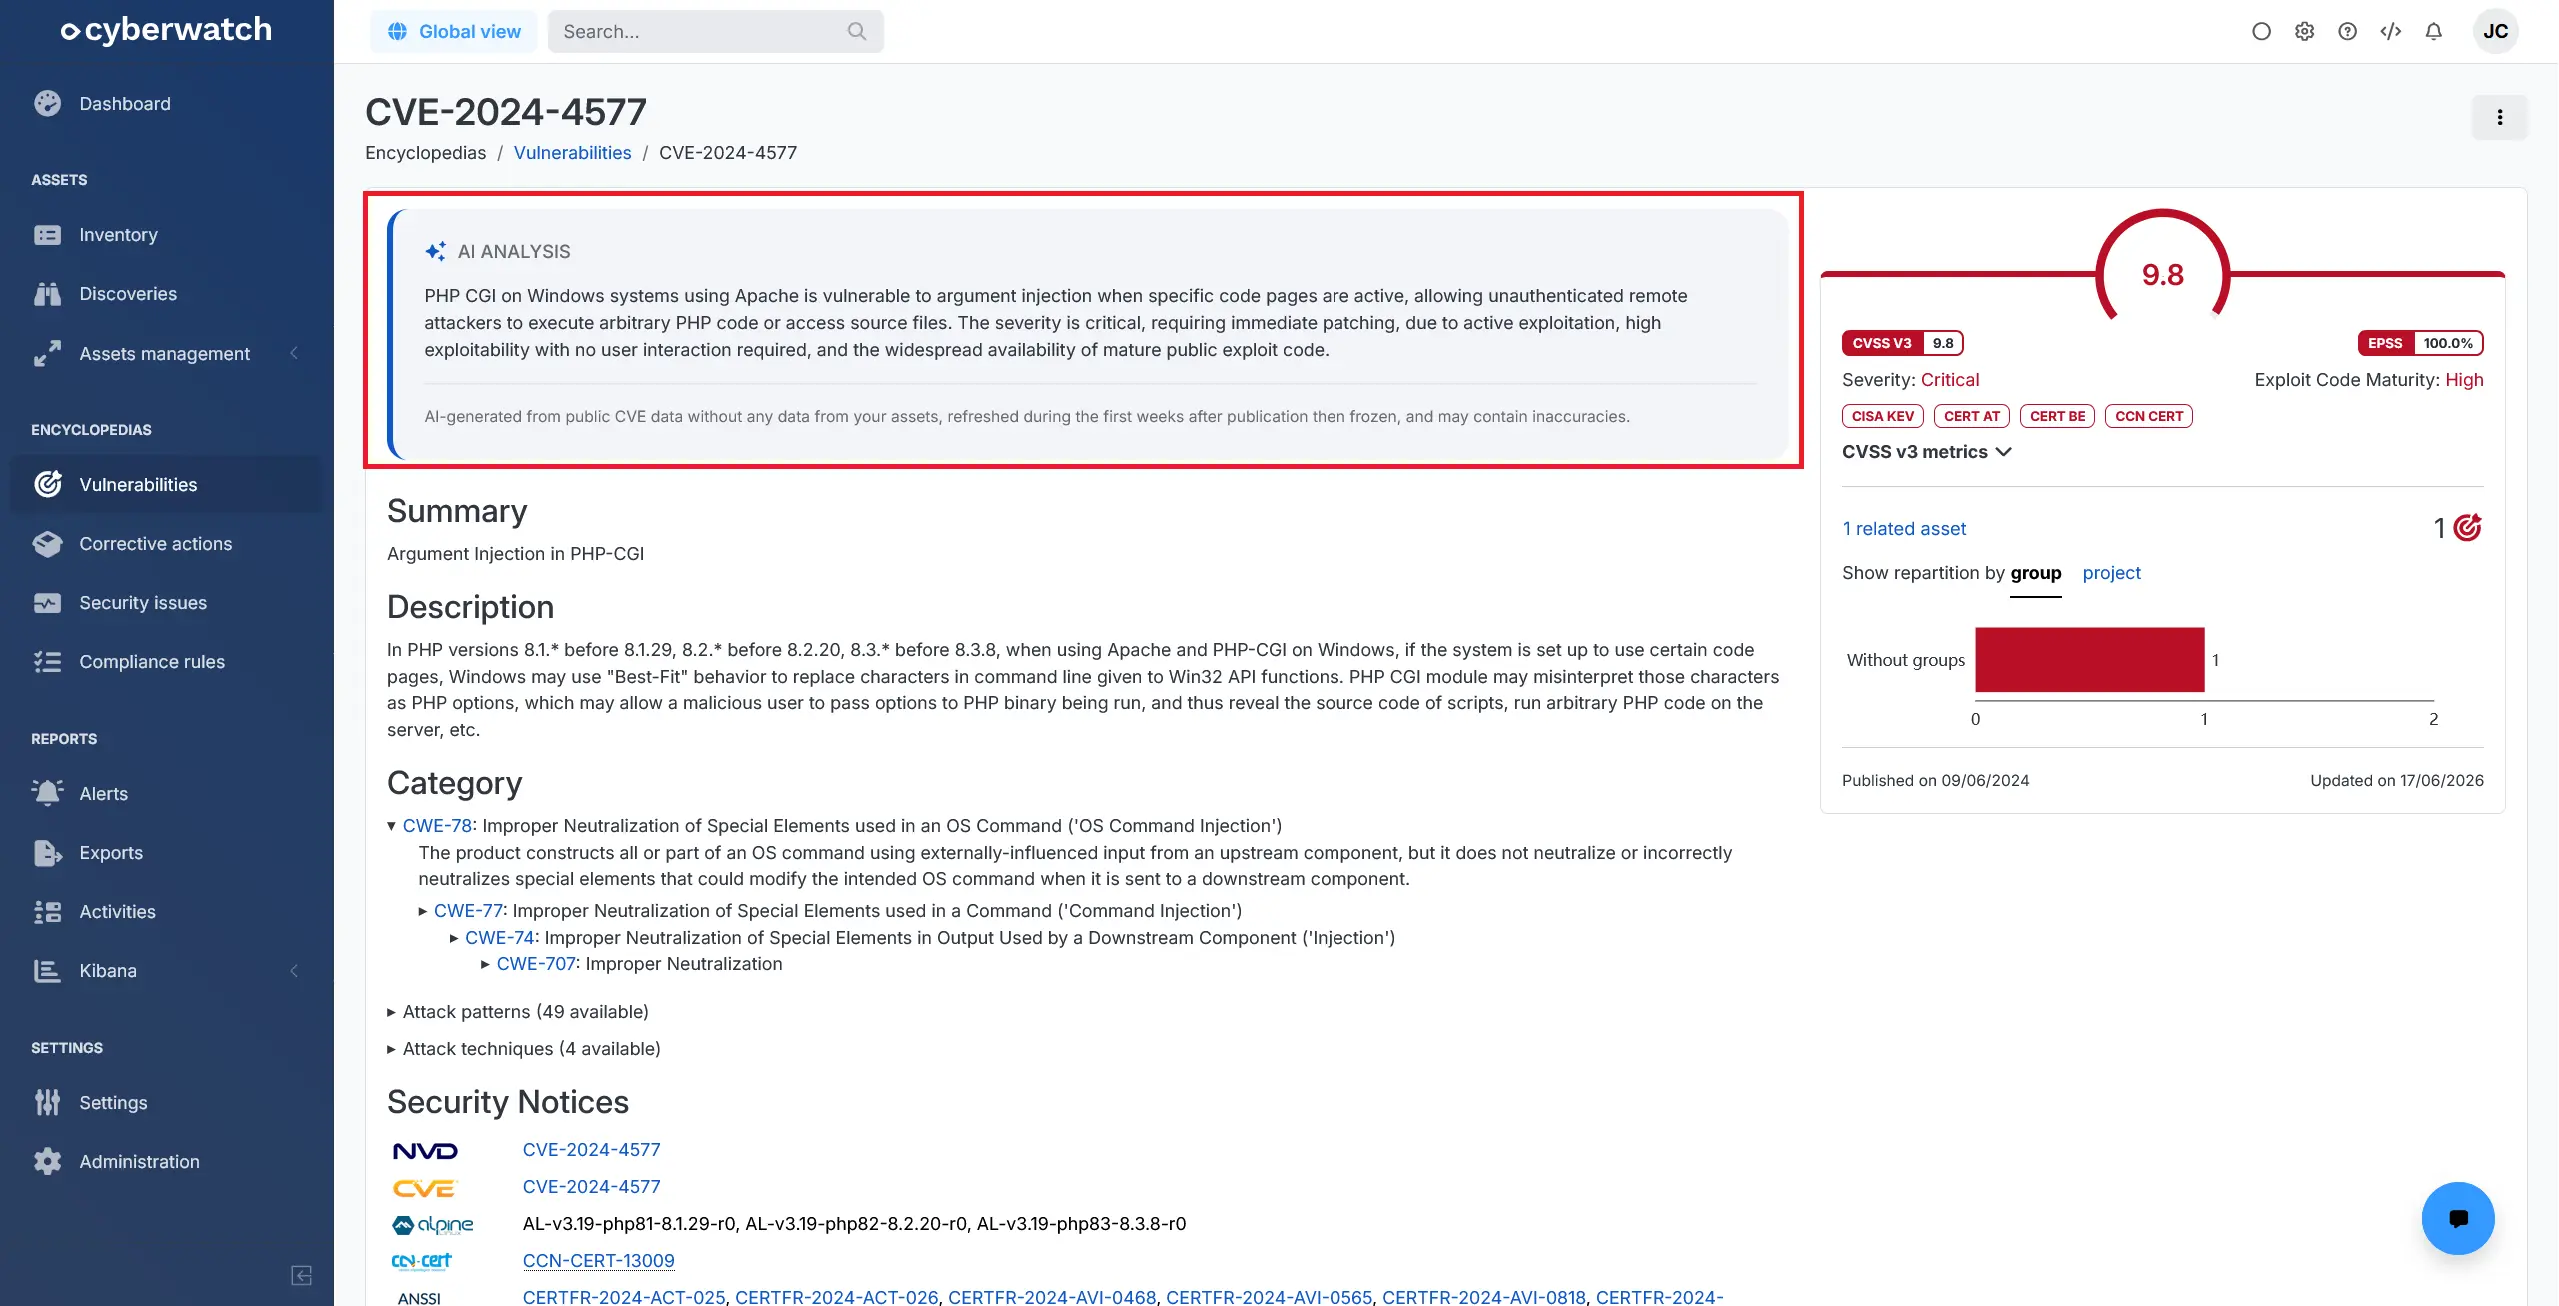
- Details of a Vulnerability: when available, an AI-generated summary highlights the essential information needed to understand and prioritize the CVE, in the user’s language or in English as a fallback. This summary is also included in email alerts (preview)
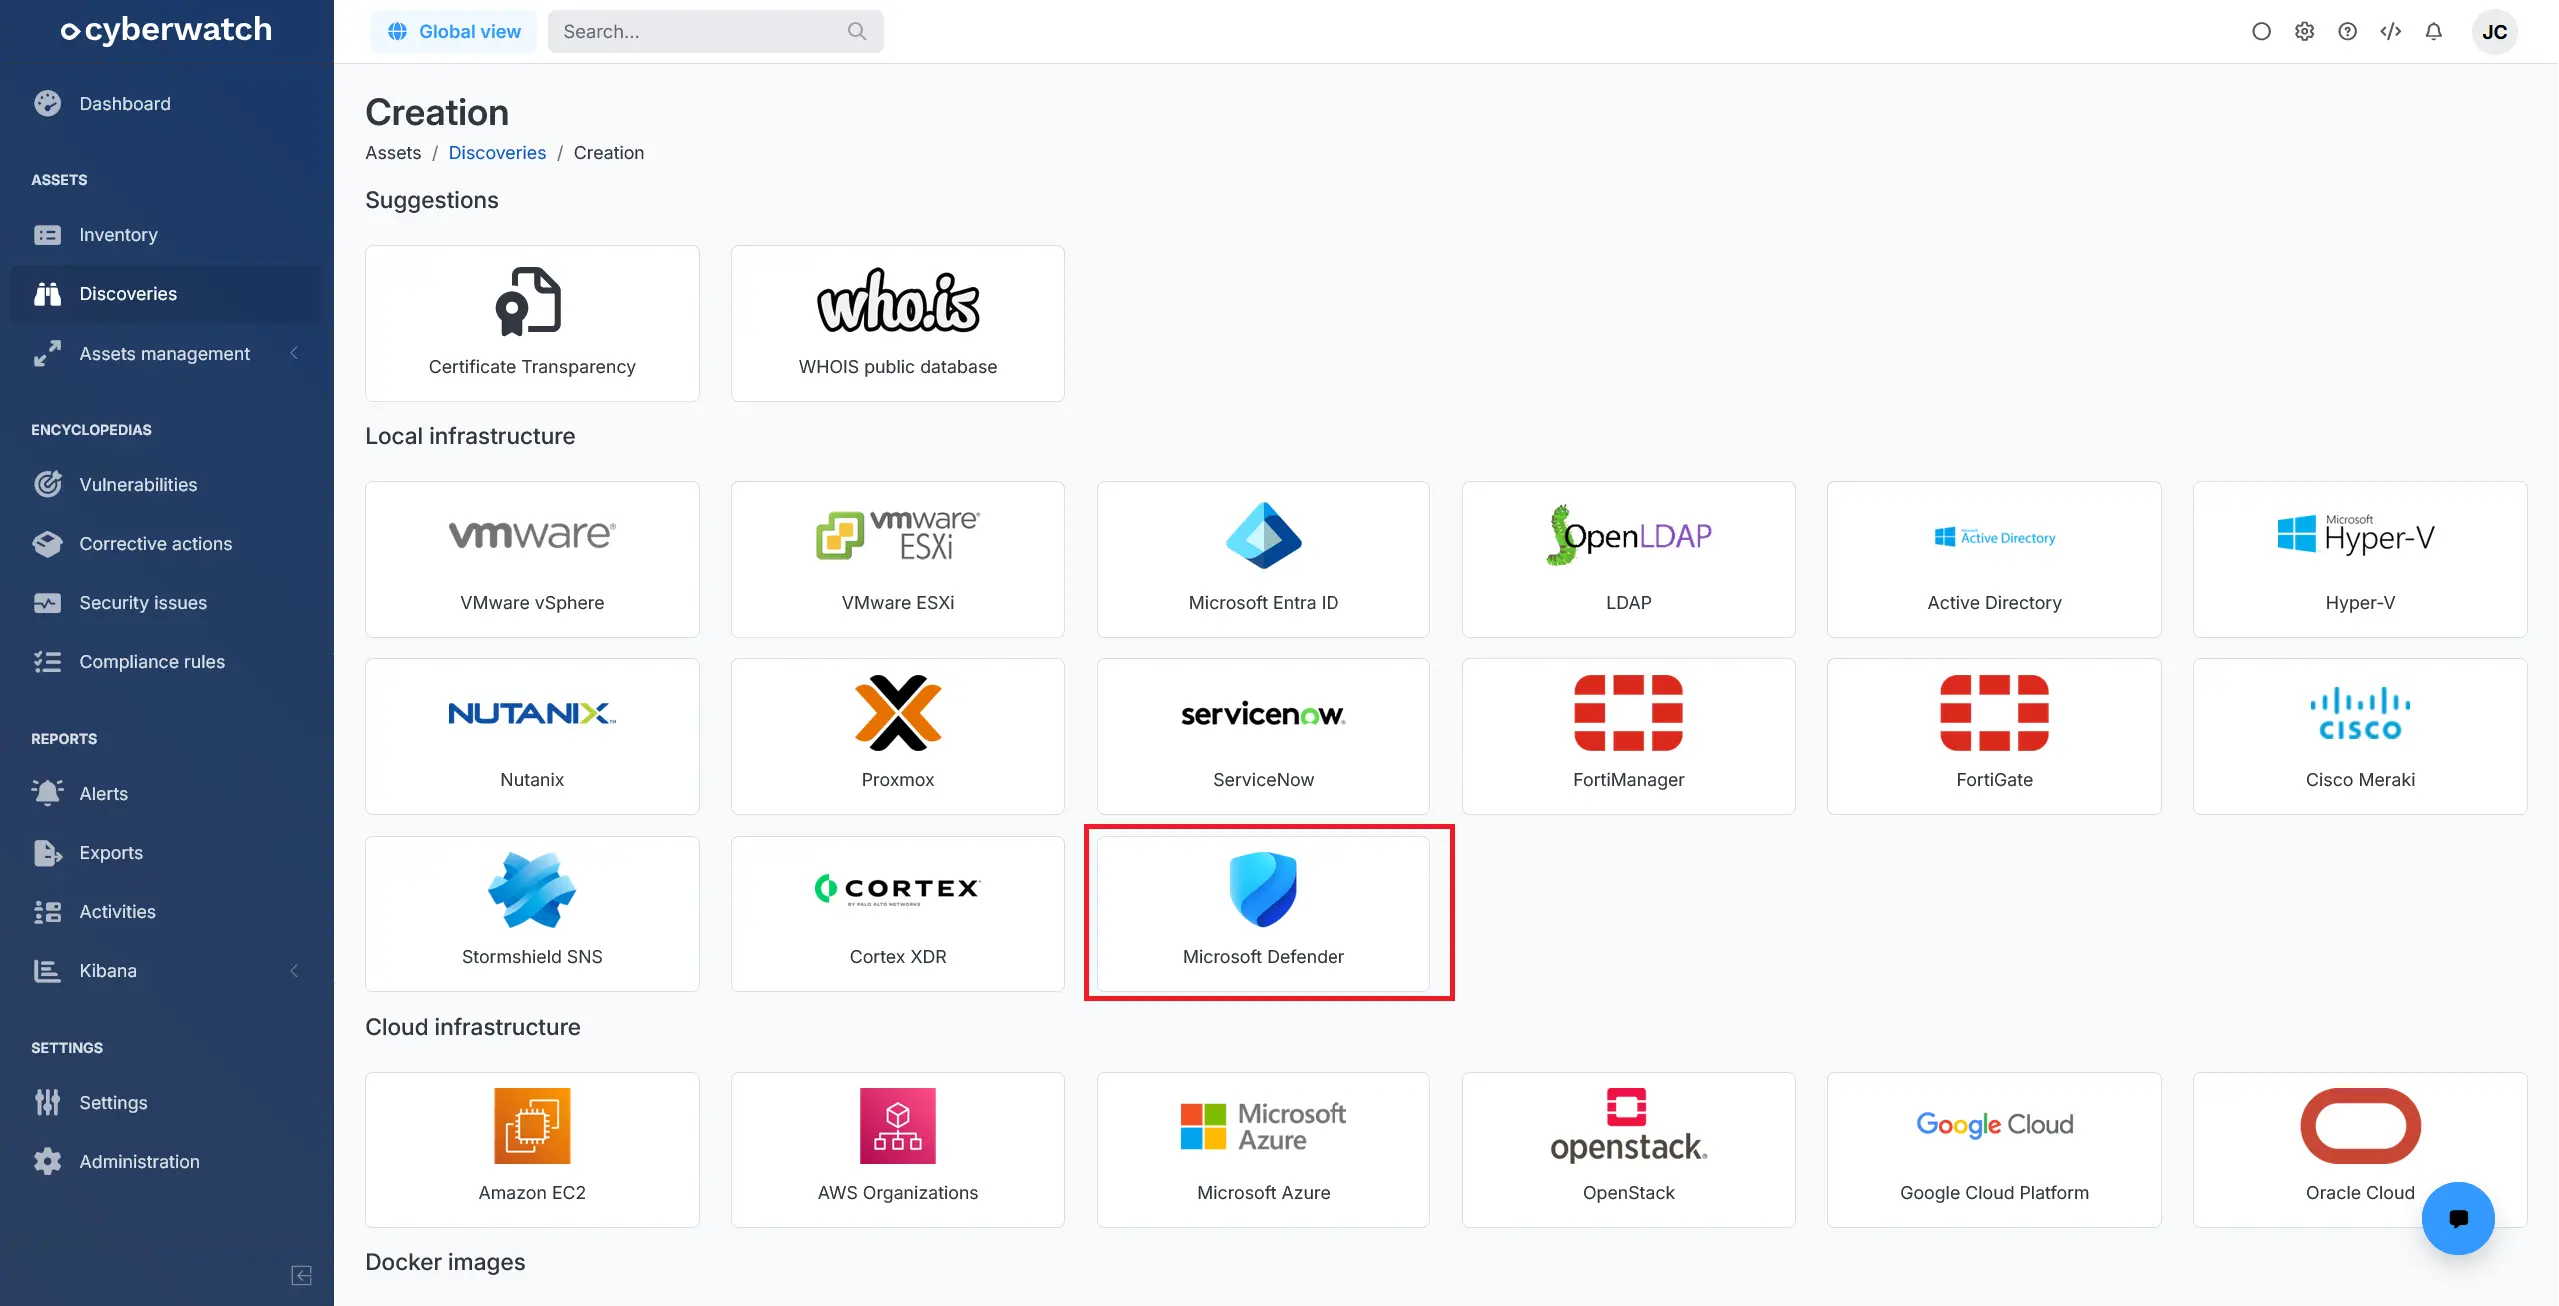
- Discoveries: added Microsoft Defender discovery. Defender-managed assets are reported with their device group and, once registered, their vulnerabilities are analyzed using the software inventory collected by Defender, with no additional agent to deploy (preview)
- Languages: the application is now available in Italian
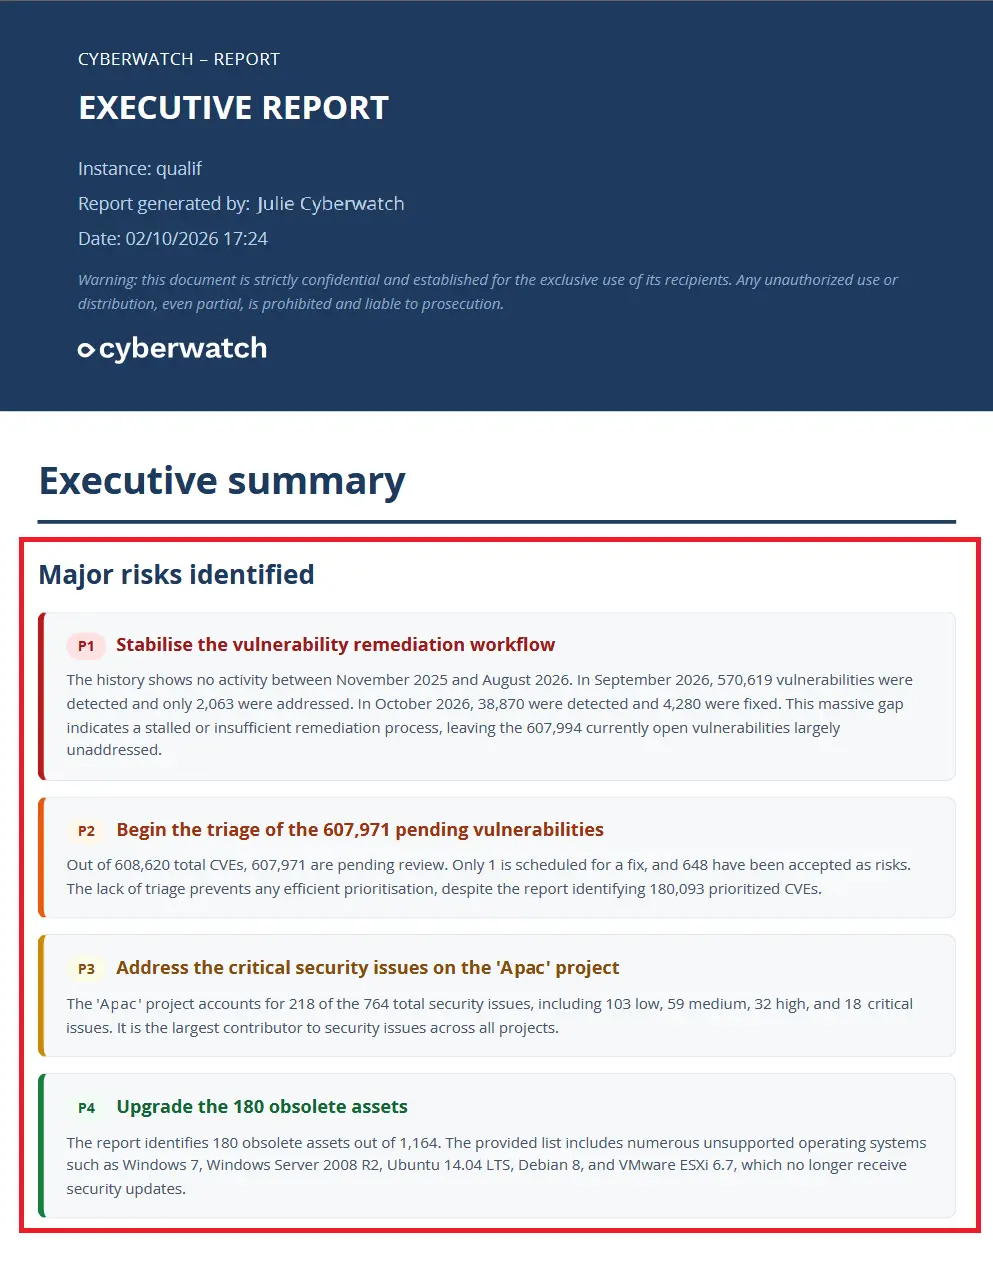
- Reports: redesigned the executive summary with new indicators, clearer charts and a better view of changes in security posture over time. When AI features are enabled, it identifies the main risks affecting the environment and provides up to four prioritized recommendations, which are also included in the email body (preview)
New features:
- Agentless connections: added support for SNMP credentials configured in CyberArk Conjur
- API: added the
/api/v3/dashboard/metricsroute to retrieve dashboard metrics - Compliance:
- Added and updated several SBP rules for Linux and Windows
- Added the CIS Benchmark for Ubuntu 26.04 LTS and updated several CIS Benchmarks, including AlmaLinux, Debian, Oracle Linux and Windows
- Scope: added end-of-life dates for GitLab
- Security issues: added detection of CPU vulnerabilities on Linux and Windows
Updated features and performance improvements:
- Activities: automatic asset deletions resulting from a discovery or following a loss of communication are now displayed in the activity history
- Alerts: redesigned emails with the instance’s custom logo and a card-based presentation of vulnerabilities, assets and patches. Readability in dark mode has also been improved
- API: the
/api/v3/servers/{id}/,/api/v3/cve_announcements/{cve_code}and/api/v3/vulnerabilities/servers/{id}routes now also return the last-updated date for each CVE associated with an asset - Cloud environment compliance: updated the AWS CIS Benchmark to version 7.0.0 and harmonized information about the affected resources
- Network targets and websites:
- A vulnerability detected on multiple variants of the same URL now generates a single security issue listing the affected URLs
- Added support for authenticated scans using a Selenium script on websites with a certificate that was not issued by a trusted certificate authority
- Performance: improved vulnerability calculation performance for application packages and Windows updates, CSV and Elasticsearch exports, and CVE searches
- Reports and exports: PDF reports and CSV exports can now be generated for corrective actions even when the assets have no associated CVEs
- Scanning engine: improved Microsoft Edge detection, including support for the Extended Stable channel
- UX: the details and AI assistant side panels are now resizable
Bugfixes:
- Agentless connections: fixed an issue with Aruba AOS-CX device detection over SNMP
- Analyses: fixed an issue that could cause high CPU usage when analyzing Linux applications
- Assets inventory: fixed an issue preventing CSV exports from being generated after filtering from the search bar
- Compliance:
- Fixed the evaluation of compliance scripts returning a “not applicable” result
- Ignored rules are no longer included in the counters and filters of the compliance rules encyclopedia
- Network targets and websites: fixed nonexistent pages being reported when a website redirects to another URL
- Scanning engine:
- Fixed a patched-version detection issue for VMware ESXi and vCenter
- Fixed Adobe Acrobat Reader vulnerability detection
- Fixed vulnerability detection related to the running kernel on Ubuntu 24.04 and 26.04
15.10 (2026-09-15)
New features:
- Authentication provider: added the ability to automatically assign projects based on LDAP user groups
- Dashboard:
- Each widget can now be associated with a saved query to display data for a specific scope
- Multiple instances of the same widget can now be added for greater dashboard customization
- Details of an Asset: Windows registry keys associated with installed applications are now reported
- Prioritization policies: added the ability to set a minimum exploit level in a policy
- Scope:
- Added support for Aruba ClearPass devices
- Added support for PaperCut MF and NG
- Added support for Proxmox VE
- Added support for QNAP QTS devices
- Added support for TheGreenBow VPN Enterprise
- UX: one-click copy for code blocks
Updated features and performance improvements:
- Analyses: improved SAP Notes handling when calculating vulnerabilities
- API: the
/api/v3/cve_announcementsroutes now include the vulnerability summary - Cloud environment compliance: updated Oracle Cloud Infrastructure CIS Benchmark
- Compliance: improved check reliability for SBP and ICS rules on Windows
- Details of an Asset:
- From the Patch management tab, you can set a reactivation date for vulnerabilities associated with the selected patches
- Port listening addresses are now reported
- Discovered assets: Nmap and Palo Alto Cortex XDR discoveries report the device type of detected assets
- Exports: the device type is now included in CSV exports of discovered assets
- Projects: asset rules can also be defined at the project level
- Scanning engine:
- Improved Microsoft .NET Framework vulnerability detection by better accounting for cumulative updates
- Improved vulnerability detection for Mozilla Thunderbird ESR installed via Snap
- Improved vulnerability detection on Check Point devices
- Security issues encyclopedia: improved security issues bulk deletion
Bugfixes:
- Agentless connections: fixed an identification issue for Cisco NX-OS via SNMP
- Assets inventory: fixed an issue with prioritization policy filtering for users restricted to projects
- Compliance:
- Fixed an issue preventing results from being displayed when analyzing domain-joined Windows assets
- Fixed an issue preventing some SCAP benchmark rules from being supported when an additional check was detected
- Corrective actions:
- Fixed an issue preventing patches from being deployed from the side panel
- Fixed an issue preventing the deployment of some Red Hat packages
- Dashboard: fixed a tooltip display issue affecting some charts
- Exports: fixed an inconsistency in corrective action status when exporting assets associated with a CVE
- Scanning engine: fixed TeamViewer vulnerability detection
15.9 (2026-07-27)
Highlighted features:
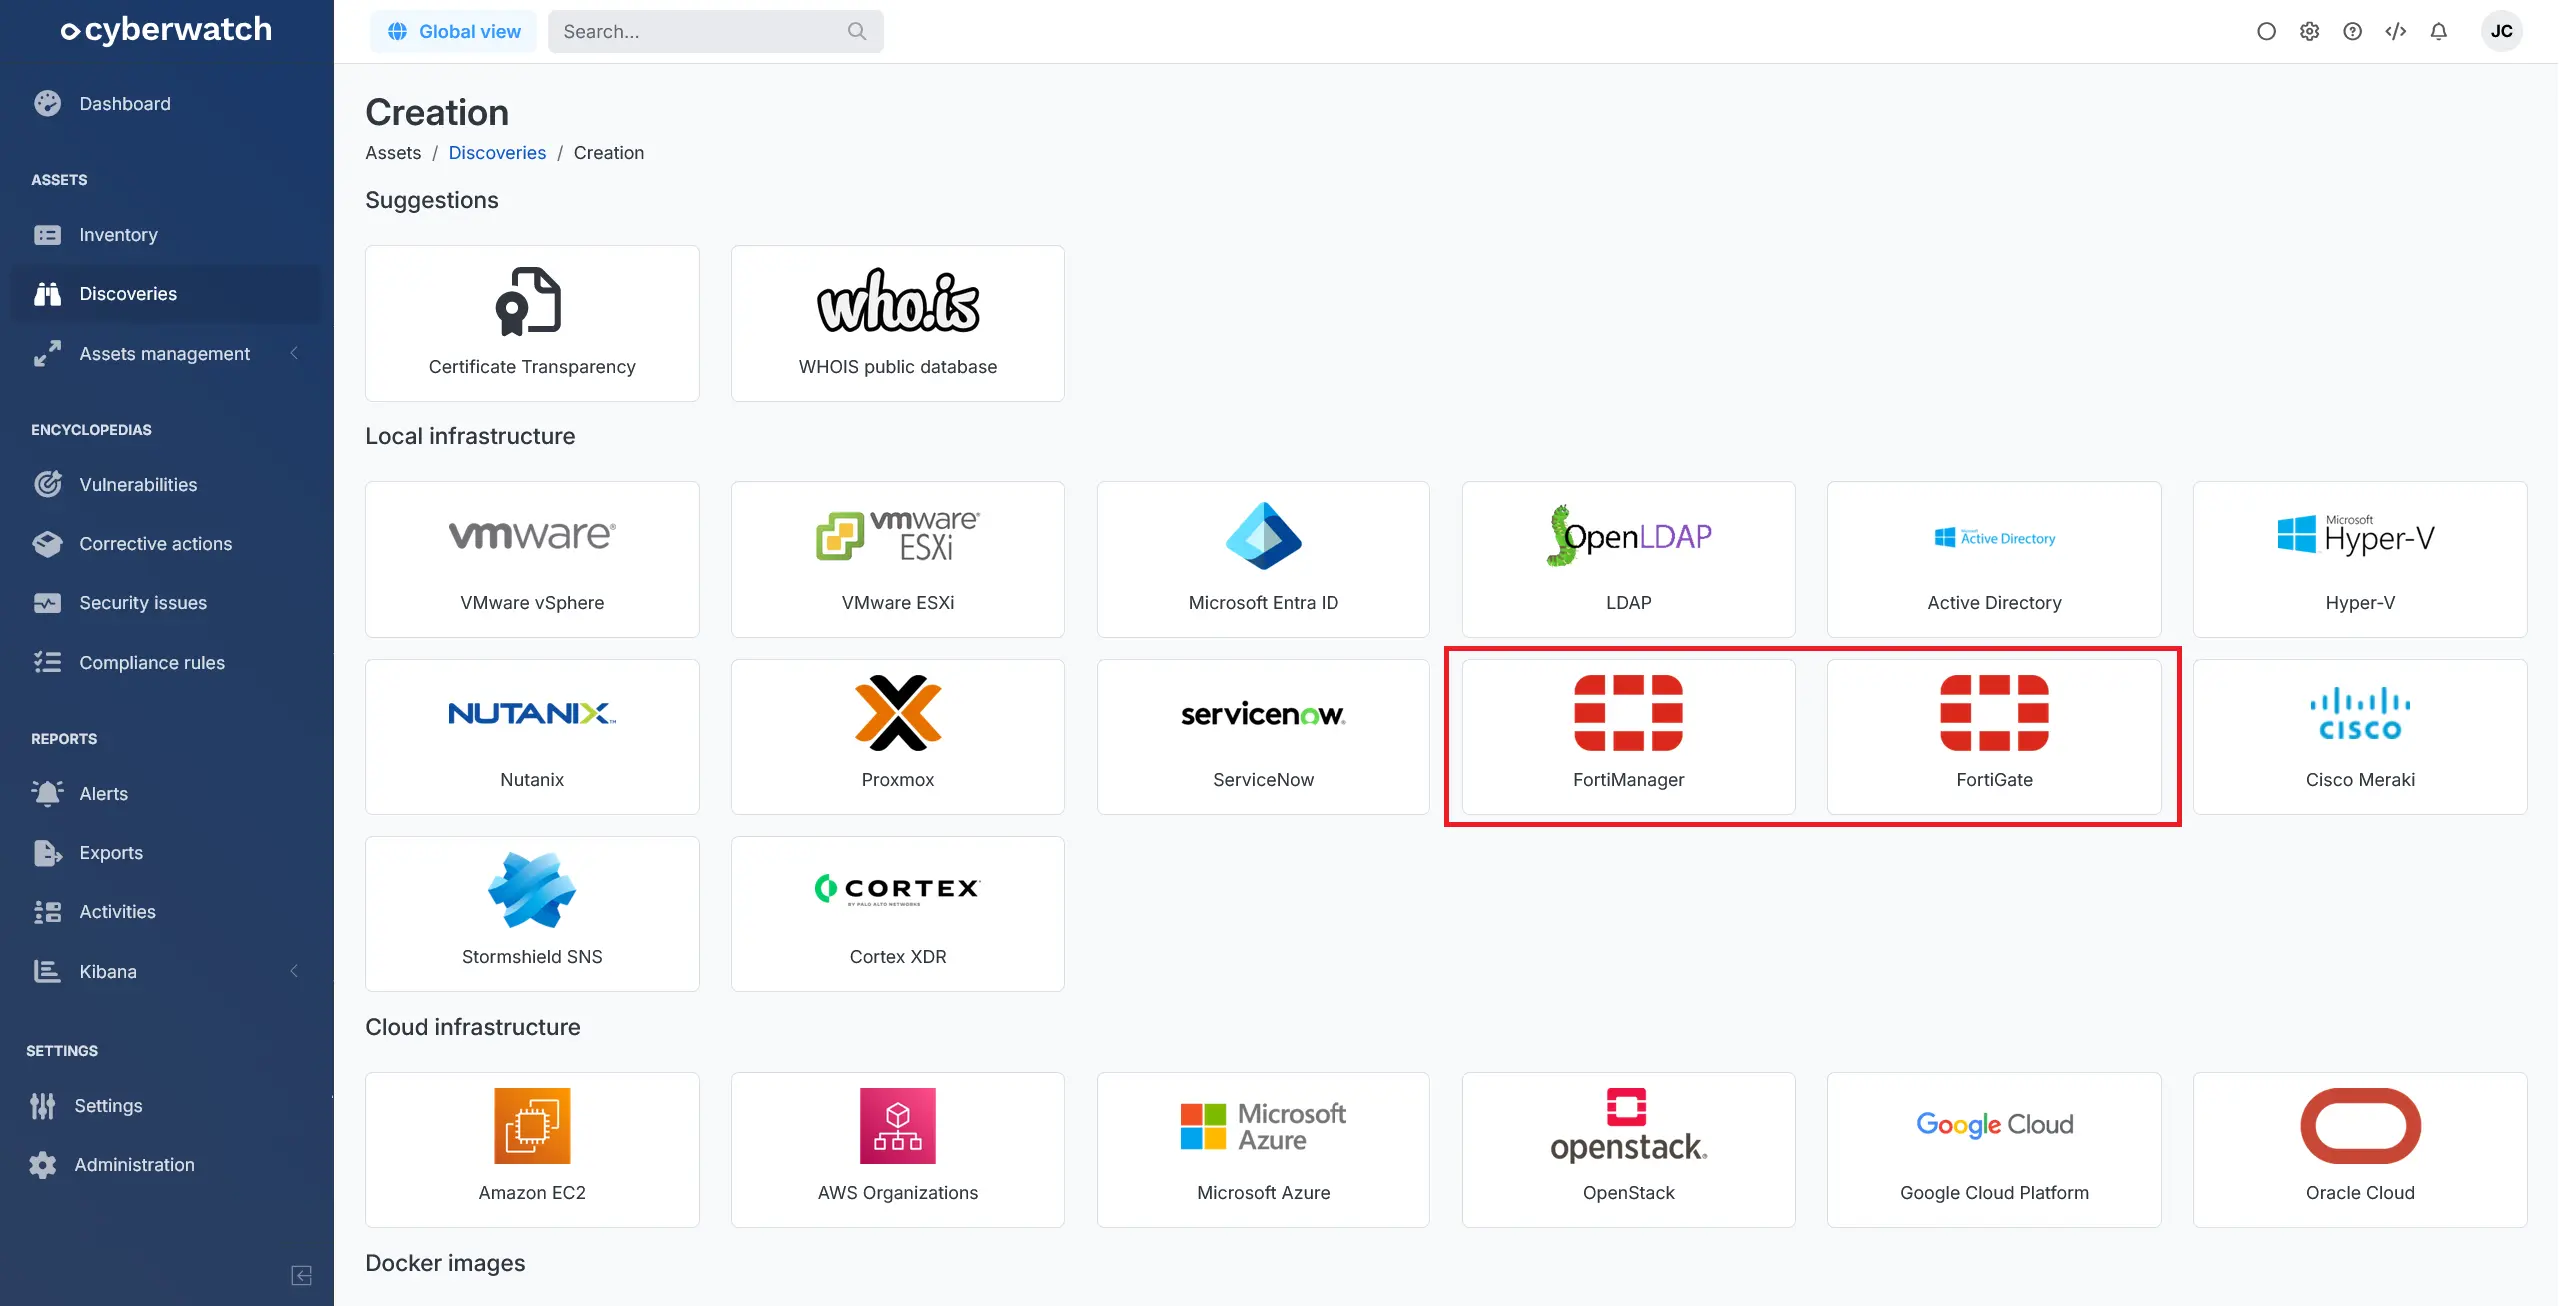
- Discoveries: added FortiManager discovery to report devices managed by a FortiManager. Fortinet discovery is renamed to FortiGate to distinguish the two discovery types (preview)
- Prioritization policies: support for EPSS v5 in the vulnerability prioritization method called “3D prioritization”
New features:
- Discovered assets: added the ability to register assets from a Palo Alto Cortex XDR discovery as Cortex XDR agents
- Discoveries:
- Added JFrog Artifactory discovery
- VMware vSphere discoveries now support selecting an operating system family
- Discoveries and Agentless connections:
- Added Kubernetes discovery for clusters defined in a kubeconfig file
- Kubernetes projects can now be created using a kubeconfig file
Updated features and performance improvements:
- Agents: added the ability to force-start an analysis when another one is still reported as running
- Alerts: alert management has been removed from the “Settings” menu but remains accessible from the “Alerts” menu
- Compliance:
- Compliance scans are automatically re-run after modifying a regular expression in a custom compliance rule
- Updated several CIS Benchmarks, including Amazon EKS and Azure AKS
- Network targets and websites: screenshots taken before and after authentication are now displayed in the “Summary” tab of the details page of an asset, when available
- Prioritization policies: the Netherlands NCSC catalog can also be used for vulnerability prioritization
- Scanning engine:
- Improved Microsoft Defender vulnerability detection with support for the Malware Protection Engine
- Improved Mozilla Thunderbird vulnerability detection with better support for ESR versions
- Improved vulnerability analysis on Linux assets to better reflect the kernel currently running
- Improved vulnerability detection by more accurately accounting for operating system information from the NVD
- Improved vulnerability detection on SonicWall devices
- UX: improved the display of pagination and selection in tables
Bugfixes:
- Assets inventory:
- Fixed CVE filtering to display only assets actually affected by the searched vulnerability
- Fixed group filtering for users restricted to projects
- Compliance:
- Fixed a performance issue that could cause high CPU usage when running rule SBP-WIN-04-006
- Fixed an issue preventing compliance results from being displayed when analyzing certain Windows rules
- Discovered assets: fixed an issue that could prevent Docker images from Amazon ECR and EKS discoveries from being registered
- Exports: fixed an issue preventing recipients from being searched when configuring a scheduled export
- Scanning engine:
- Fixed a detection issue on Cisco Secure Client
- Fixed a detection issue on Oracle Java
15.8 (2026-06-18)
As of this release, group-based access management has been removed. Projects are now the only way to manage permissions, a feature introduced in version 14.7.
Highlighted features:
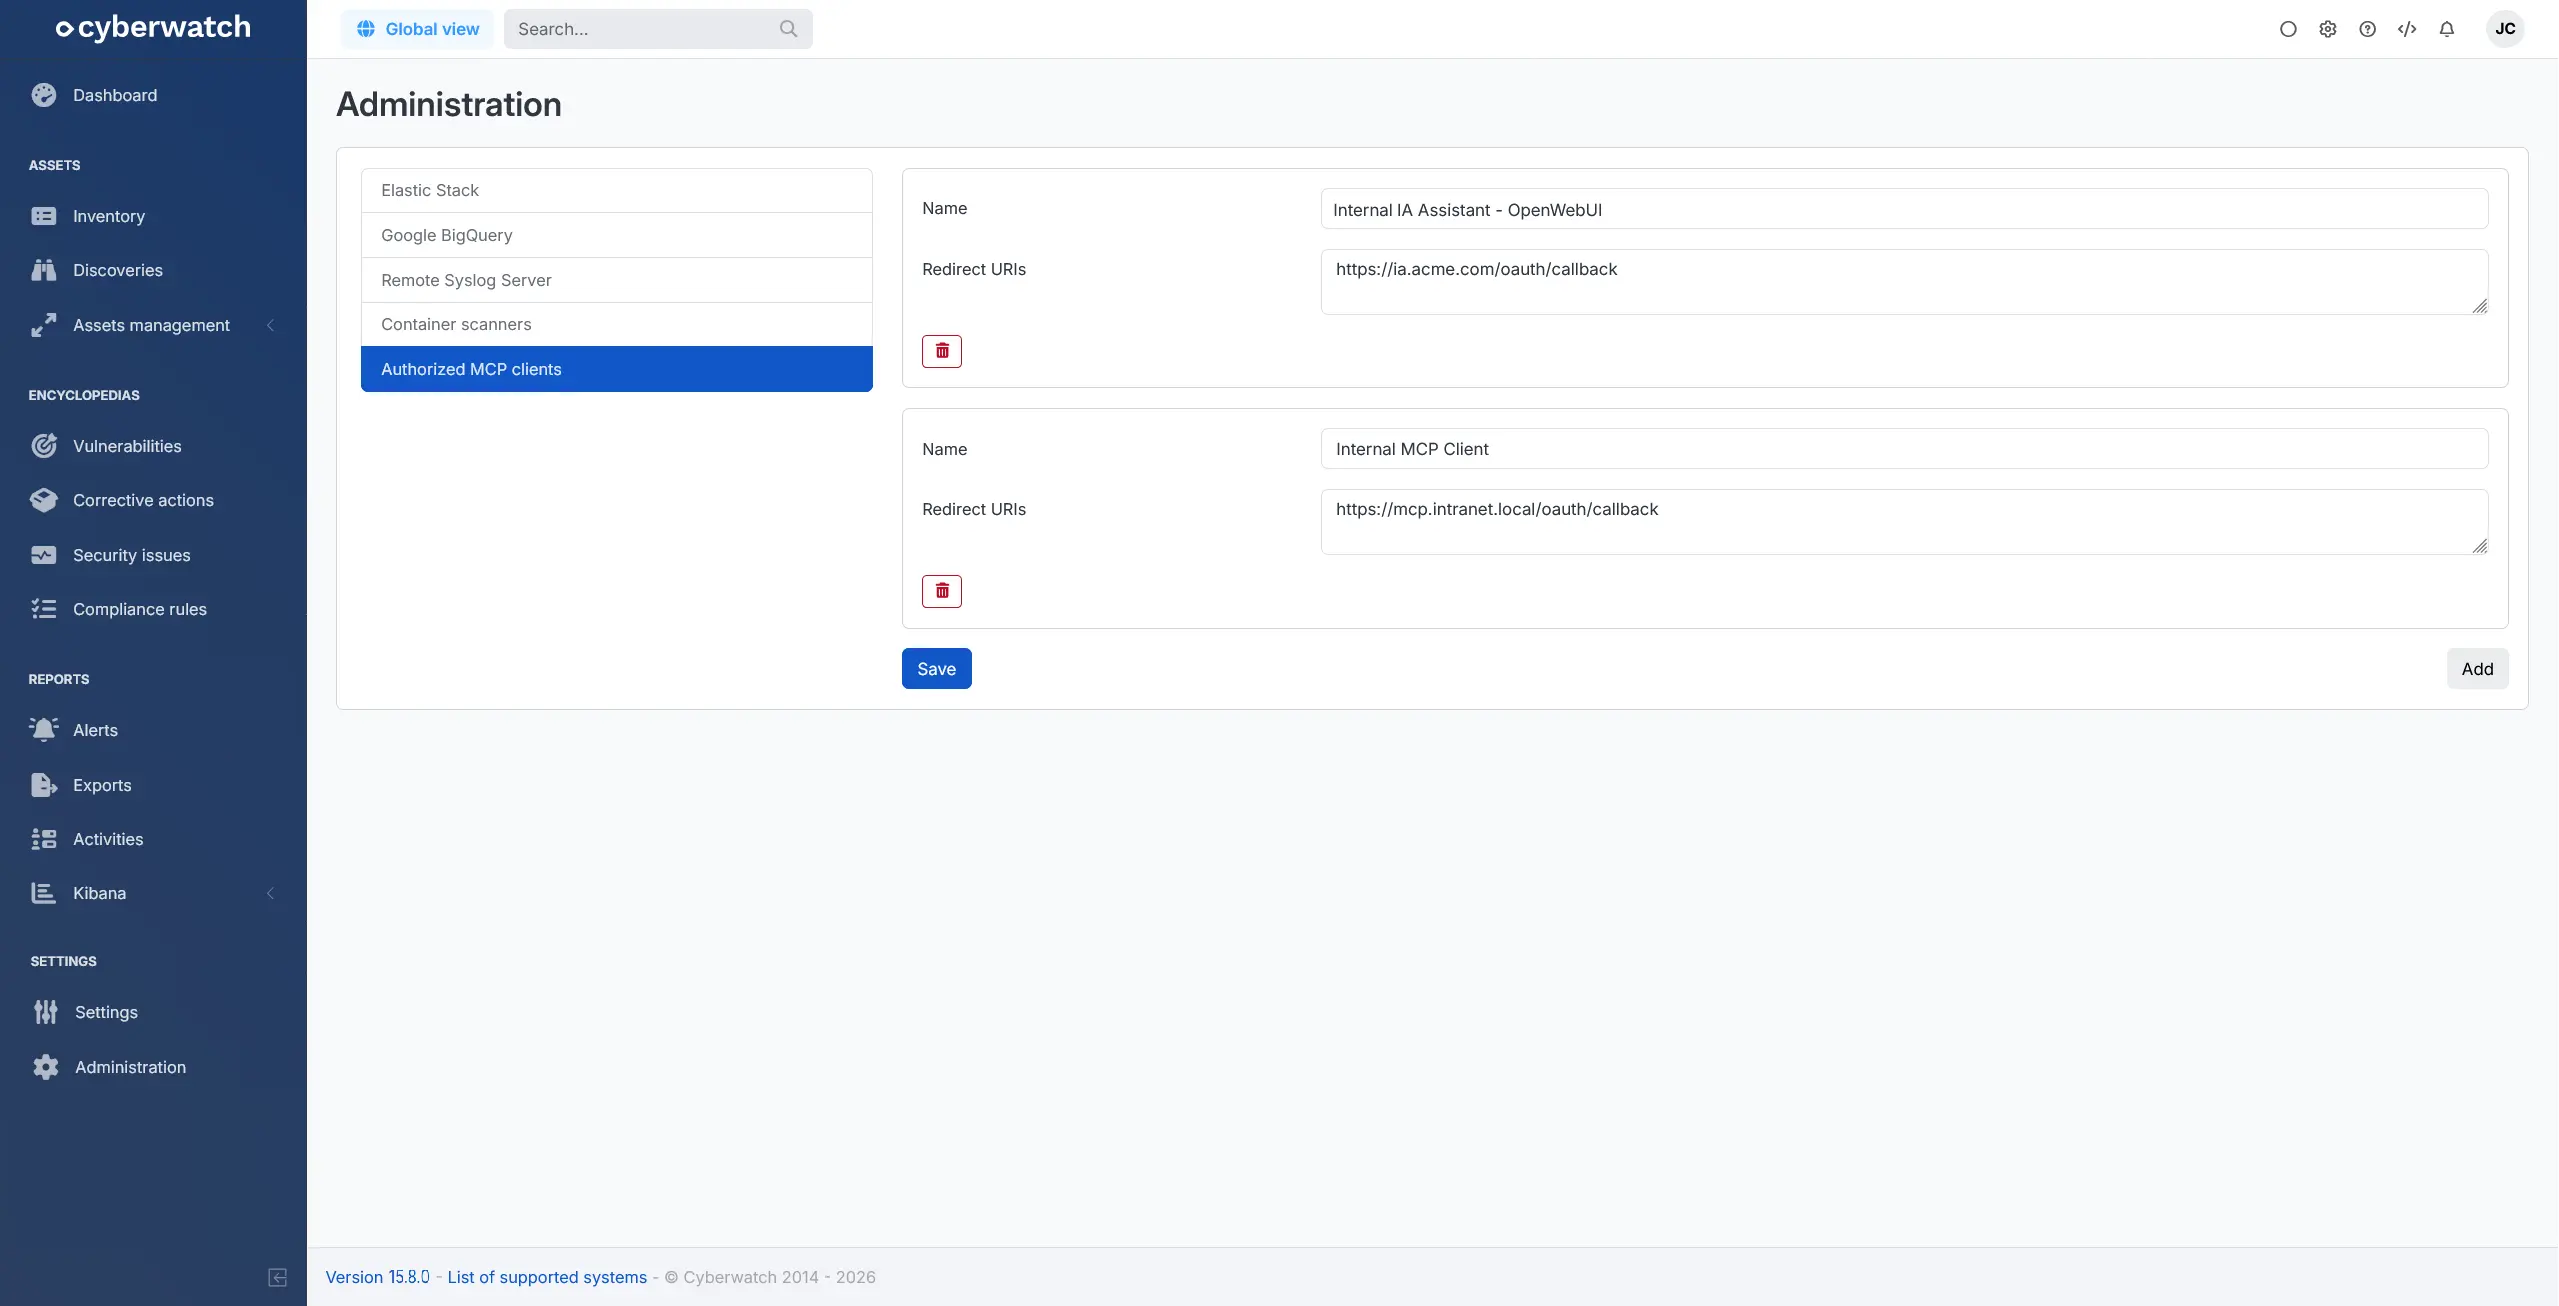
- AI: added the ability to configure custom MCP clients to make it easier to integrate tools compatible with the MCP server (preview)
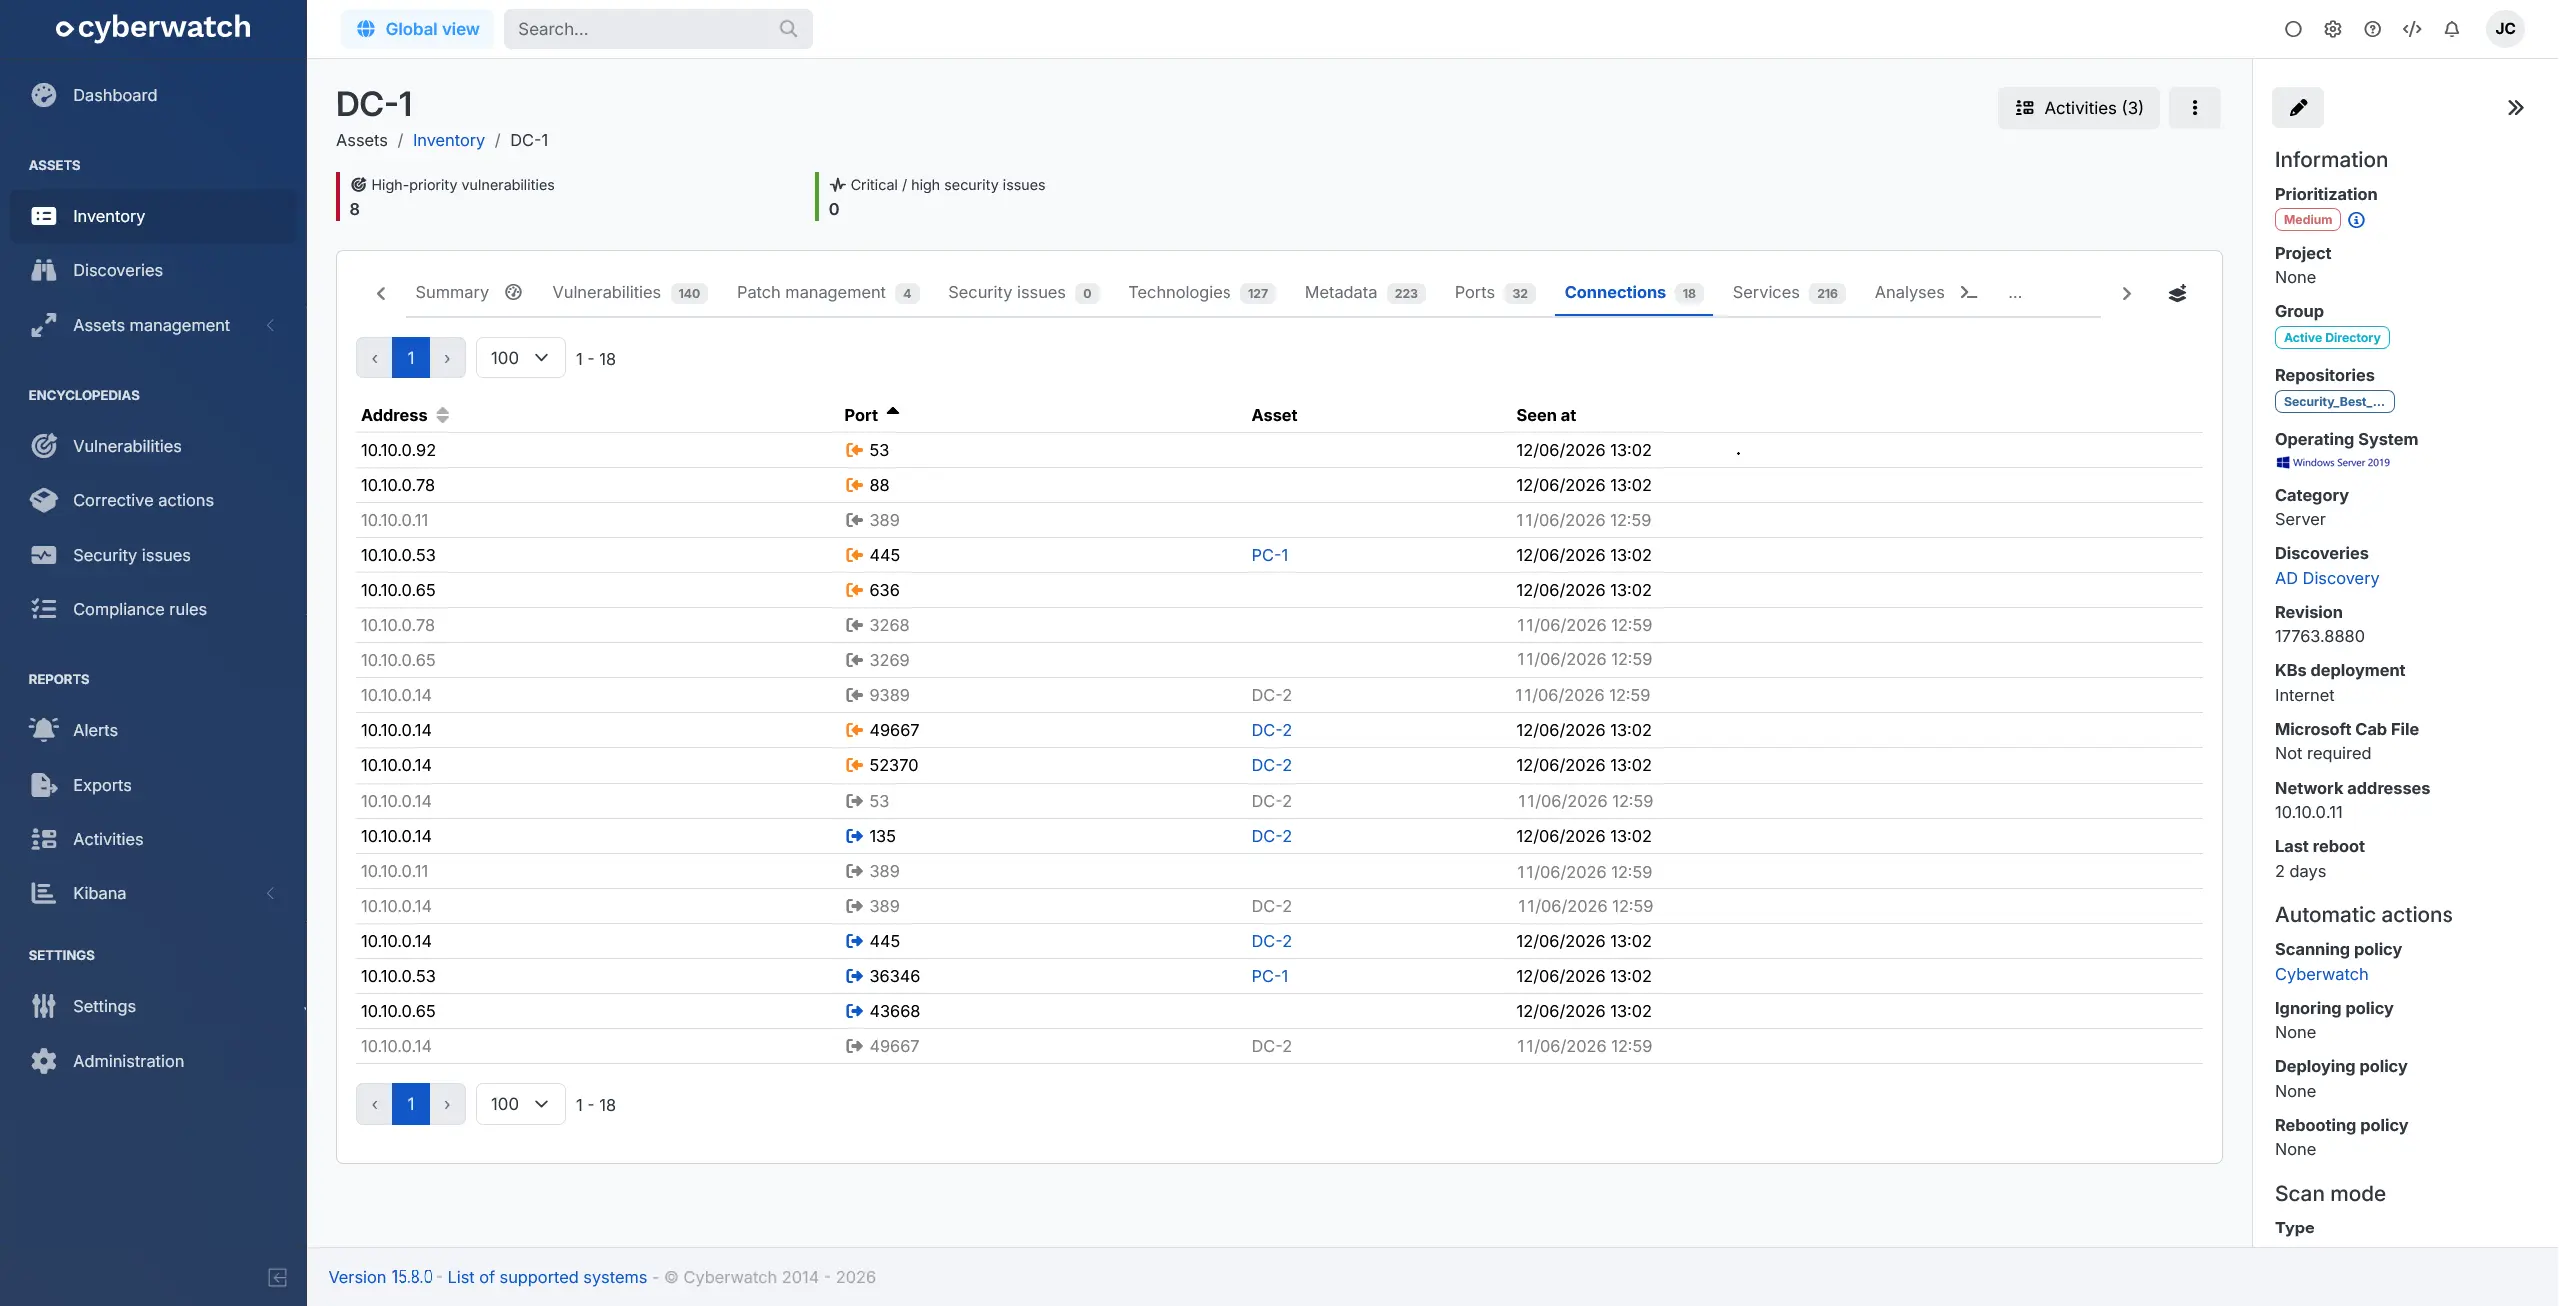
- Details of an Asset: added a new tab displaying observed network connections to make asset communication analysis easier (preview)
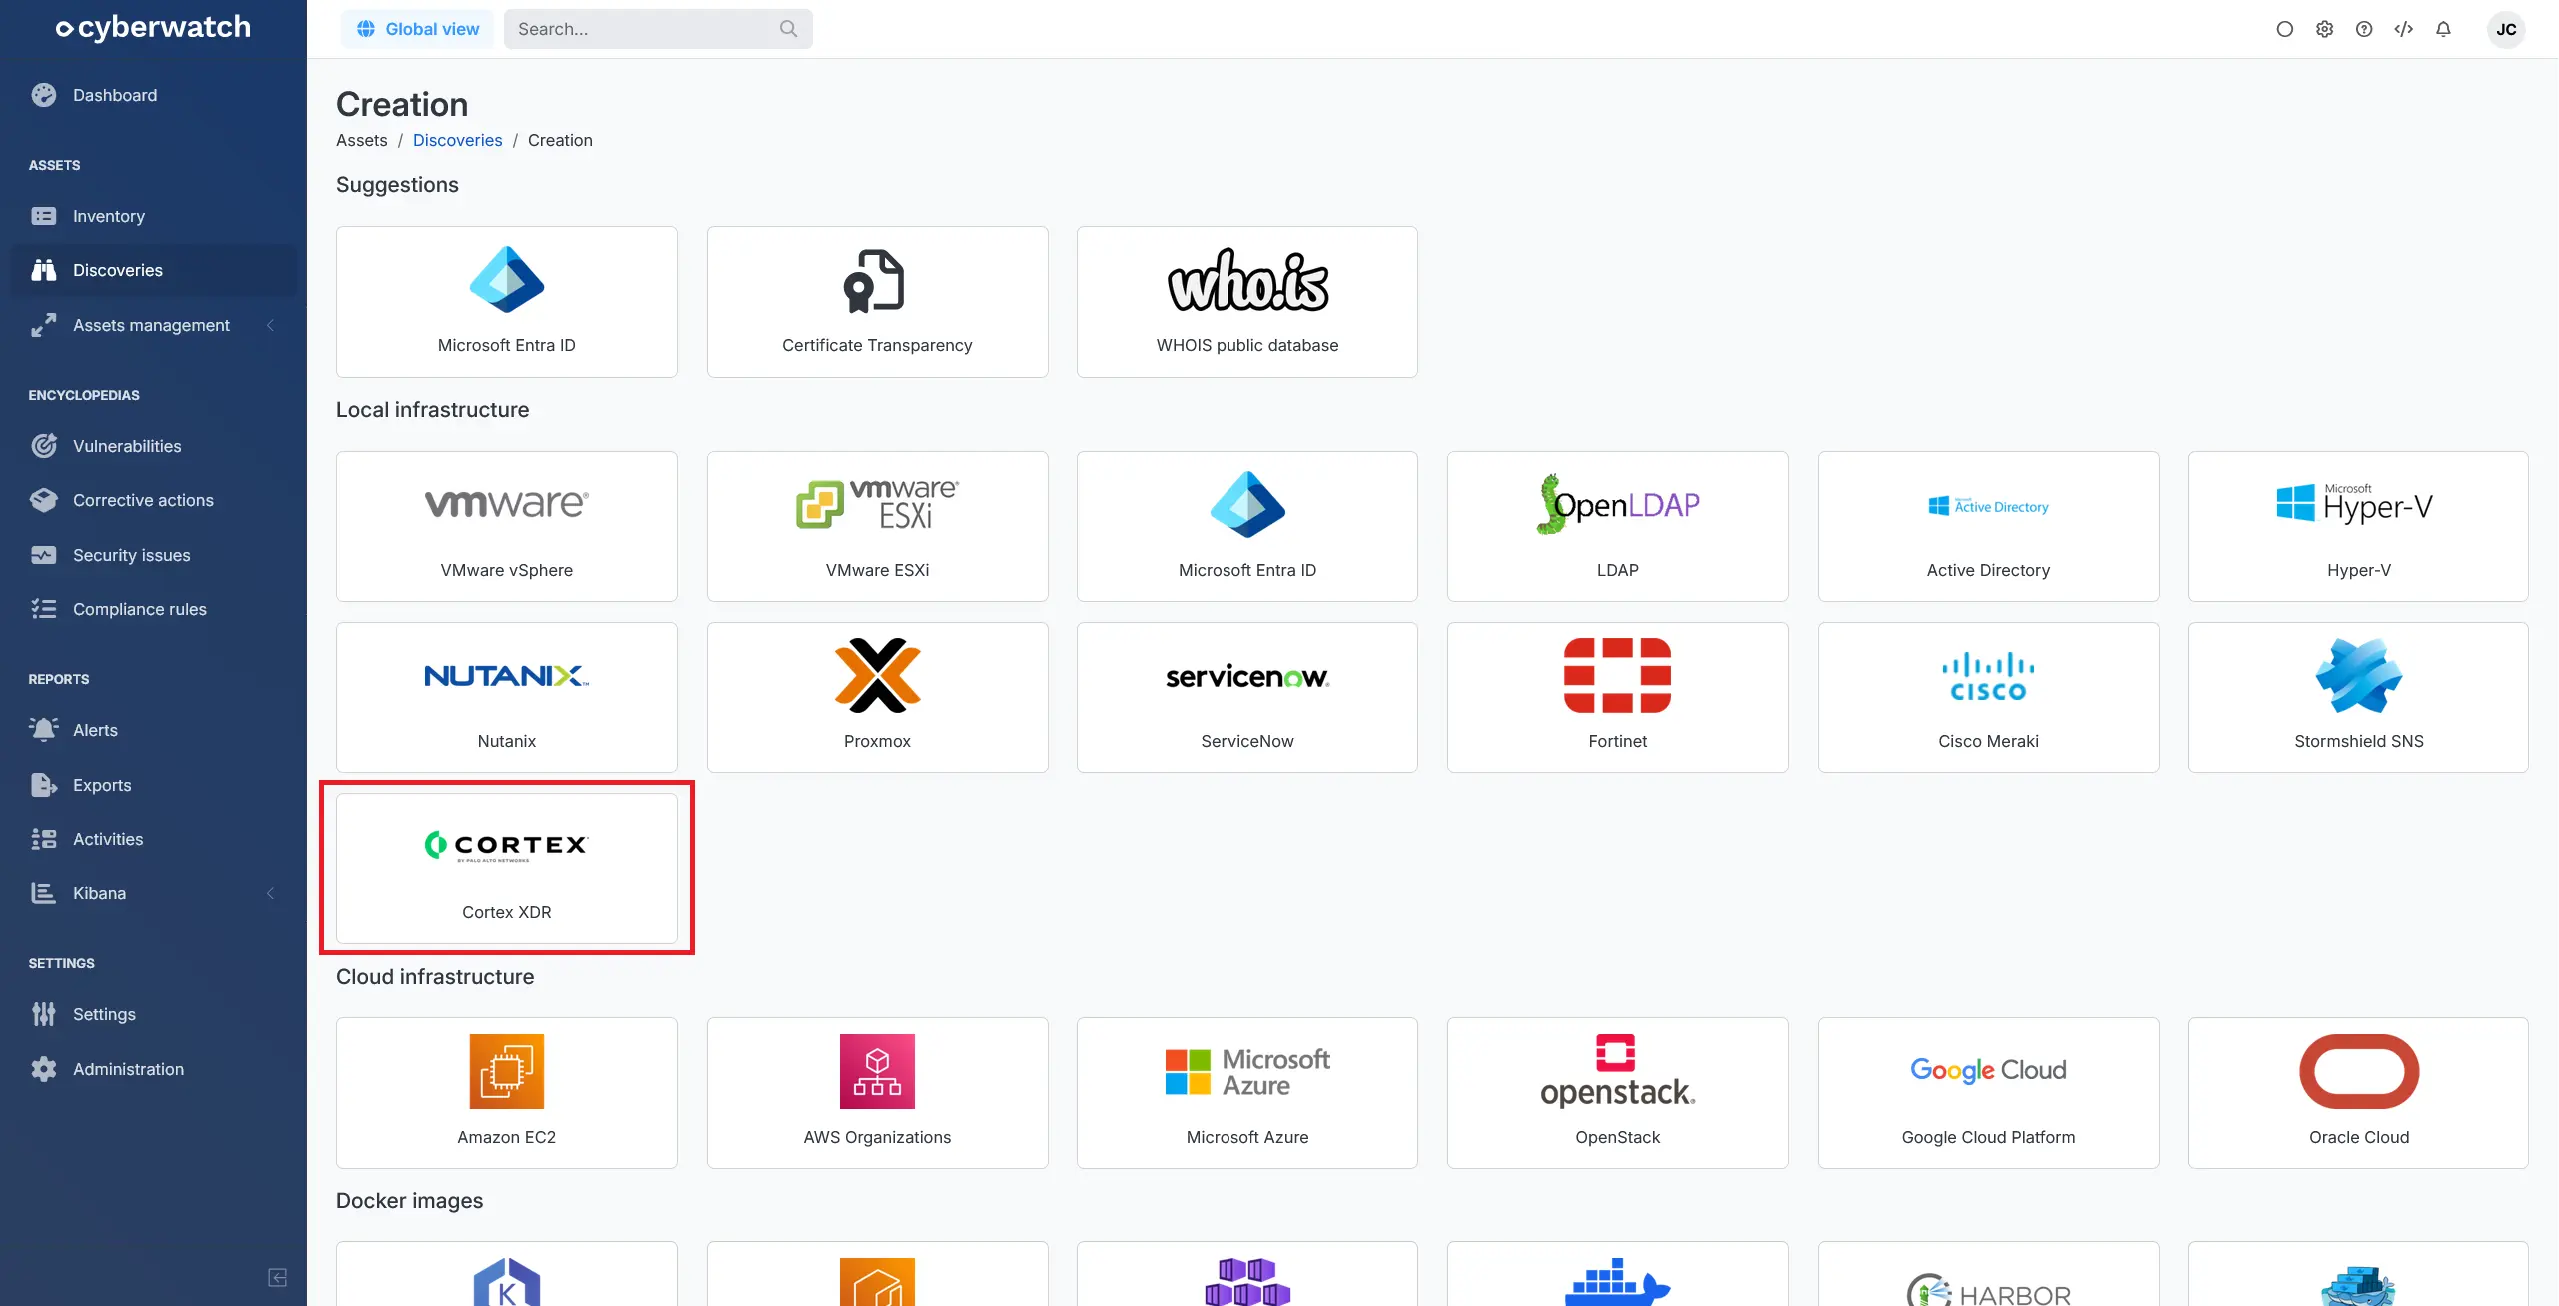
- Discoveries: added Palo Alto Cortex XDR discovery for monitoring assets with Cortex XDR agents (preview)
New features:
- Asset rules: added an action to set an initial project for assets without a project
- API: added new routes to create, update, and retrieve discoveries
- Cloud: Oracle Cloud Infrastructure resources are now visible in the “Resources” tab
- Compliance:
- Added support for operating system families in custom compliance rules
- Added support for Windows CIS Benchmark rules using local variables from OVAL definitions
- Added SUSE Linux Enterprise Server 16 CIS Benchmark and updated several CIS Benchmarks, including Debian, macOS, Ubuntu, and Windows
- Dashboard: added a widget to track asset count over time
- Scanning engine: added in-depth analysis of Java archives to report embedded dependencies
- Scope:
- Added support for Cisco APIC and Cisco Unified Communications (CUCM, CUC) devices
- Added support for Citrix NetScaler Console and SDX devices
- Added support for F5 rSeries devices
- Added support for Meinberg LANTIME devices
- Added support for Nutanix Prism Element devices
Updated features and performance improvements:
- Details of an Asset: from the patch management tab, you can now change the vulnerability analysis status for the selected patches
- Discoveries:
- Fortinet discovery now also reports devices from all VDOMs configured on FortiGate
- Support for AWS GovCloud environments in EC2 discoveries
- MITRE ATT&CK: Cyberwatch now relies on attack techniques from version 19
- Projects: Cyberwatch now automatically restores the last global project filter used at each login
- Reports: optimized report processing and generation
- Scanning engine:
- Improved detection of already fixed vulnerabilities on Windows assets
- Improved detection of Go dependencies embedded in binaries
- Improved detection of Red Hat packages
- Improved vulnerability detection on SUSE and openSUSE systems
Bugfixes:
- Agentless connections:
- Fixed an issue with firmware detection for Cisco NX-OS devices over SNMP
- Fixed an issue with ForcePoint device detection over SNMP
- Details of an Asset: fixed an issue where comments were not saved in the modal used to change vulnerability analysis status
- Discoveries: fixed an issue that could interrupt GitLab Container Registry discoveries on SaaS instances
- Scanning engine:
- Fixed an inconsistency in the suggested patch version for Microsoft Office 2021
- Fixed an issue where the fixed version was reported incorrectly when analyzing applications on Linux assets
15.7 (2026-05-11)
Highlighted features:
- AI: improved performance and relevance of MCP queries on assets and vulnerabilities
- Compliance: added Oracle Cloud Infrastructure CIS Benchmark
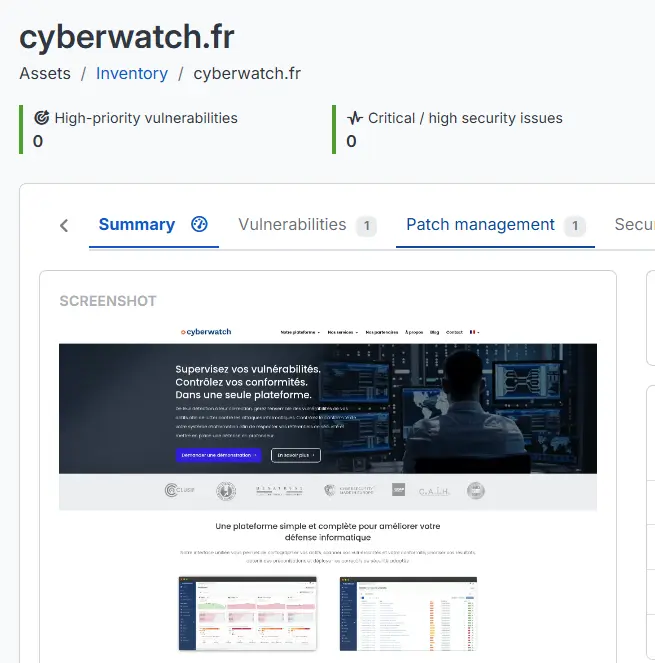
- Network targets and websites: added screenshots to scan results to make analysis easier (preview)
New features:
- Dashboard: added a chart to show the distribution of vulnerabilities by status
- Compliance: added the ability to create declarative custom rules, extending compliance coverage to network devices and air-gapped assets
- Discoveries: added discovery for Cisco Meraki devices
- Docker images: globally installed NPM packages are now also detected
- Network targets and websites: added the ability to configure Nmap modules through scan policies
- Scope:
- Added end-of-life dates for Drupal and Ivanti Connect Secure
- Added security advisories from the Norwegian NSM and the UK NCSC
- Added support for Azure Data Studio, Centreon, Microsoft Defender Antivirus, Microsoft SQL Server 2025 and Ubuntu 26.04
Updated features and performance improvements:
- API:
- The
/api/v3/serversroute now also supports filtering by operating system family - Compliance rule and vulnerability routes now include comments
- The
- Discoveries:
- Docker images detected through the discovery of running images on Linux assets now also show their source assets
- Improved error handling for AWS discoveries
- Exports: comments are now included in CSV exports for compliance rules and vulnerabilities
- External tools: enhanced data sent through syslog with additional information related to vulnerability prioritization and exposure
- Scanning engine:
- Enhanced Python library detection by taking installation metadata into account
- Improved detection for Cisco NX-OS devices, Microsoft System Center Configuration Manager, and Red Hat (AUS, E4S support and more accurate technology identification)
- Updated vulnerability detection on Linux systems to reflect a change in package architecture handling
- Searches: more accurate results through improved filtering that takes search anchors into account (beginning and end of text)
Bugfixes:
- Agentless connections:
- Fixed an issue with firmware detection for OpenGear LightHouse devices over SNMP
- You can once again bulk edit saved credentials
- Alerts:
- Fixed an issue when editing alerts without filters
- Fixed an issue where the “Status” filter was not applied to security issues
- Compliance: fixed an issue with the time unit that could affect the evaluation of some Windows CIS rules
- Discoveries: fixed an issue where search filters in the side panel caused incomplete display of discovered assets
- Scanning engine:
- Fixed detection issues on Amazon Linux 2, Check Point, Oracle Linux and HPE Aruba devices
- Fixed a name-casing issue in malicious package detection
- Fixed an issue where already patched vulnerabilities were detected on Windows assets
15.6 (2026-03-30)
Highlighted features:
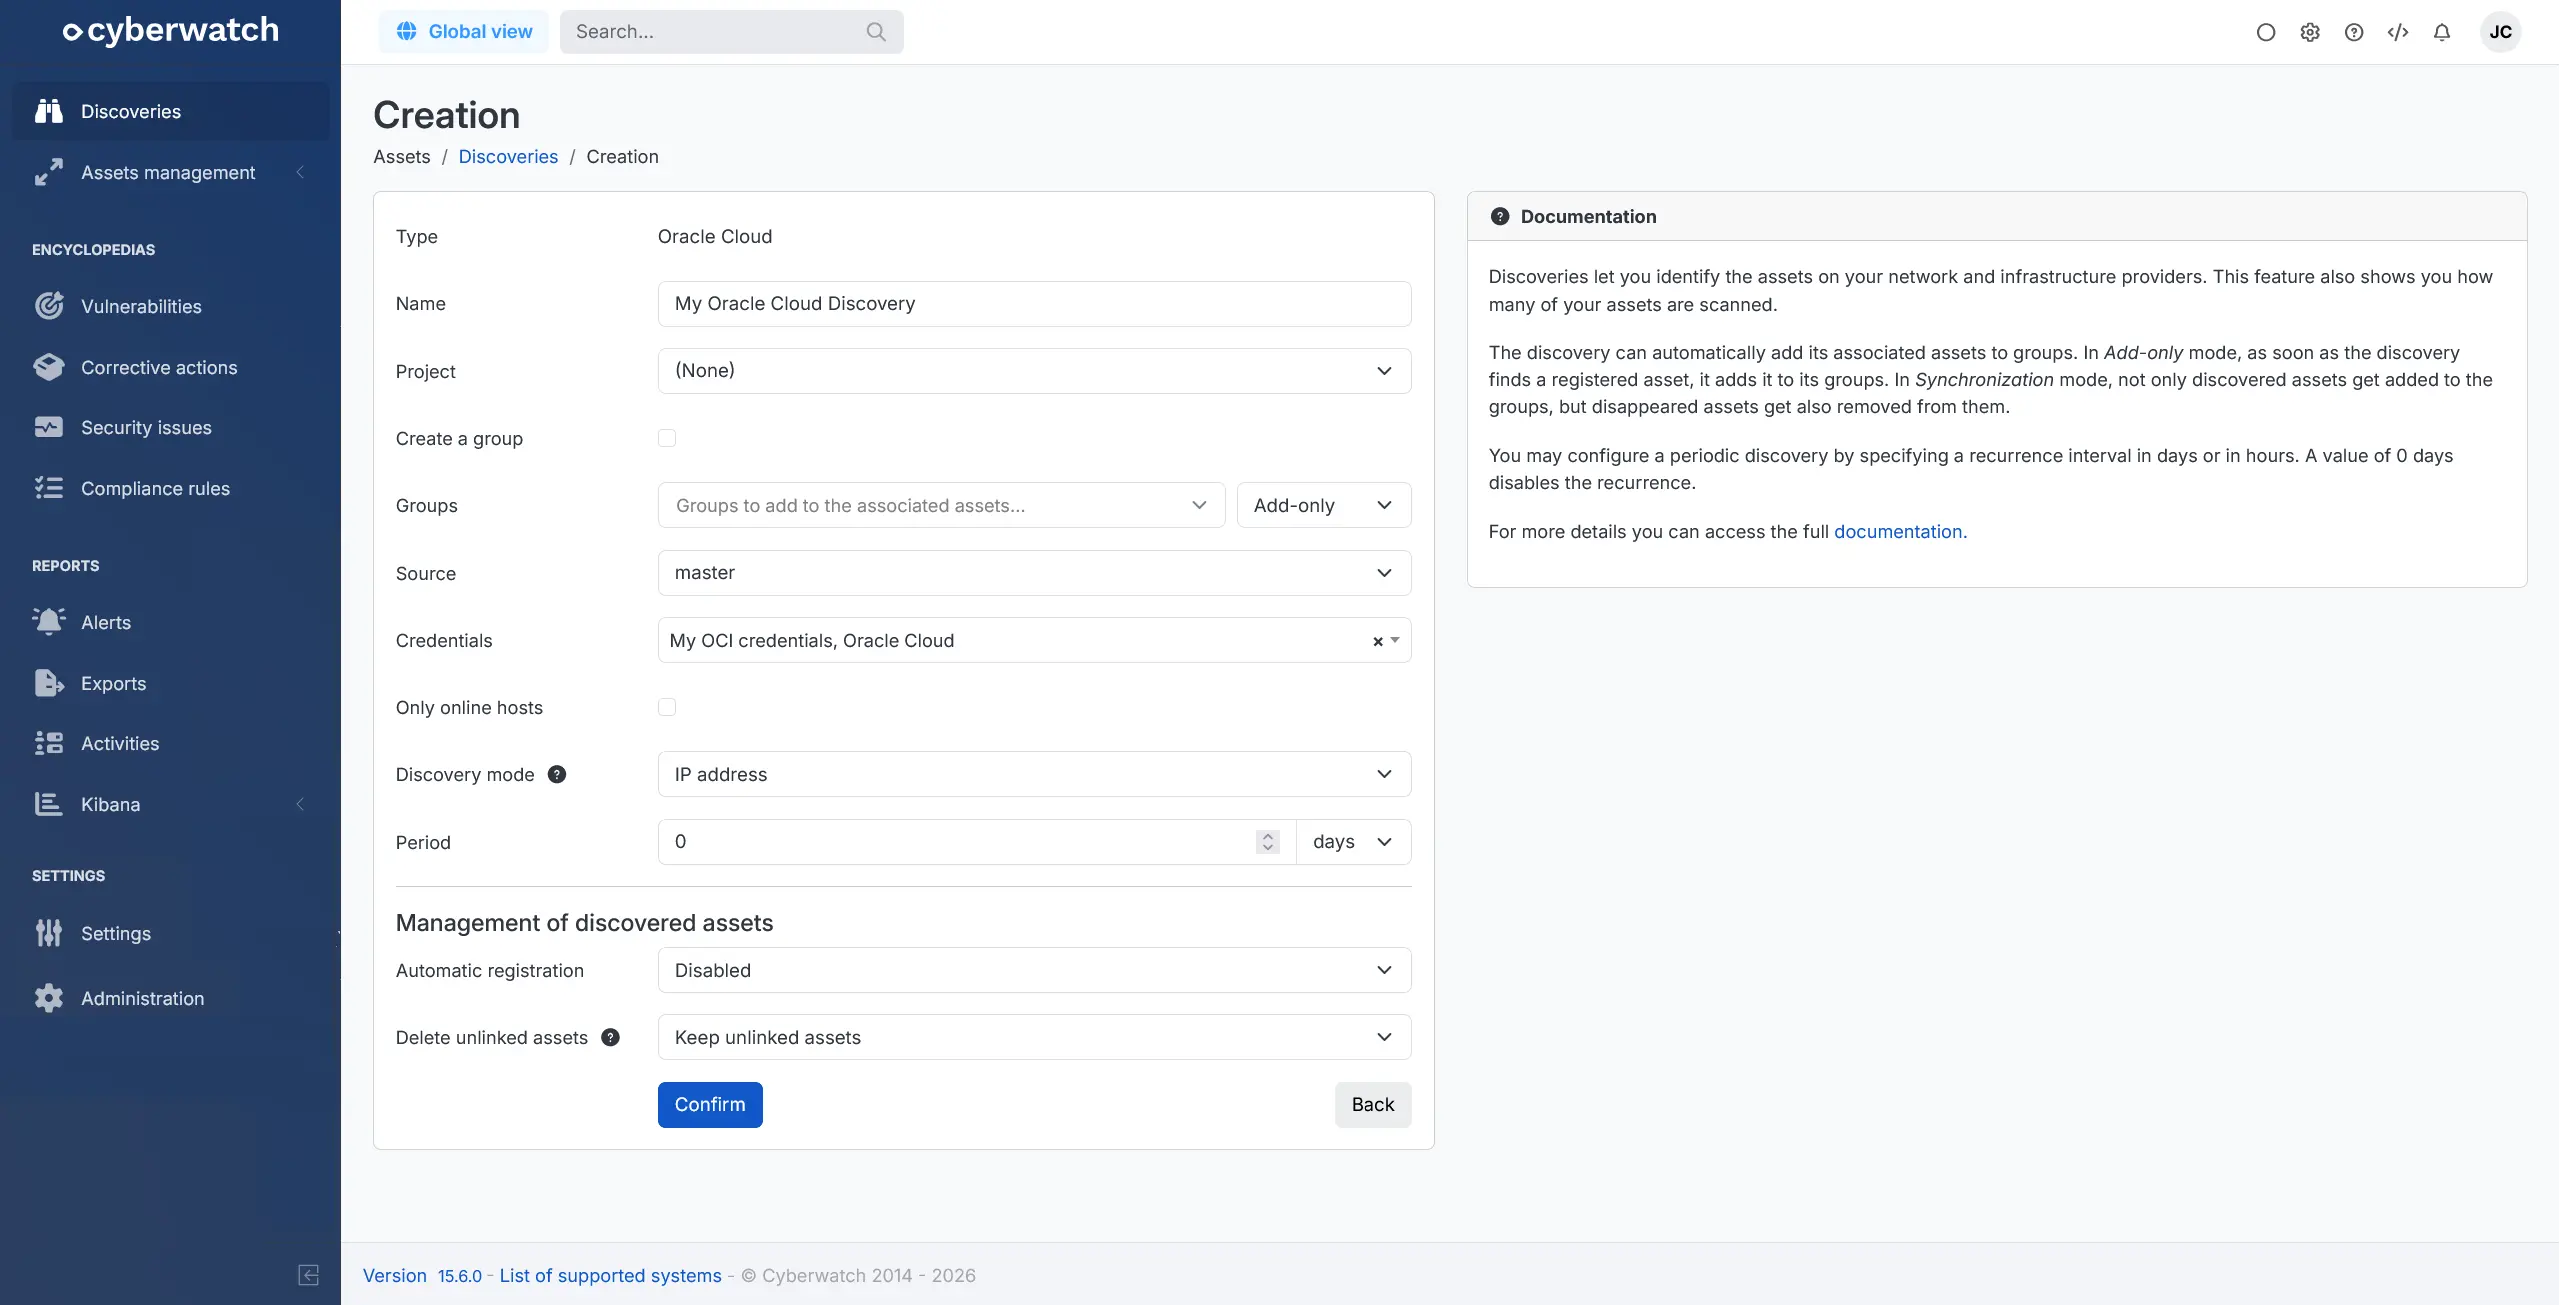
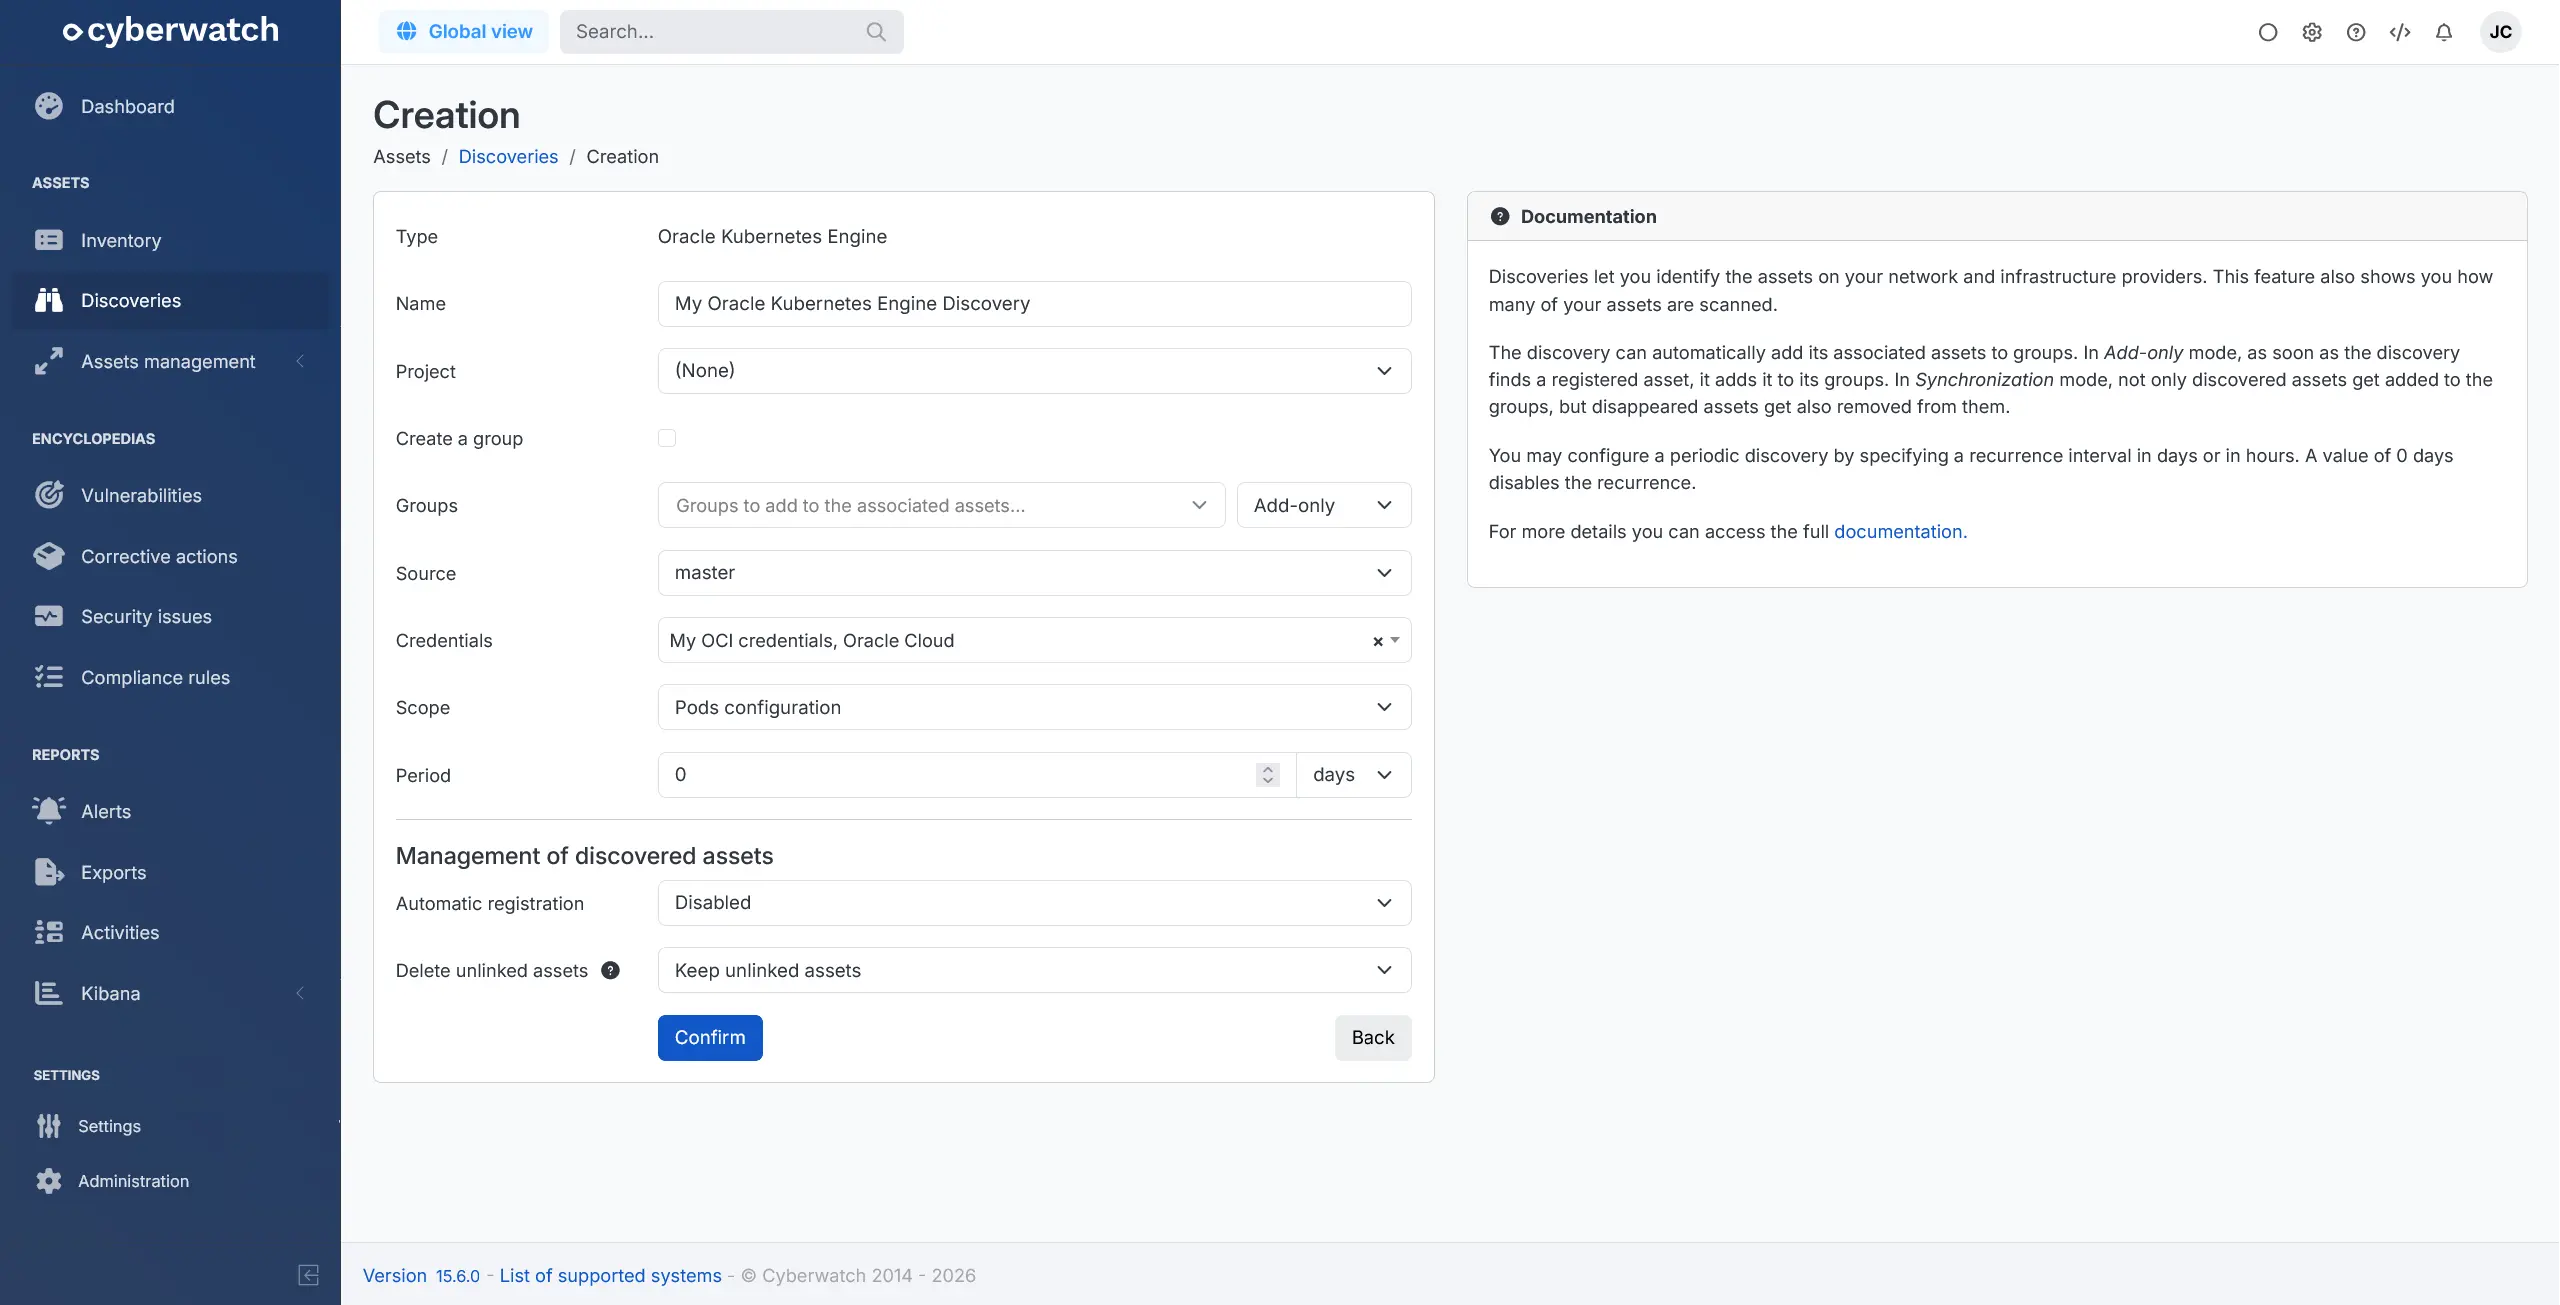
- Discoveries: added Oracle Cloud Infrastructure and Oracle Kubernetes Engine discoveries (preview) (preview)
- Kibana: user scope is now enforced: each user can only access assets from their own projects. Kibana access can be enabled in bulk from the interface. This feature requires orchestrator base version 5.30 or later
- Languages: the application is now available in Spanish
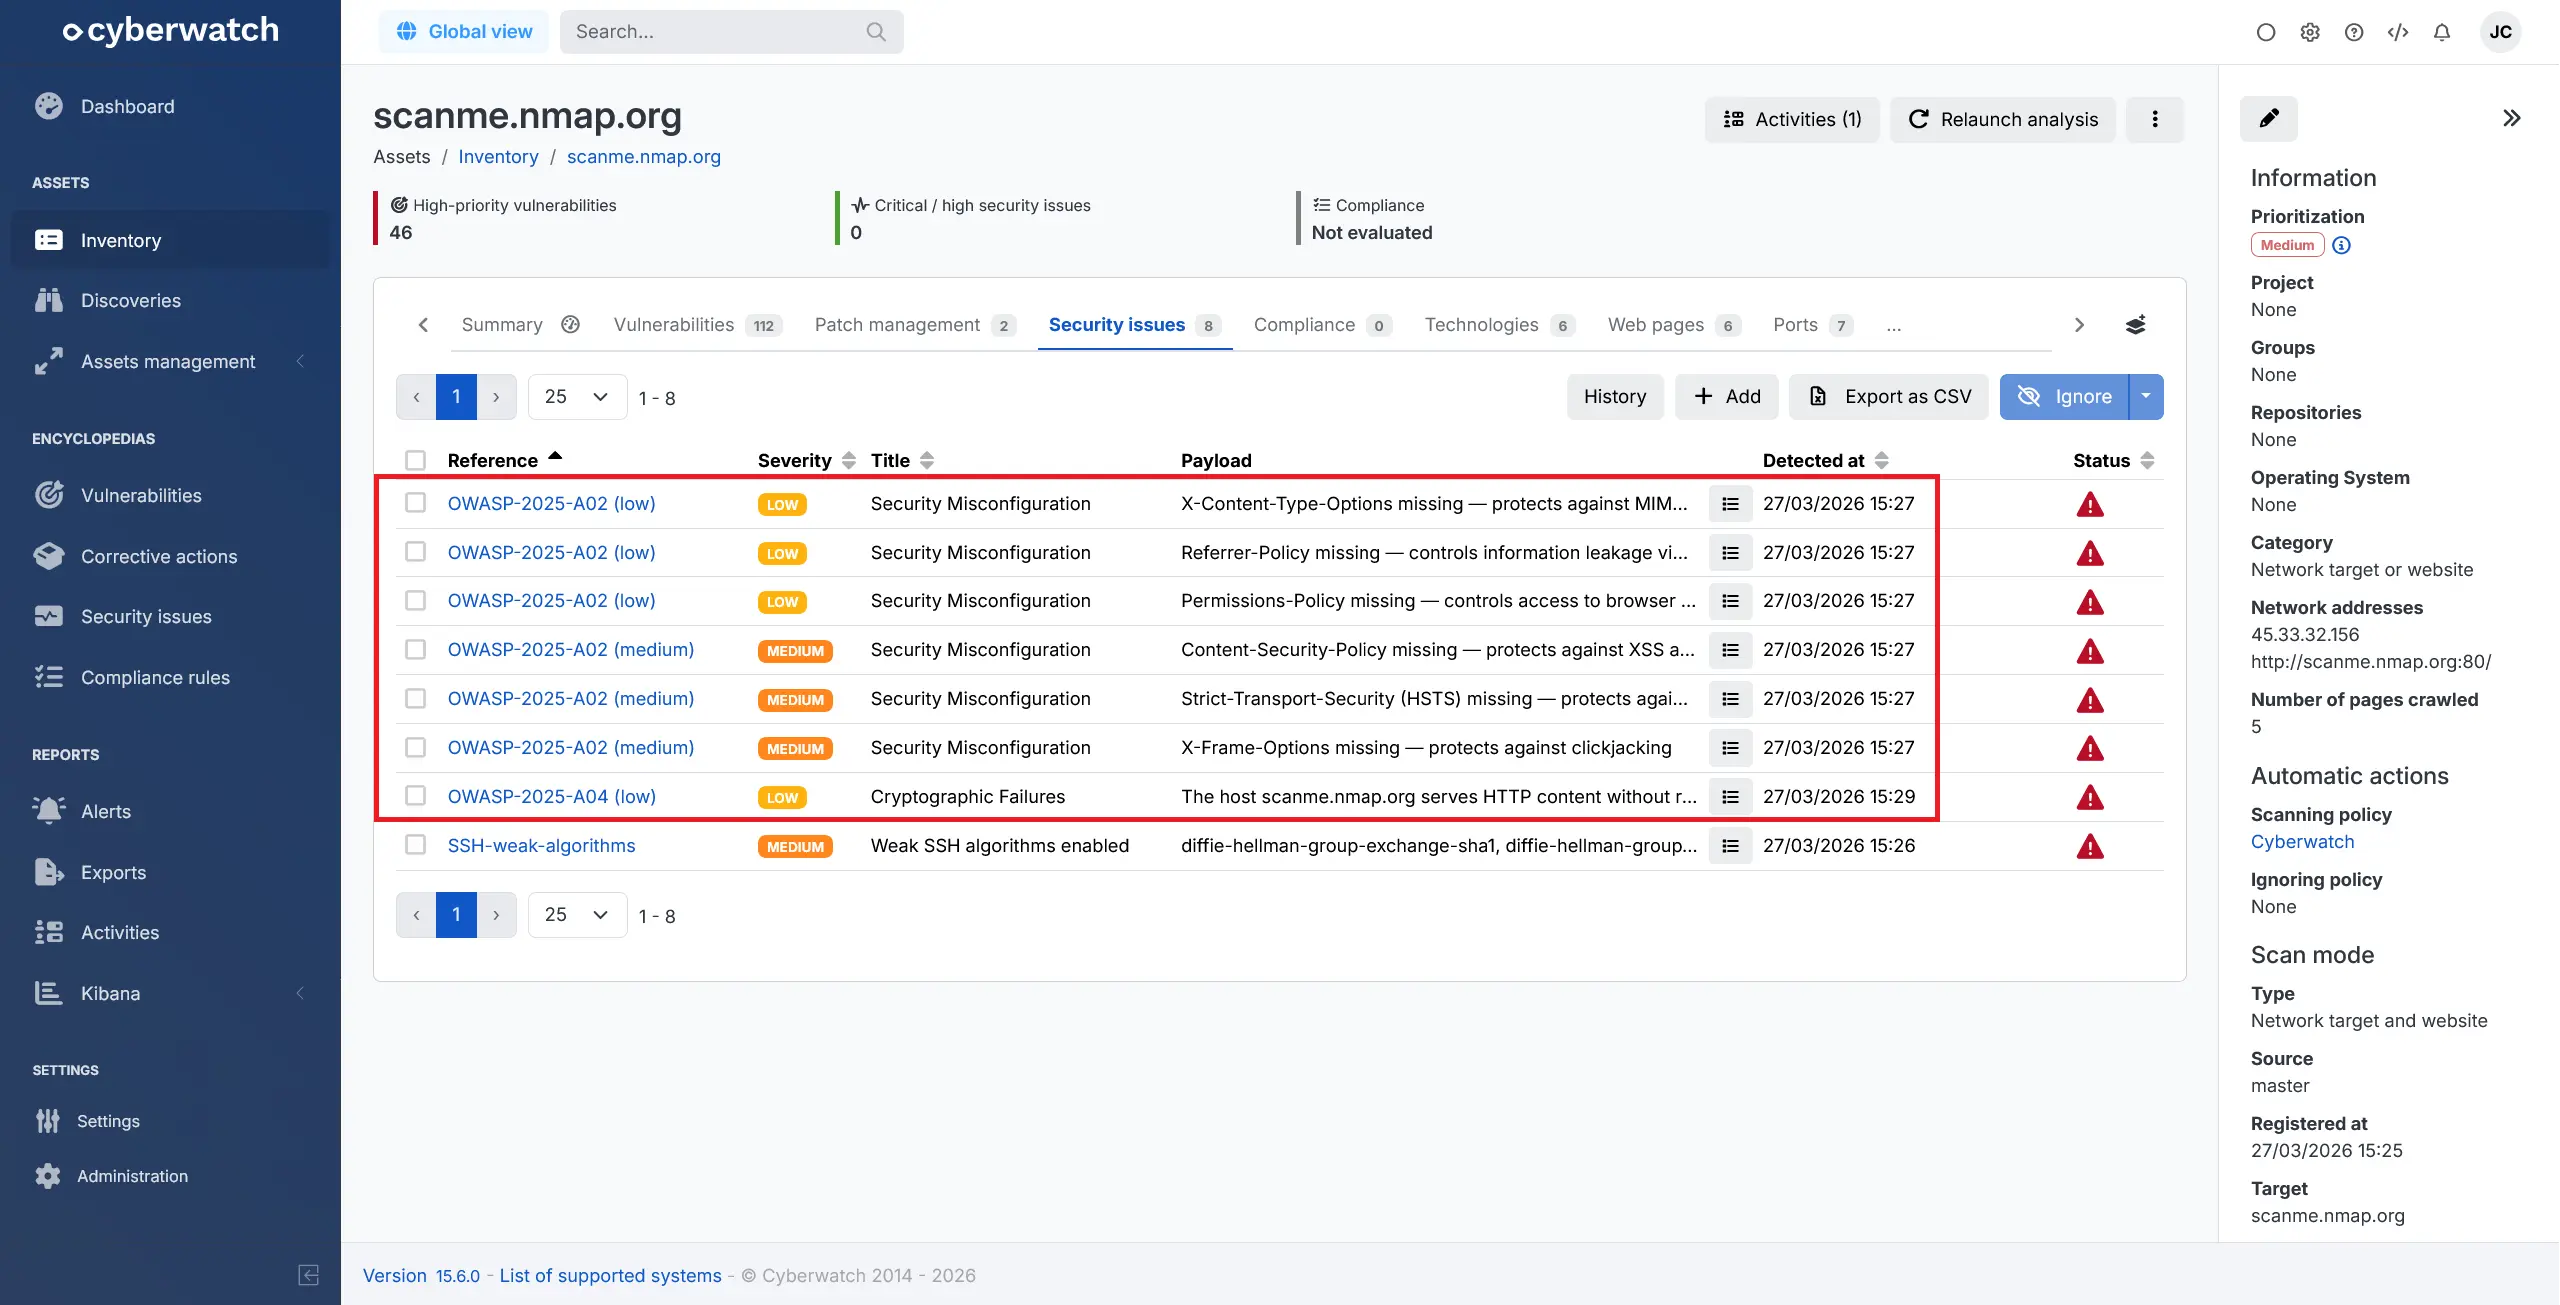
- Network targets and websites: redesigned the OWASP web application scanning engine. This engine improves overall performance and replaces the WSTG framework with the OWASP Top 10 2025 (preview)
- Reports: added the ability to generate a PDF information system coverage report for audits and regulatory compliance
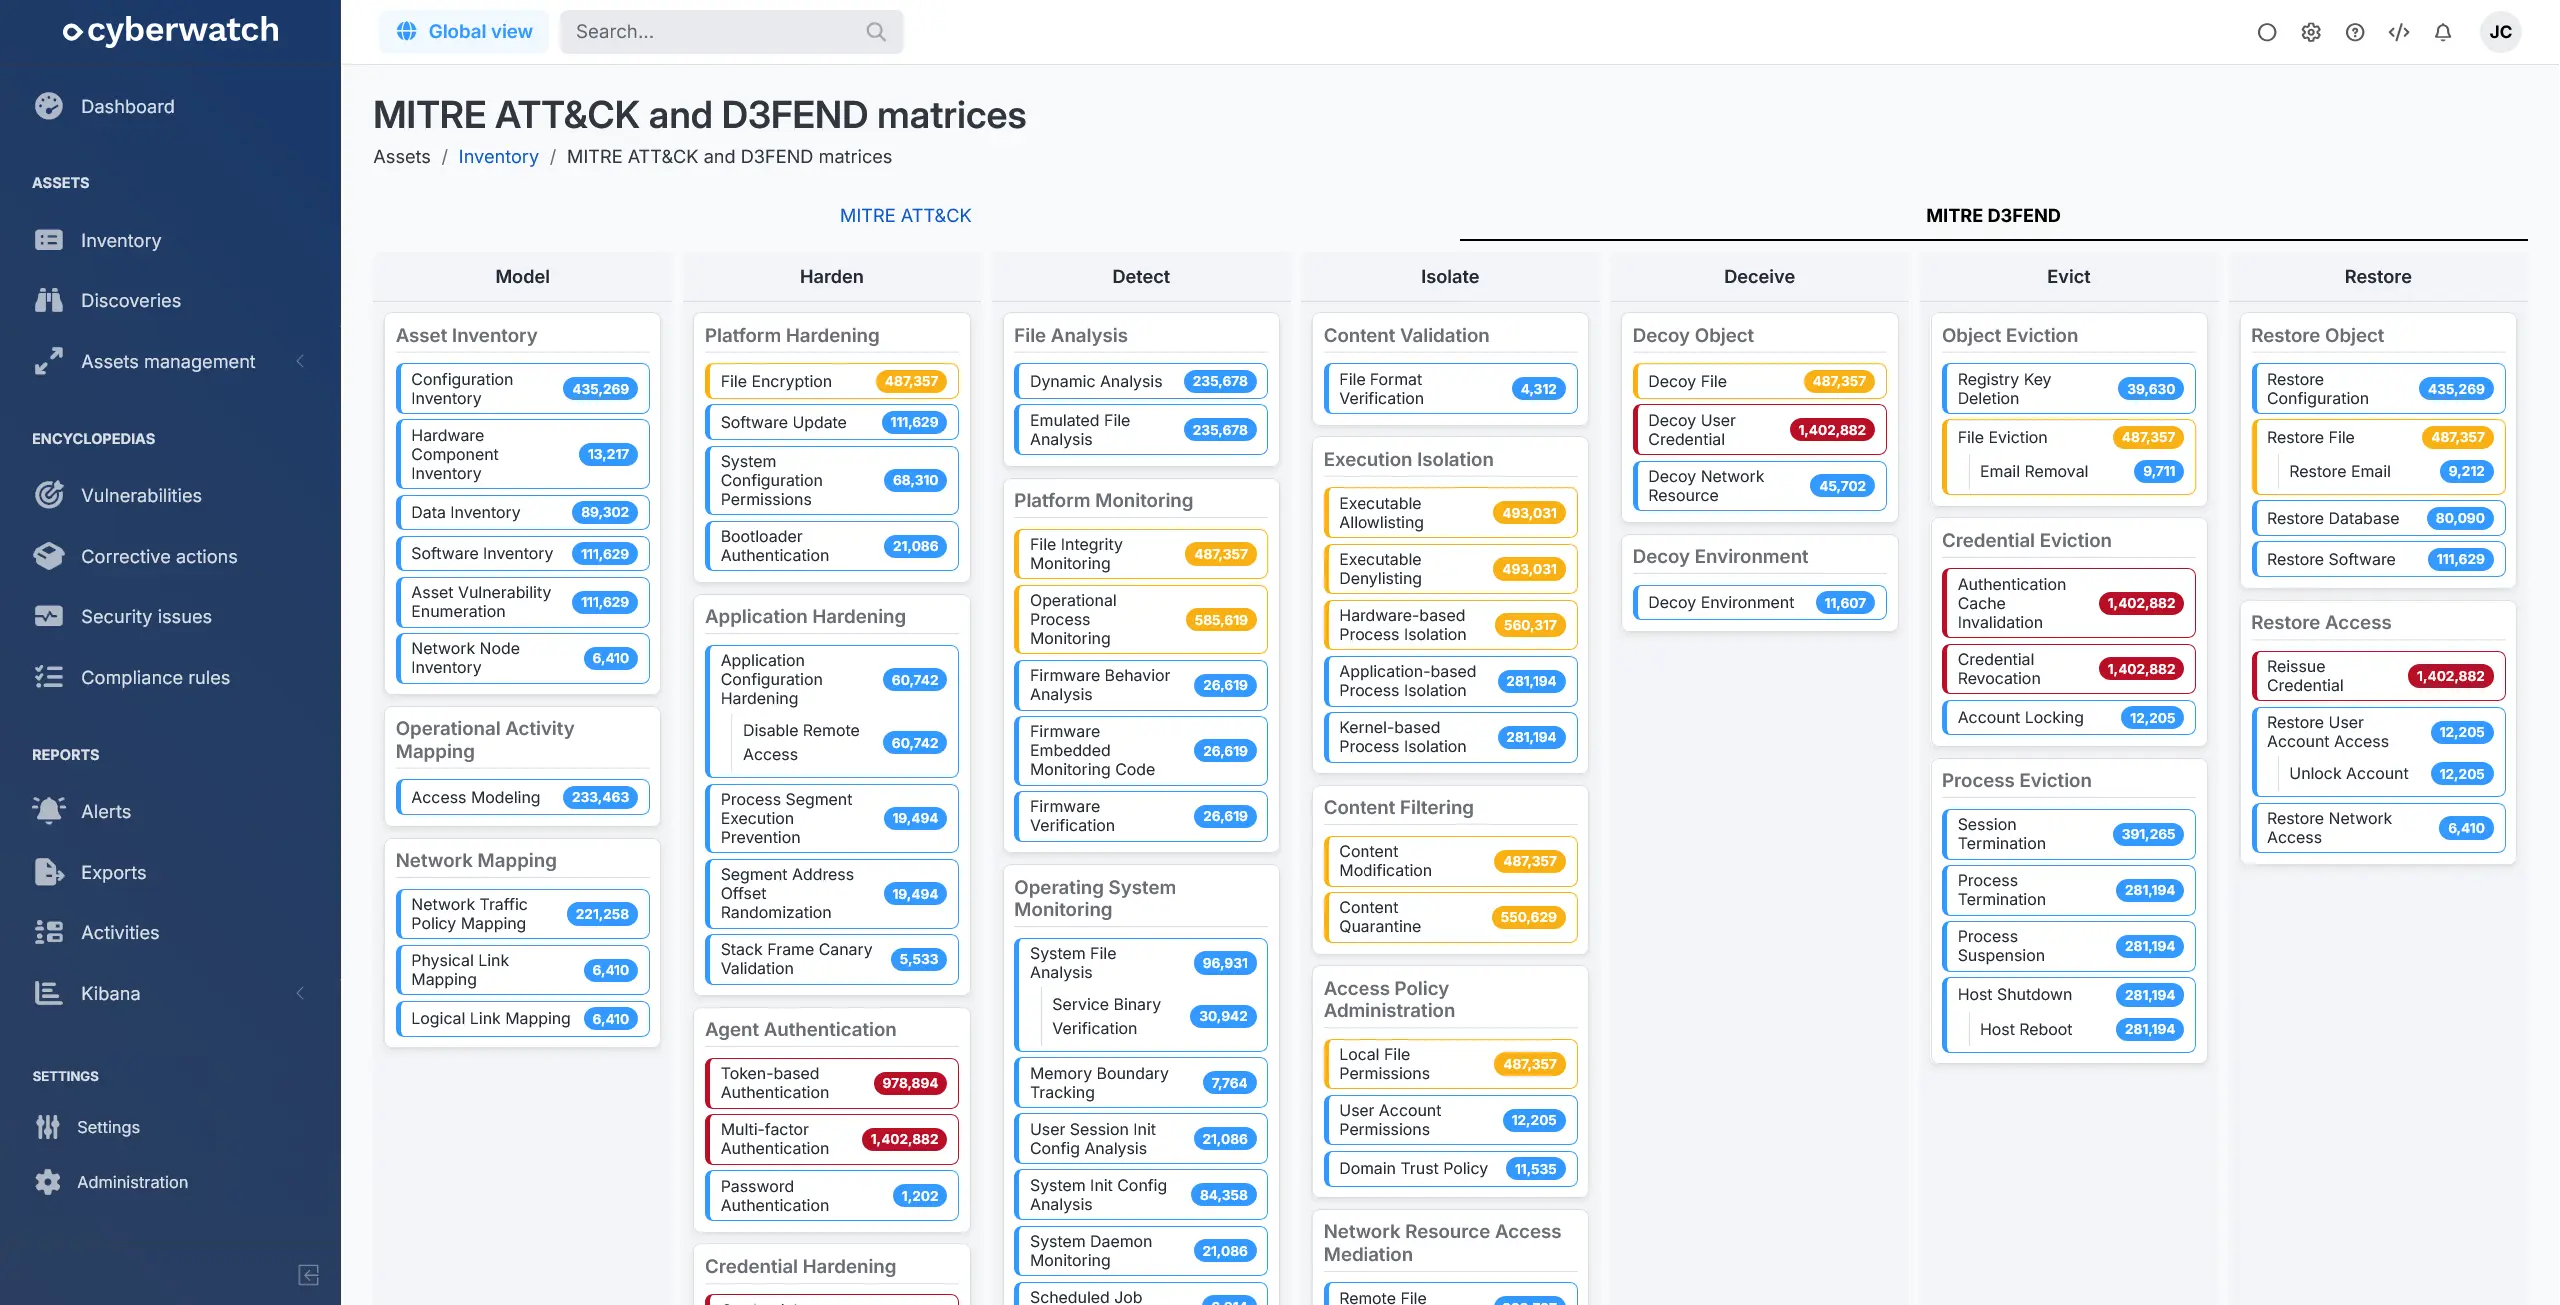
- Vulnerability encyclopedia: added the MITRE D3FEND framework to complement ATT&CK, with matrices displayed in a tabbed view, to enhance analysis using associated defense techniques (preview)
New features:
- Scanning engine:
- Installed Windows drivers are reported in the list of technologies
- Python packages from virtual environments are also reported
- Scope:
- Added security advisories from the NCSC Ireland
- Added support for Arista devices
- Added support for VMware Cloud Director
- Added support for ZPE Systems Nodegrid Serial Console devices
Updated features and performance improvements:
- Agents: included the project in the names of MSI files
- AI: improved MCP server performance and analysis capabilities
- Authentication provider: you can now enable verification of IdP certificate expiration in SAML
- Cloud: the wizard also facilitates the creation of Microsoft Entra ID applications for Azure and Microsoft 365, simplifying integration with Cyberwatch
- Corrective actions: improved the Windows Package Manager support for updating third-party applications
- Customization: new settings to refine the CVEs included in alerts
- Details of a Vulnerability: the CSV export can be limited to selected assets
- Details of an Asset: improved management of vulnerability statuses during corrective actions
- Projects: analysis scripts can also be defined at the project level
- Repositories: performance improvements to optimize page load time
Bugfixes:
- Agentless connections: fixed a detection issue on Aruba devices in SNMP
- Alerts: fixed an issue that prevented alerts from being edited
- Docker images: fixed an issue that prevented some images from being scanned when added from the details page of an asset
- Prioritization policies: fixed an issue that prevented system administrators with limited project access from creating policies
- Projects: users associated with a single project can once again select their stored credentials
- Scanning engine:
- Fixed a detection issue on Veeam Backup & Replication
- Fixed an analysis problem on Microsoft Office
- Fixed an analysis problem on Mozilla Firefox
- Security issues: fixed inconsistent behavior when their status changes
15.5 (2026-02-23)
Highlighted features:
- AI: added a new MCP feature allowing artificial intelligence to interact with the application and automate specific actions
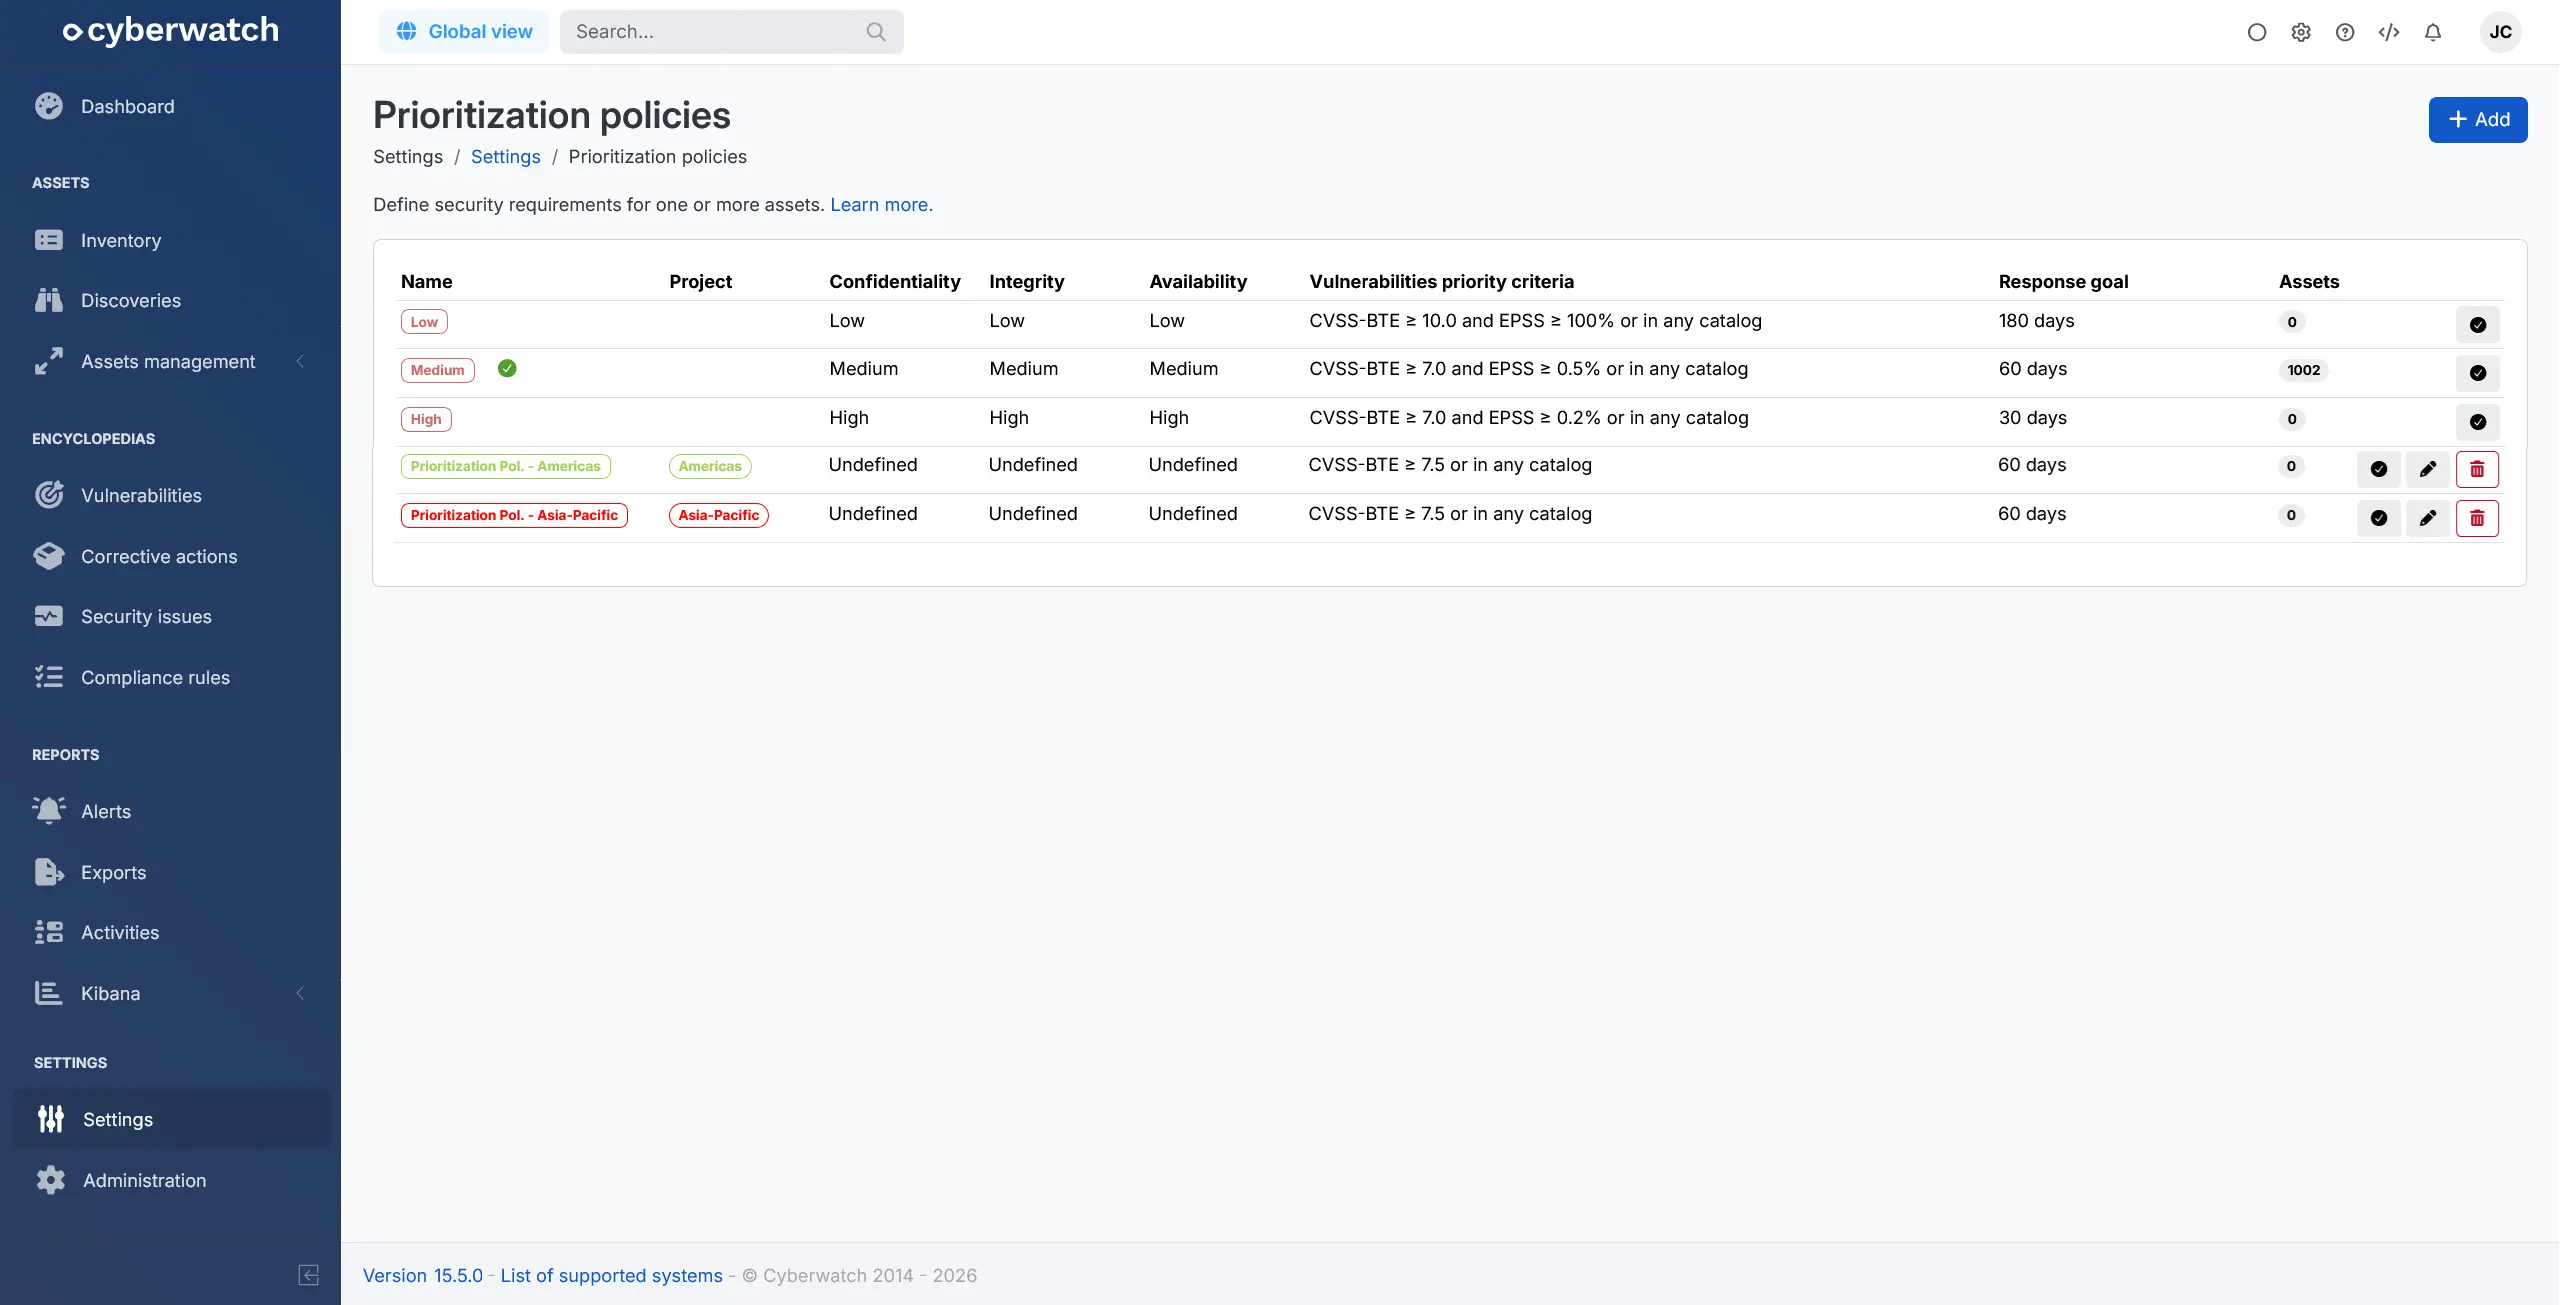
- Criticalities: renamed to “Prioritization policies” to better reflect its intended use (preview)
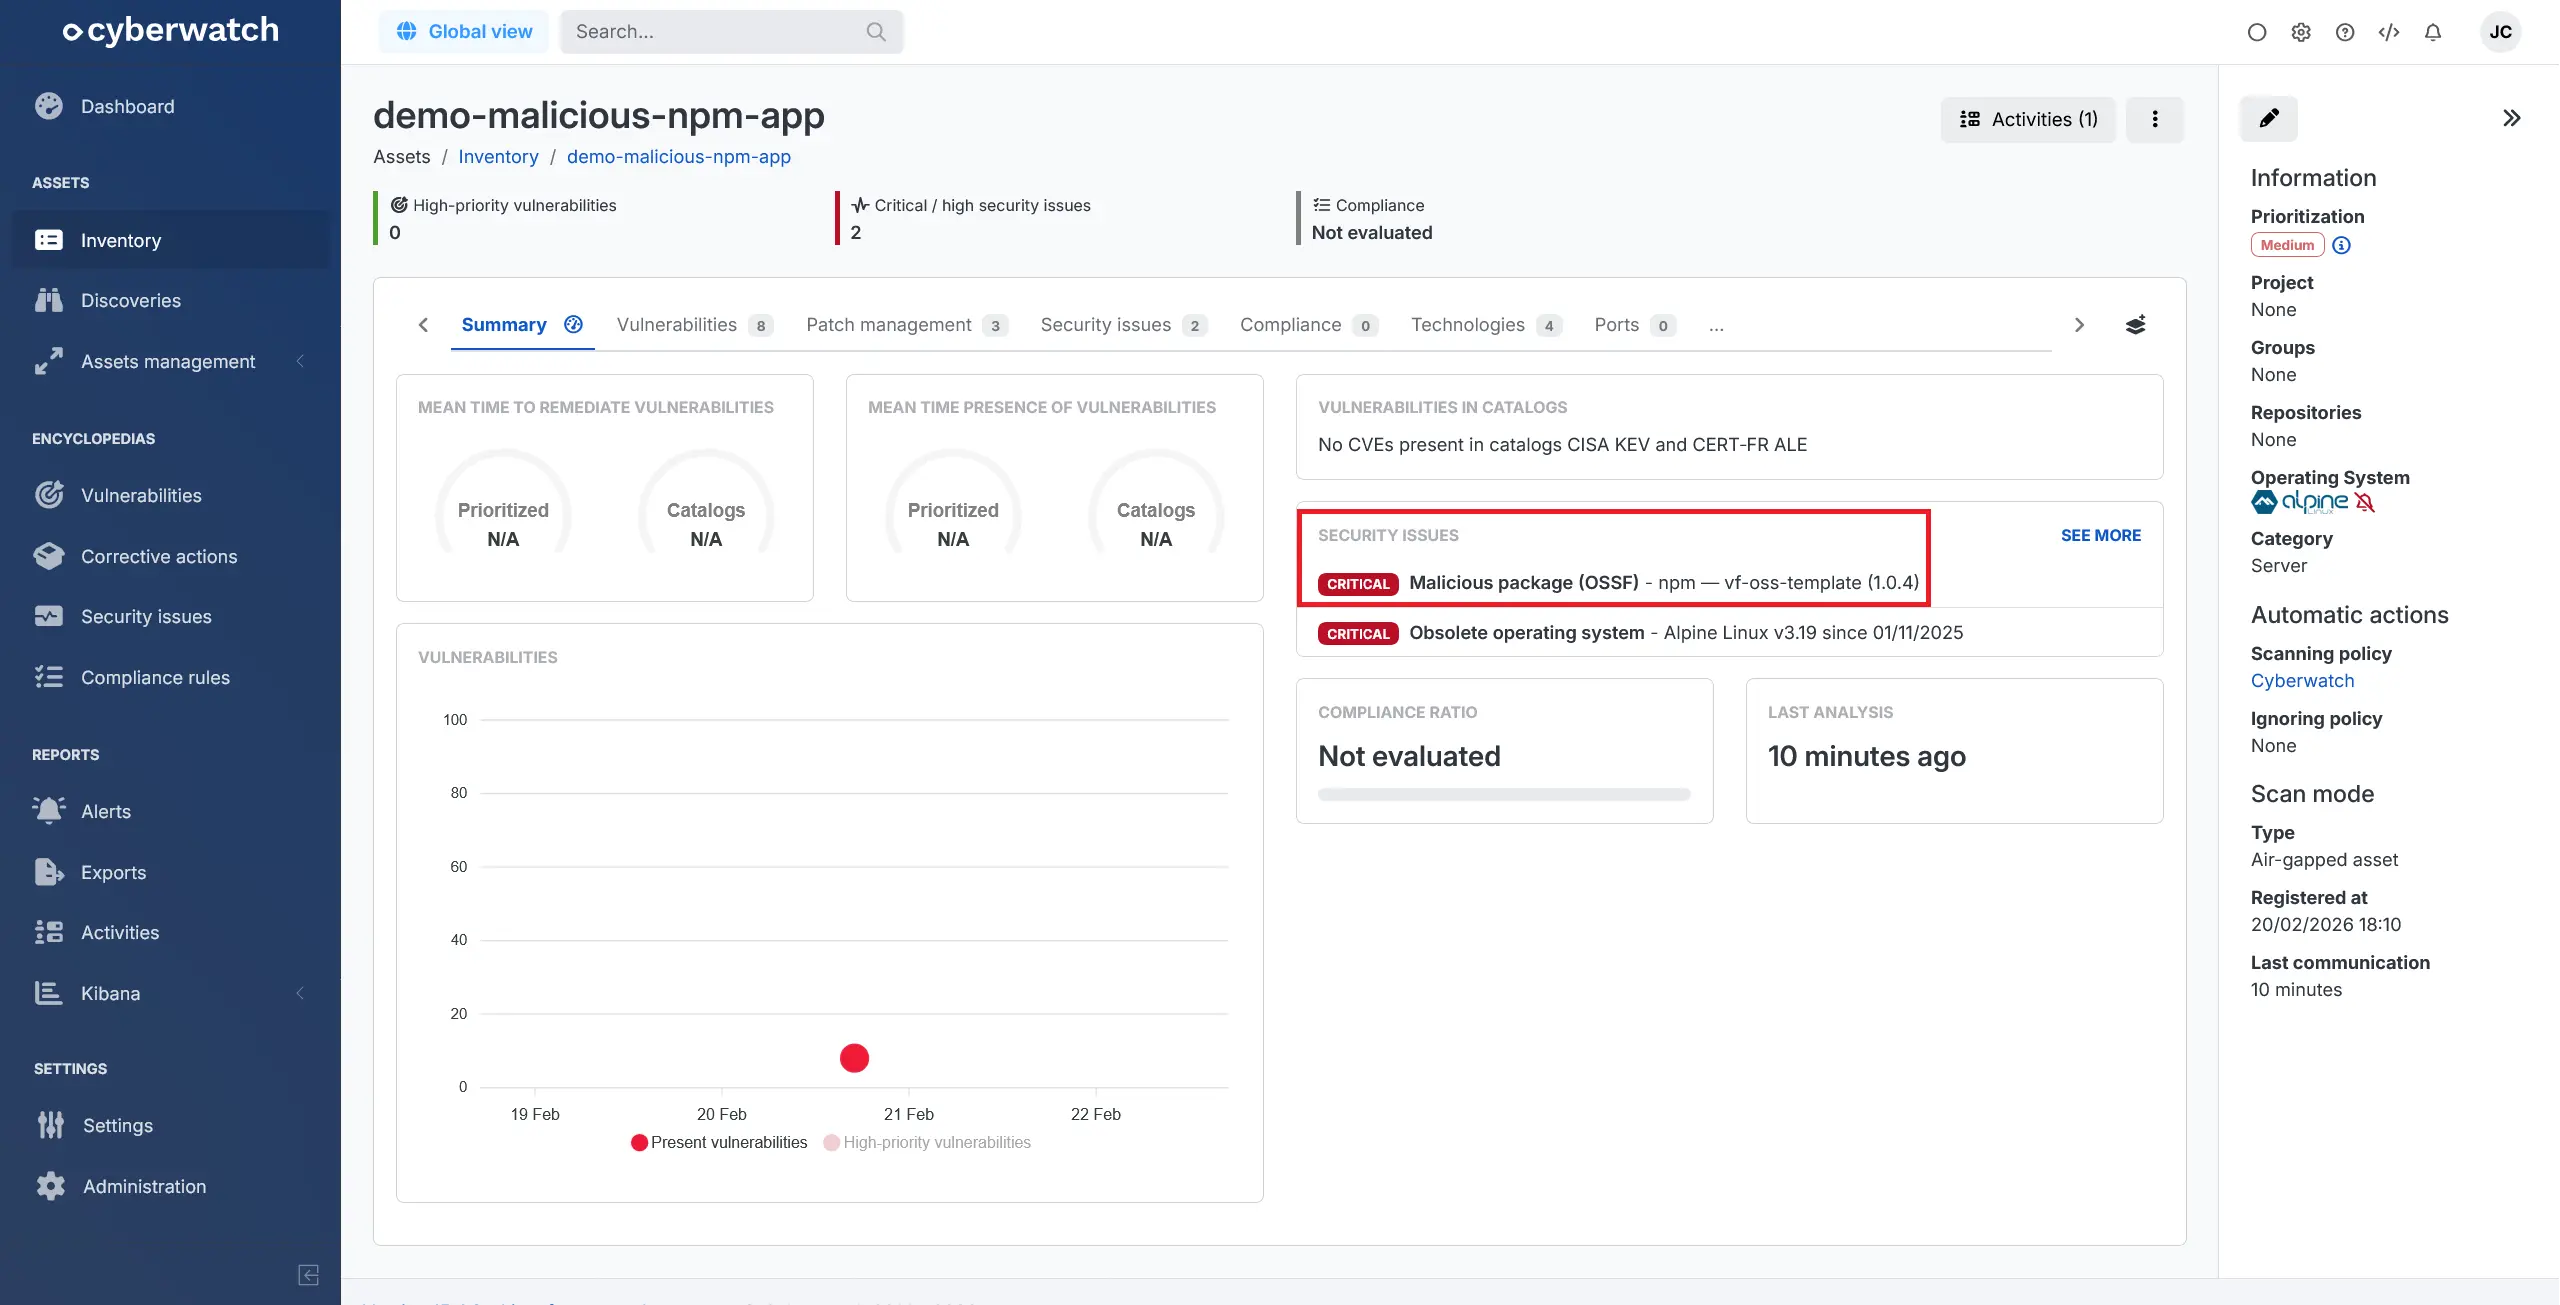
- Security issues: added detection of malicious software packages affecting assets, based on data from the OpenSSF repository (preview)
New features:
- Corrective actions: patch deployment for Snap applications is now supported
- Scope:
- Added security advisories from ABB
- Added security advisories from Nozomi Networks
- Added security advisories from SICK
- Added security advisories from the CNCS Portugal
- Added security advisories from the NCSC Netherlands
- Added security advisories from VARIoT
- Added support for SUSE Linux Enterprise Server 16.0
Updated features and performance improvements:
- API: updated documentation to clarify route access rights based on user roles
- Assets: declarative data for all assets can now be updated via air-gap import
- Authentication provider: enhanced project association through SAML user groups, including automatic linking of unknown projects based on name matching
- Benchmarks: the compliance benchmark configuration view has been moved to the “Administration” menu
- Cloud environment compliance: updated Microsoft 365 compliance rules for Exchange Online, Purview, OneDrive, SharePoint Online and Teams
- Compliance: improved implementation of some CIS Benchmark rules on Windows Server 2022 and 2025
- External tools: Syslog logs can now be sent over TCP with TLS encryption
- Network targets and websites:
- Improved consistency of scan results between normal and headless modes
- You can now select which Wapiti modules to run during scans
- Projects: prioritization policies can also be defined at the project level
- Vulnerabilities: functional and UI adjustments in preparation for the upcoming vulnerability tracking feature
Bugfixes:
- Network targets and websites: fixed error handling when a target is unavailable
15.4 (2026-01-26)
Highlighted features:
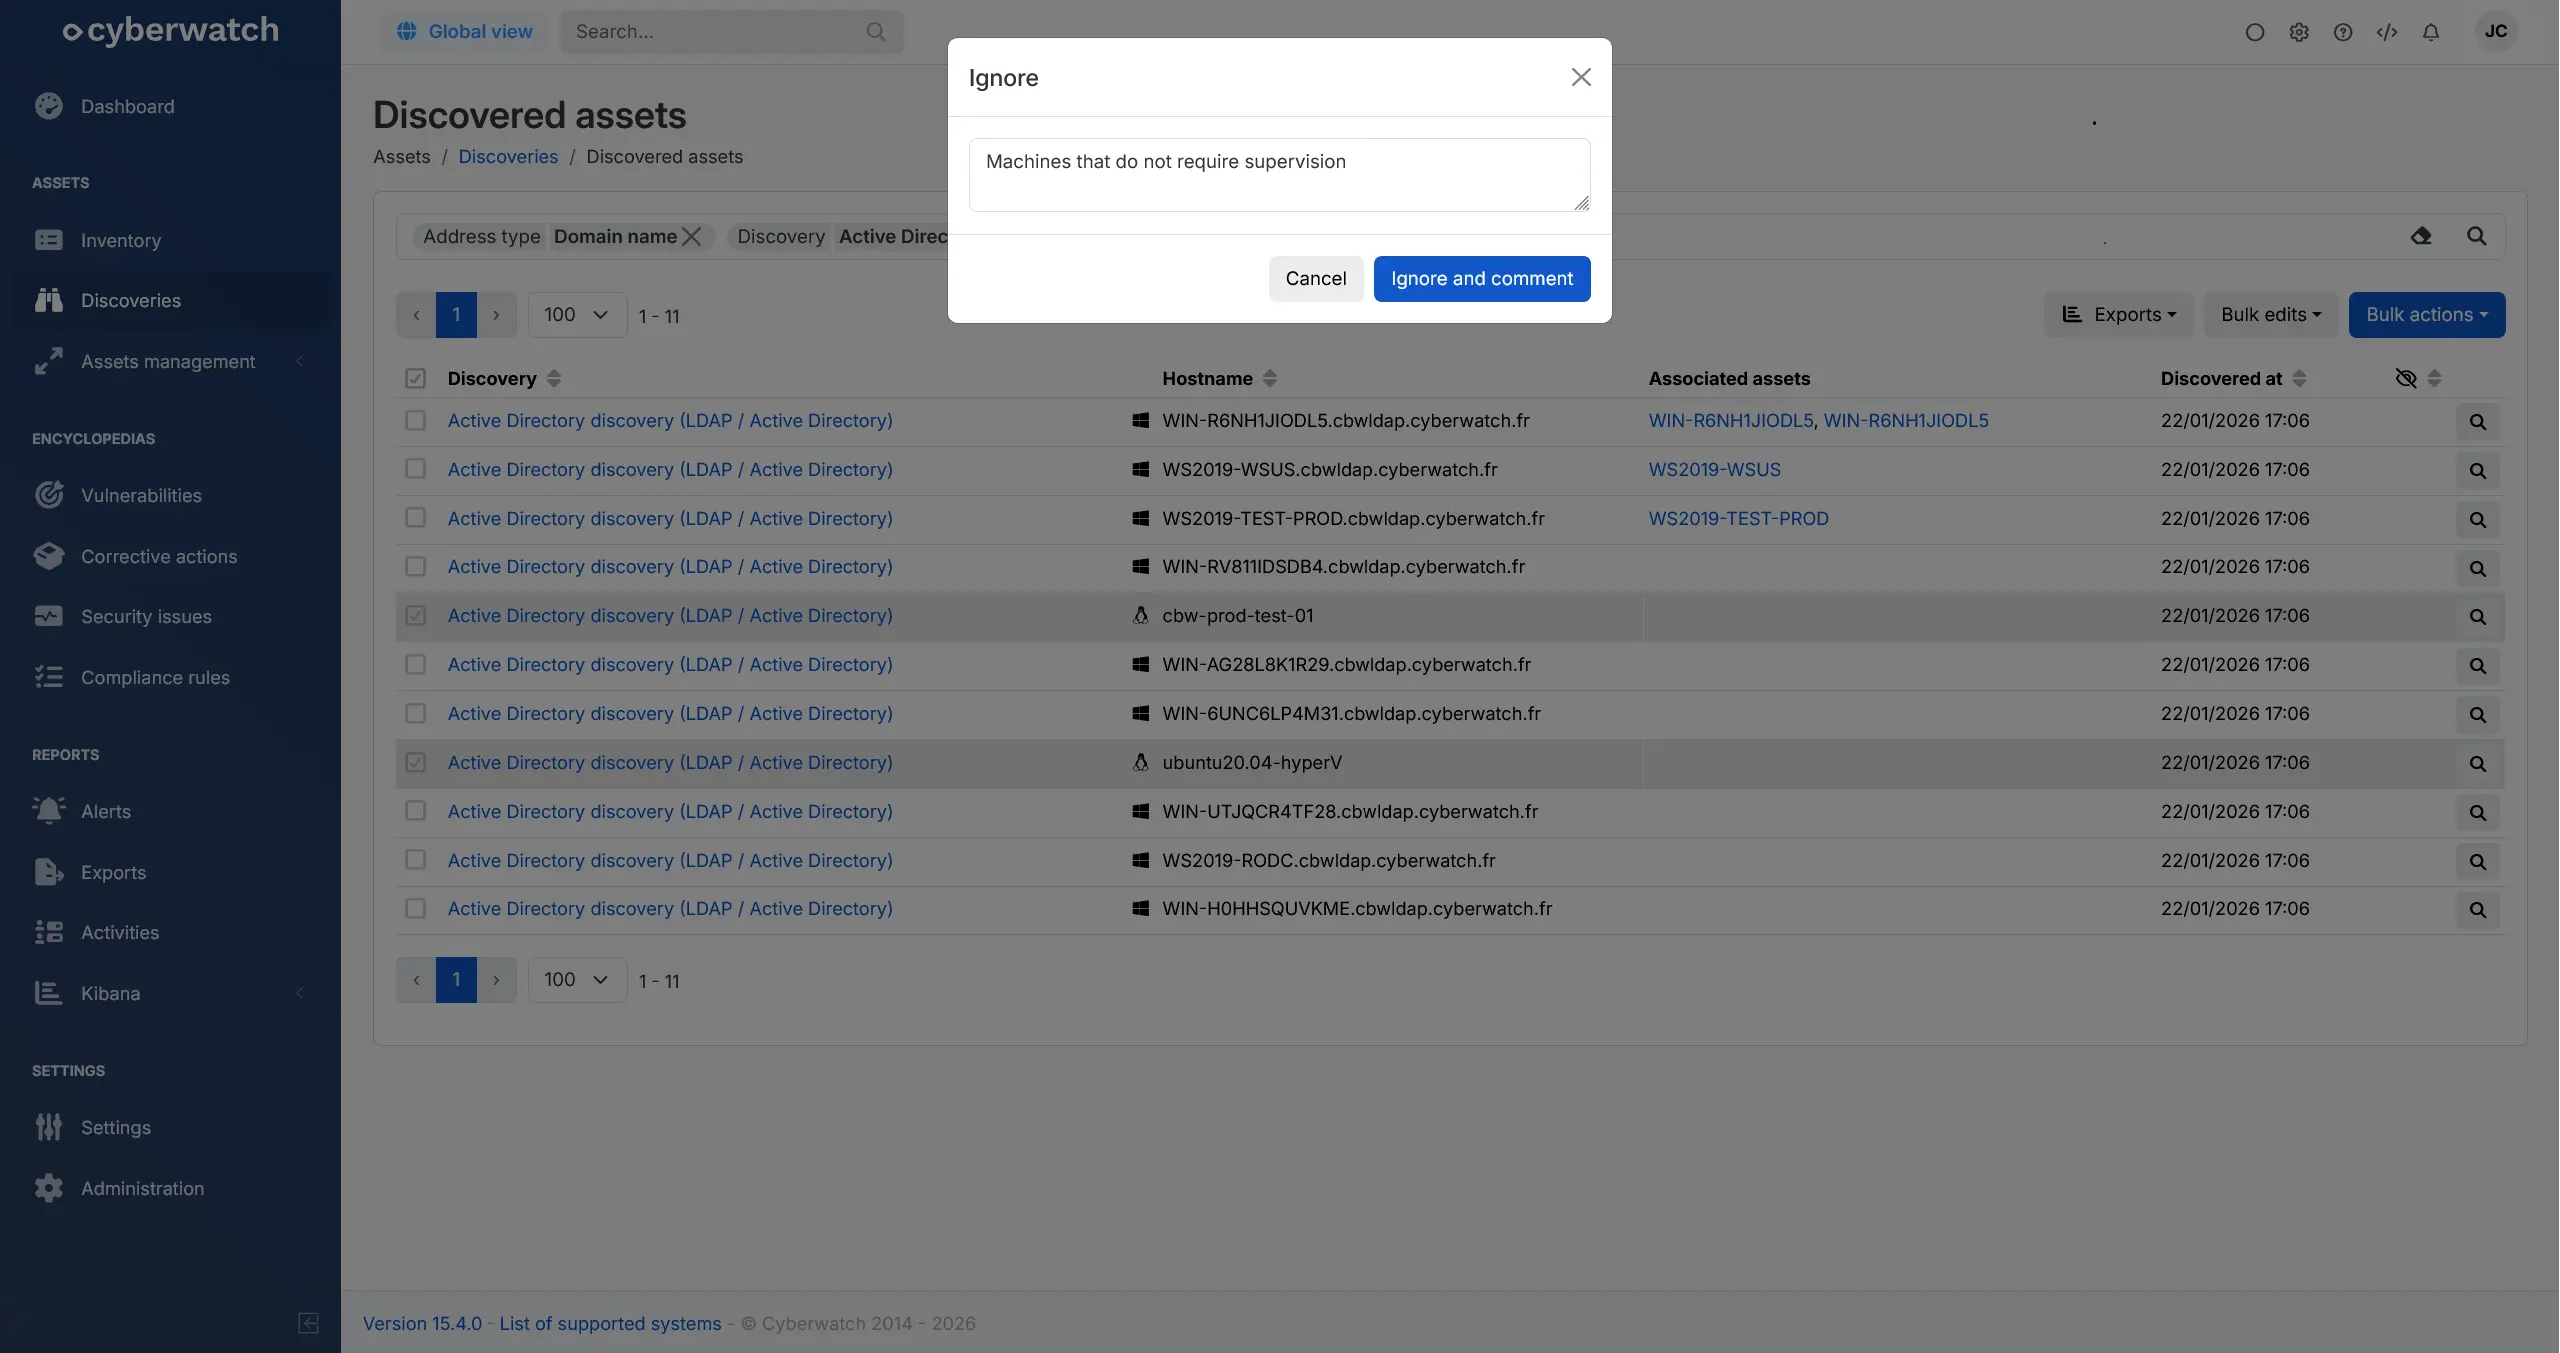
- Discoveries: you can now ignore a discovered asset (preview)
New features:
- Compliance: added and updated multiple CIS Benchmarks, including AlmaLinux 10, Debian 13, Oracle Linux 10, Red Hat Enterprise Linux 10 and Rocky Linux 10
- Discoveries: added UDP-based (SNMP) network discovery
- Scope:
- Added support for CloudLinux 10
- Added support for Fedora 43
- Added support for HPE Aruba Airwave devices
- Added support for IBM InfoSphere Information Server on Windows
- Added support for WALLIX Access Manager devices
Updated features and performance improvements:
- Activities:
- Improved user experience for activity visualization
- The search bar now includes a new time‑based filter for activity CSV export
- API:
- The
/api/v3/servers/{id}/exportroute now returns metadata, groups, and project when exporting an asset in SBOM SPDX or CycloneDX format - The
/api/v3/vulnerabilities/servers/{id}route now returns additional security‑issue payload details and corrective‑action titles for the asset - The ARN role can now be provided when creating or updating an AWS SSM agentless connection
- The
- Cloud environment compliance: implemented new Microsoft 365 compliance rules
- Compliance: updated the behavior and applicability of custom rules
- Discoveries:
- Execution timeout is now displayed in network or industrial safe queries discovery details
- IP addresses of assets identified during network discovery are now always displayed in the application, alongside the hostname when available
- Pod annotations and labels are now reported for Kubernetes discoveries
- Docker images: removed support for external runtime engines; all scans now run exclusively through the application’s native scanner
- Network targets and websites: additional URLs can now be specified for scanning
- Scanning engine: Snap applications are now supported on compatible Linux distributions
Bugfixes:
- Agentless connections: fixed detection issues for Check Point and Opengear devices via SNMP
- API: fixed an issue affecting compliance scans performed by security administrators
- Assets rules: fixed an issue preventing rule execution during asset creation in agentless connection
- Corrective actions: fixed the Windows package manager support for third-party application updates
- Discoveries: fixed an automatic asset registration issue for Proxmox discoveries
- Scanning engine: fixed Red Hat systems detection and analysis
15.3 (2025-12-15)
Highlighted features:
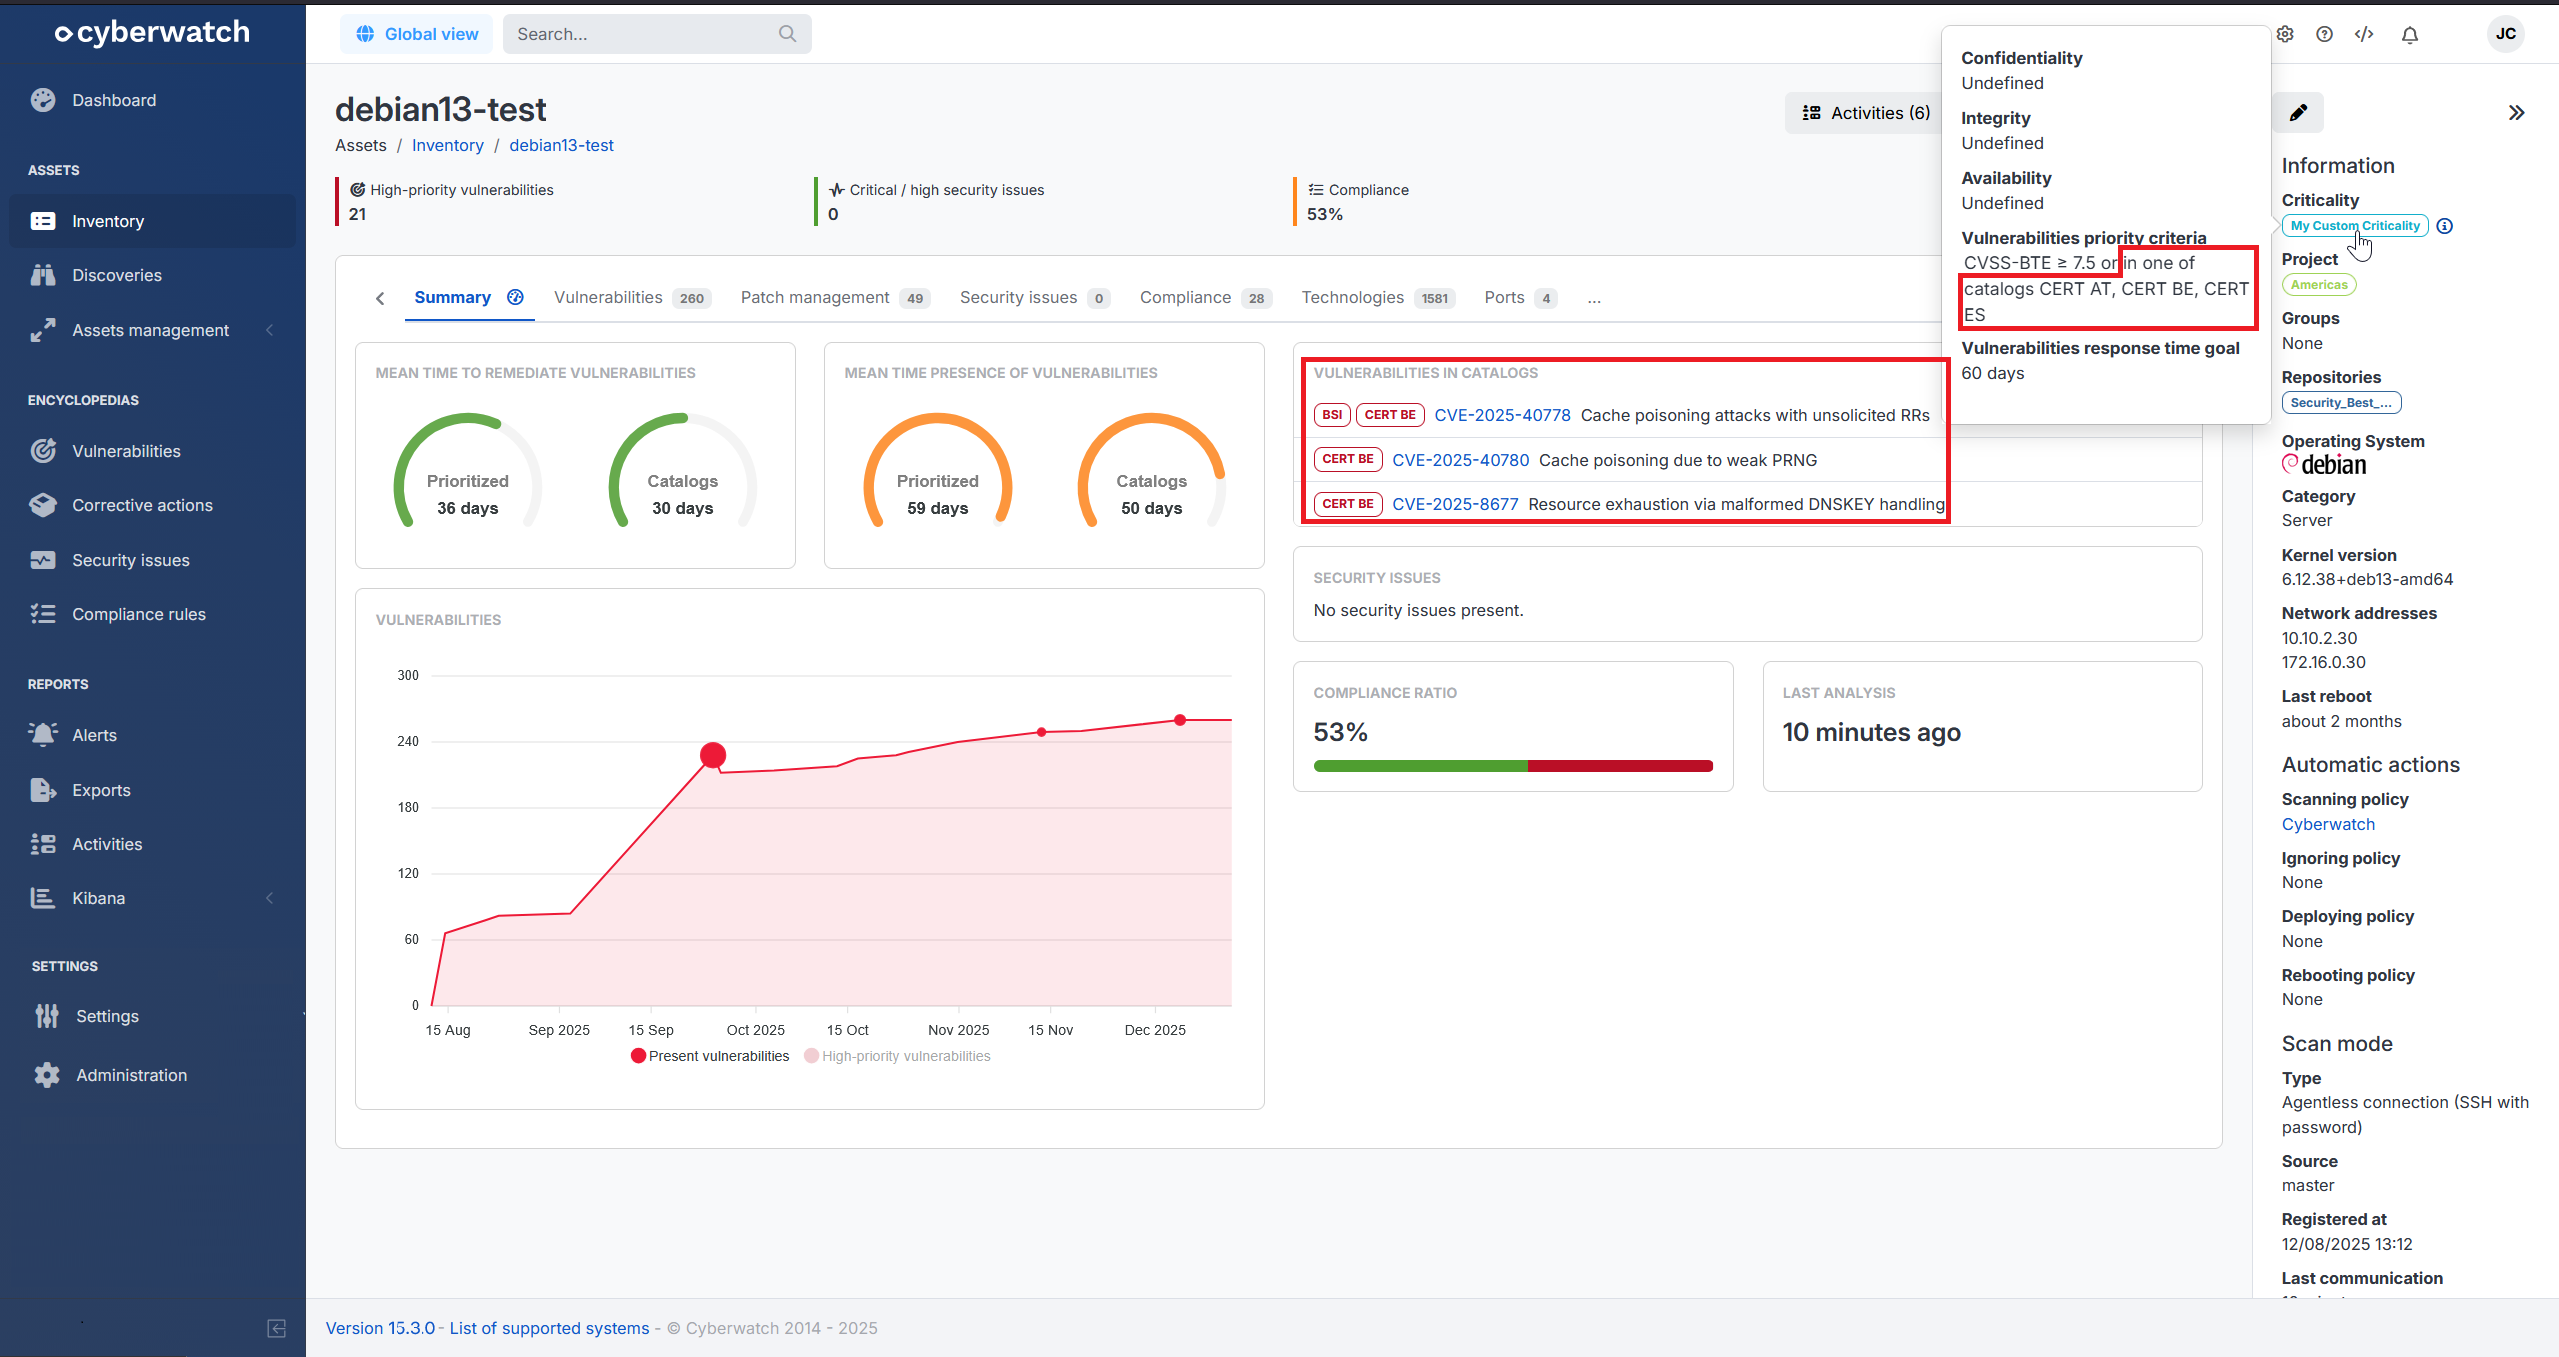
- Criticalities: you can now integrate European CERT catalogs into vulnerability prioritization (preview)
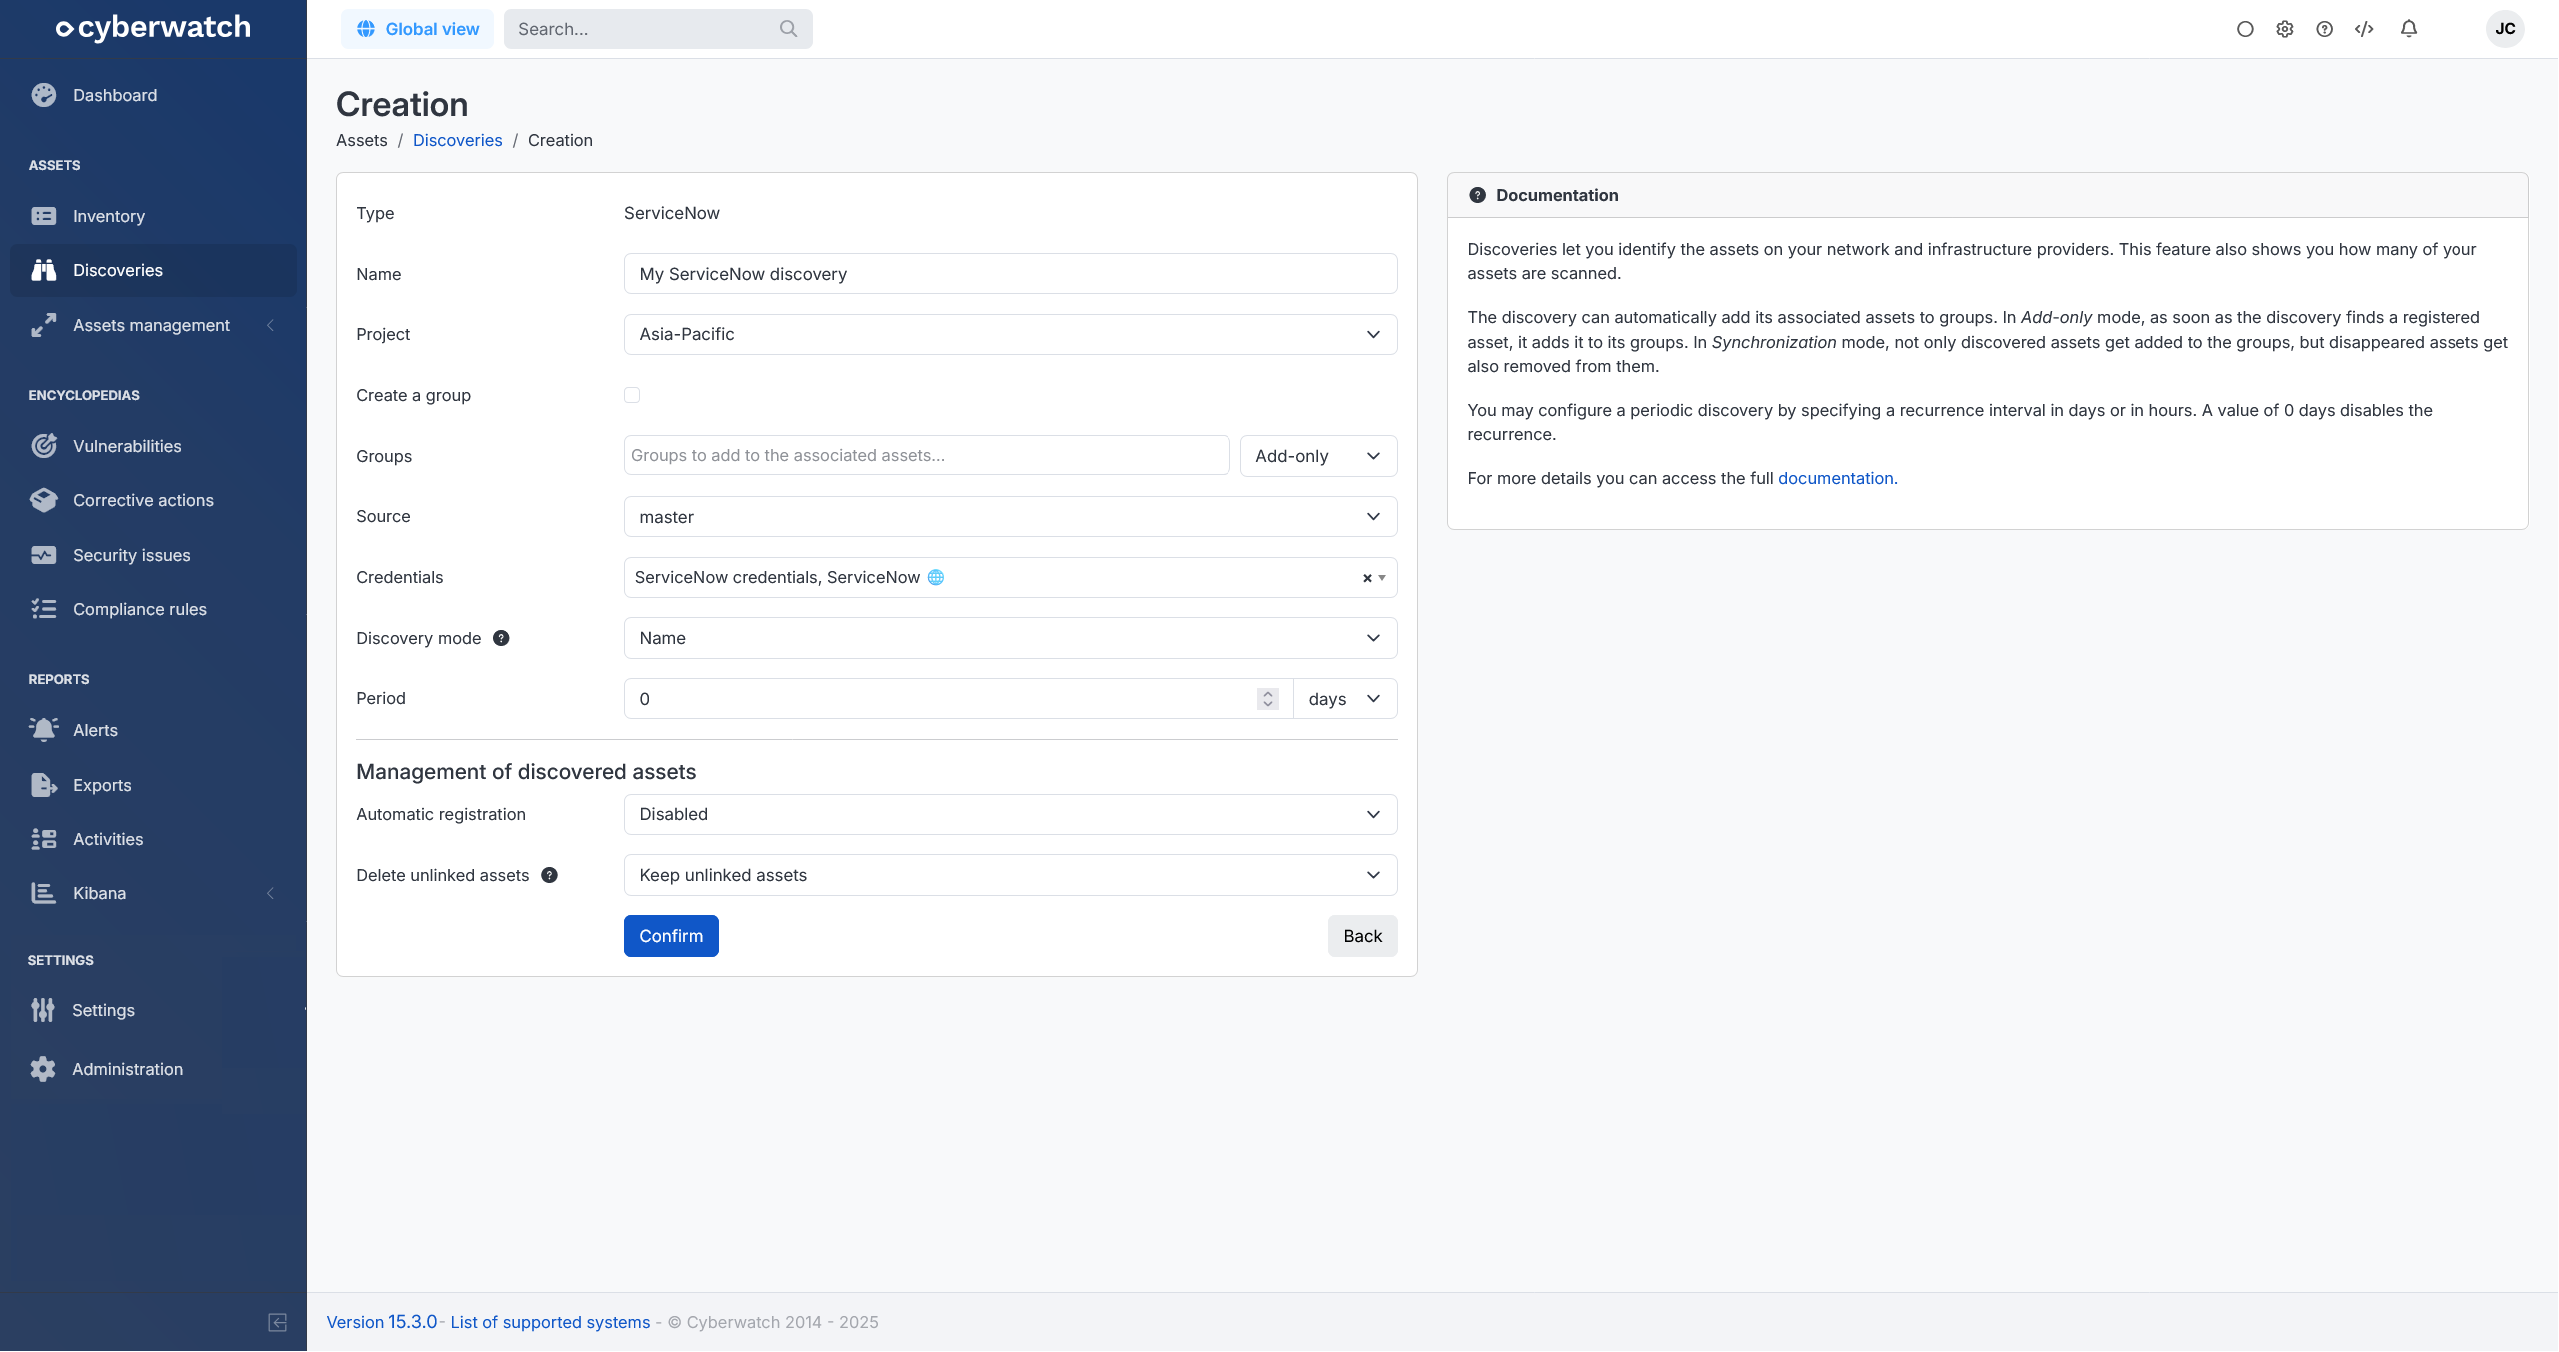
- Discoveries: added ServiceNow discovery (preview)
New features:
- Agentless connections: added support for HashiCorp Vault KV v2
- Air-gapped assets: you can now import PortSwigger Burp Suite XML vulnerability reports as air-gapped assets
- API: added a route for importing air-gapped assets
- Cloud environment compliance: added new Microsoft 365 compliance rules for multi-factor authentication
- Scope:
- Added support for Cisco Identity Services Engine devices
- Added support for Fortinet FortiWeb devices
- Added support for Microsoft Configuration Manager client on Windows
- Added support for Microsoft Office 2024
- Added support for MobaXterm on Windows
Updated features and performance improvements:
- Administration: refactored SMTP configuration form
- API: the
/api/v3/users/{id}route now returns the list of accessible projects for the user - Cloud: the wizard also offers the option to create Entra ID credentials for certificate-based authentication on Microsoft Azure or Microsoft 365
- Network targets and websites:
- Enhanced detection of various CMS systems
- Improved error management in case the target is unavailable
- You can create stored credentials for the target from the creation form
- Compliance:
- A security administrator can now ignore compliance rules
- Updated multiple CIS Benchmarks
- Harbor: you can disable the use of the proxy for image analysis
- Integrations: UX improvements on the creation form
- MITRE ATT&CK: Cyberwatch now relies on attack techniques from ATT&CK version 18
- Users: strengthened password complexity requirements
Bugfixes:
- Agentless connections: fixed the Fortinet FortiGate device detection
15.2 (2025-11-12)
New features:
- API:
- Compliance benchmark management is now possible
- Introduced routes for creating an API key and retrieving connected user key information
- Scope:
- Added support for Broadcom Brocade devices
- Added support for Fortinet FortiSwitch devices
- Added support for macOS 26
- Added support for Microsoft Visual C++ Redistributable
- Added support for Oracle Linux 10
- Added support for SBC Mediant Audiocodes devices
- Added support for Ubuntu 25.10
Updated features and performance improvements:
- API: implemented new routes for full compliance repository management
- Cloud: improved cloud resource loading performance
- Discoveries: you can now define scan timing for network discoveries
- Integrations: you can now retrieve technologies affected by a CVE
- Network targets and websites: improved detection of various CMS systems
- Projects: a system administrator with limited access can now download analysis scripts for adding air gap assets
- Repositories: you can now add a description to a repository
- Vulnerability and security issues encyclopedia: the search bar includes new time-based filters
Bugfixes:
- Authentication provider: fixed a problem with project association through SAML user groups
- Users: fixed an issue preventing the time zone defined in the profile from being applied correctly
15.1 (2025-10-06)
Highlighted features:
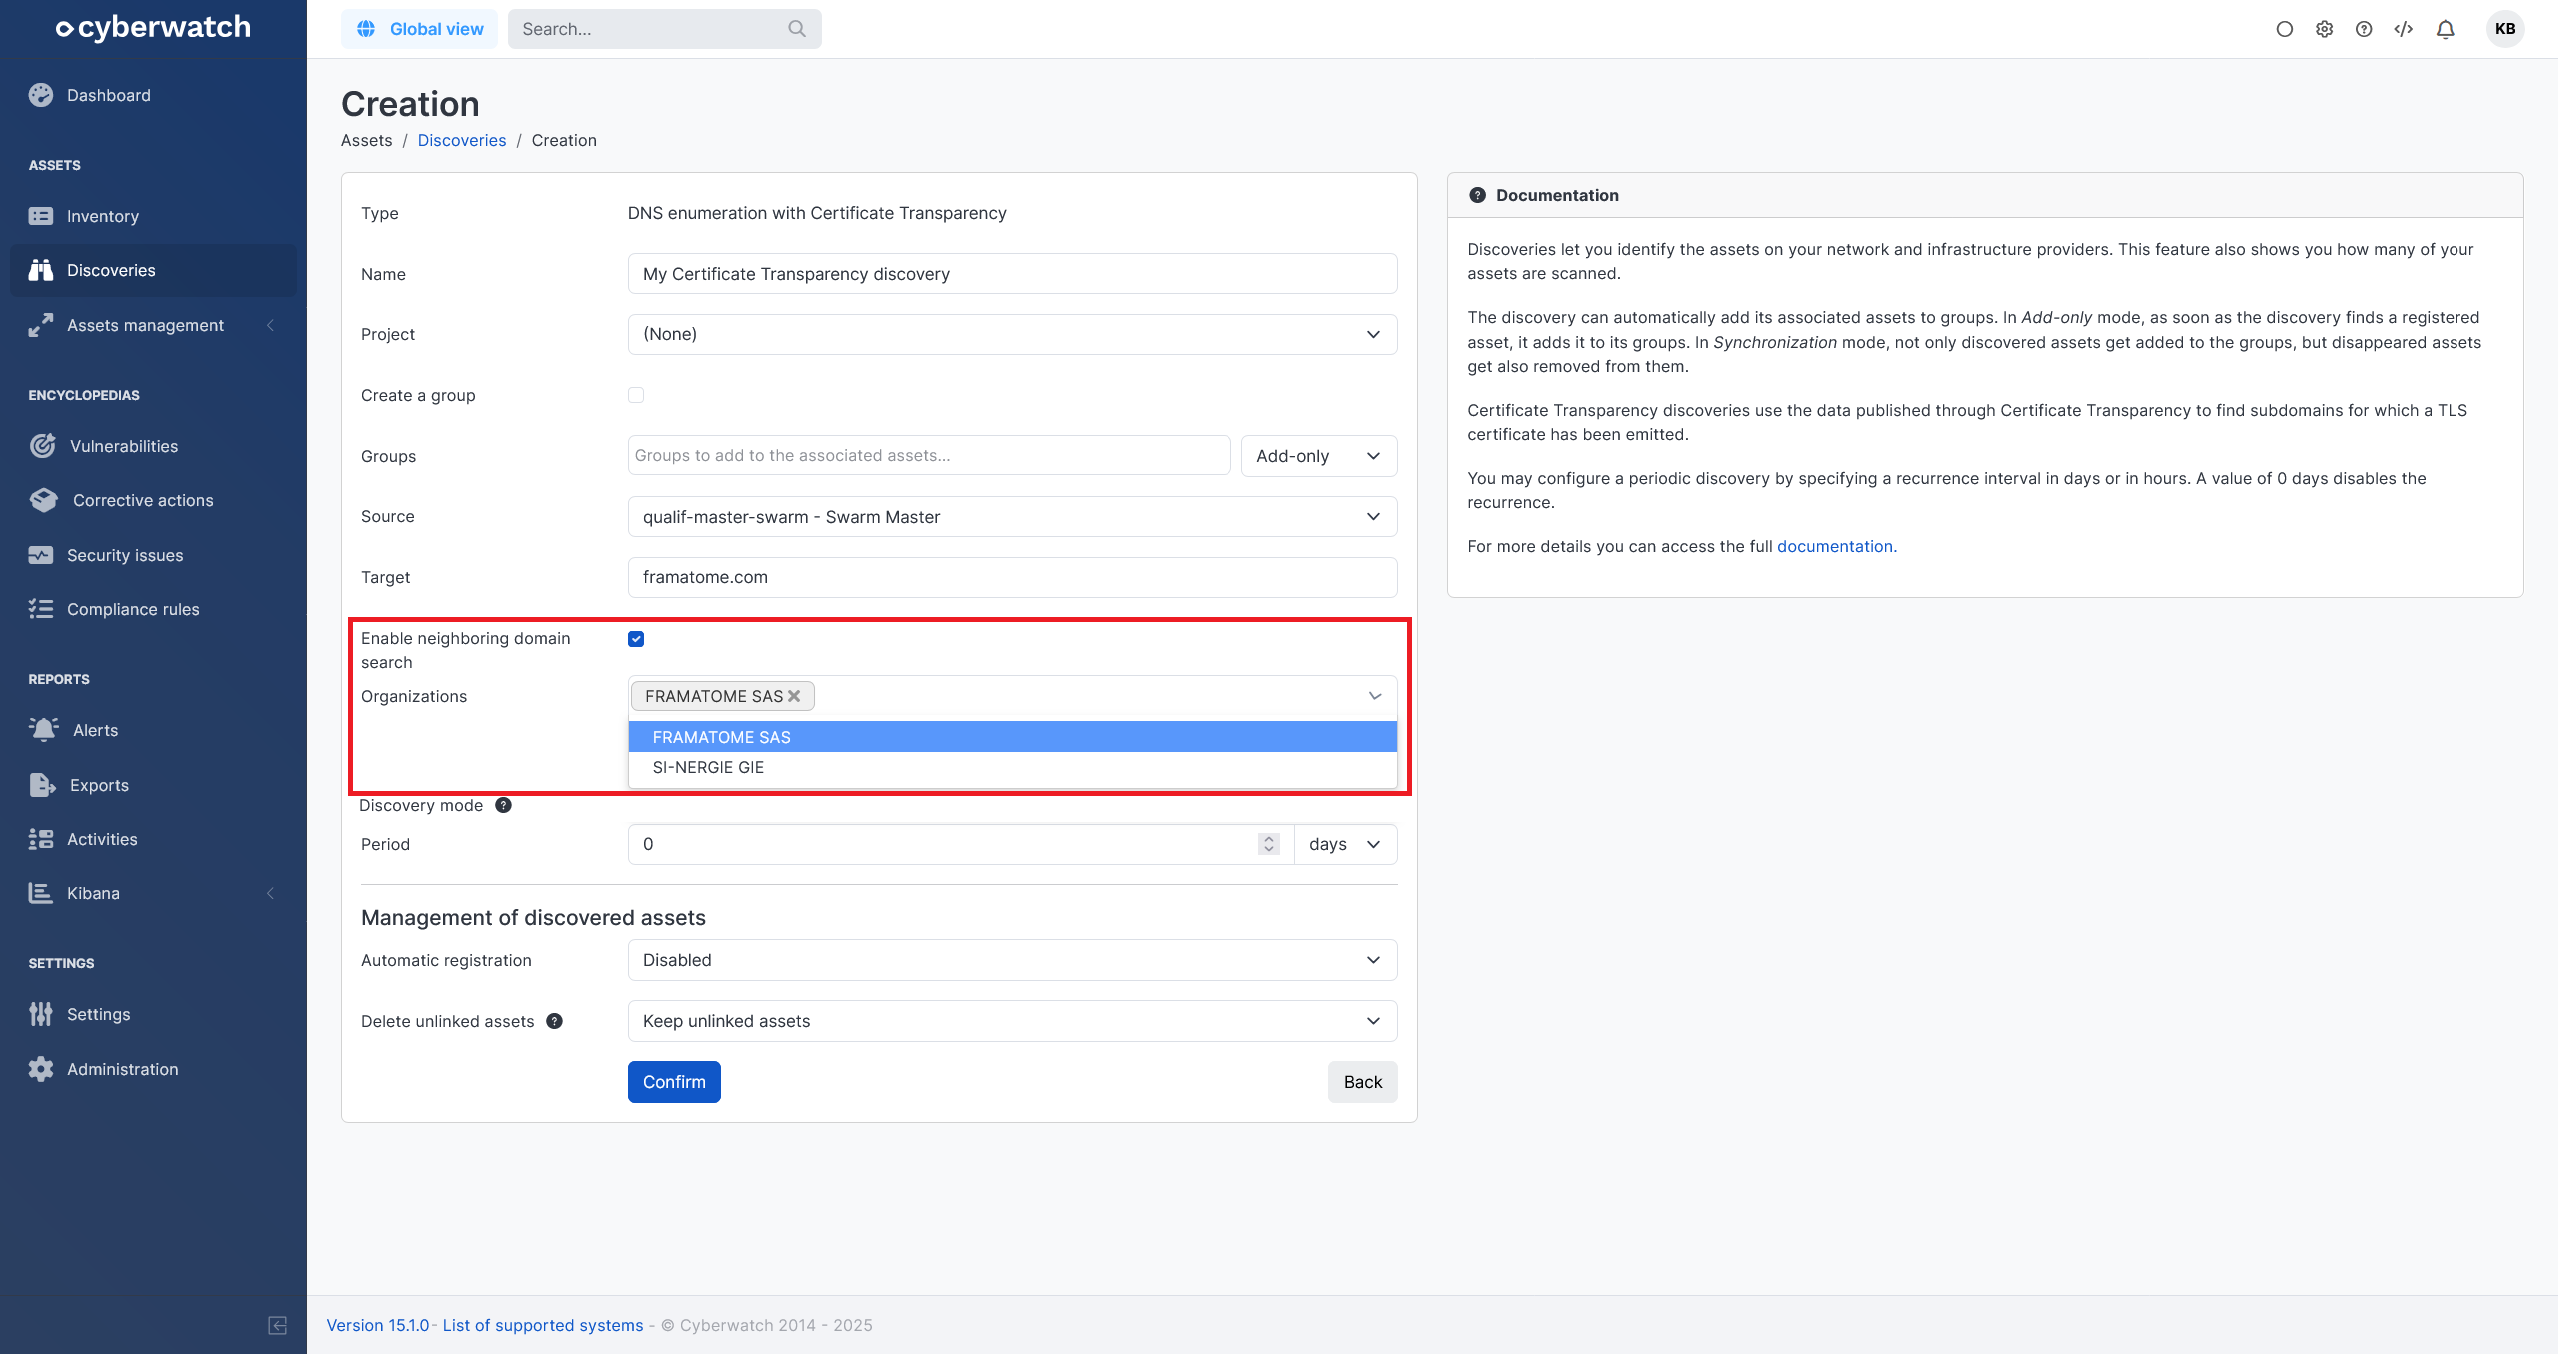
- Discoveries: Certificate Transparency discovery now offers a new option to search for neighboring organizations (preview)
New features:
- API: added a route to retrieve compliance repository information
- Compliance: added CIS Azure Kubernetes Service (AKS) Benchmark
- Details of an Asset: you can sort by date in the patch management history
- Discoveries: added a Rancher discovery
- Scope:
- Added support for OPNsense devices
- Added support for Trend Micro Deep Security Agent on Windows
Updated features and performance improvements:
- Cloud: CloudFormation template now ensures EKS compliance across all discovered clusters
- Compliance: CERTFR_AD analysis now takes into account sub-organizational units for domain controllers
- Projects:
- A system administrator with limited access can now manage deployment and restart policies of their accessible projects
- A system administrator with limited access can now manage scan policies of their accessible projects
Bugfixes:
- Cloud environment compliance:
- Cloud EKS assets will now have AWS as the operating system
- Fixed the script of CIS-Microsoft365-2.1.7 rule
15.0 (2025-09-29)
This version is a major release.
Highlighted features:
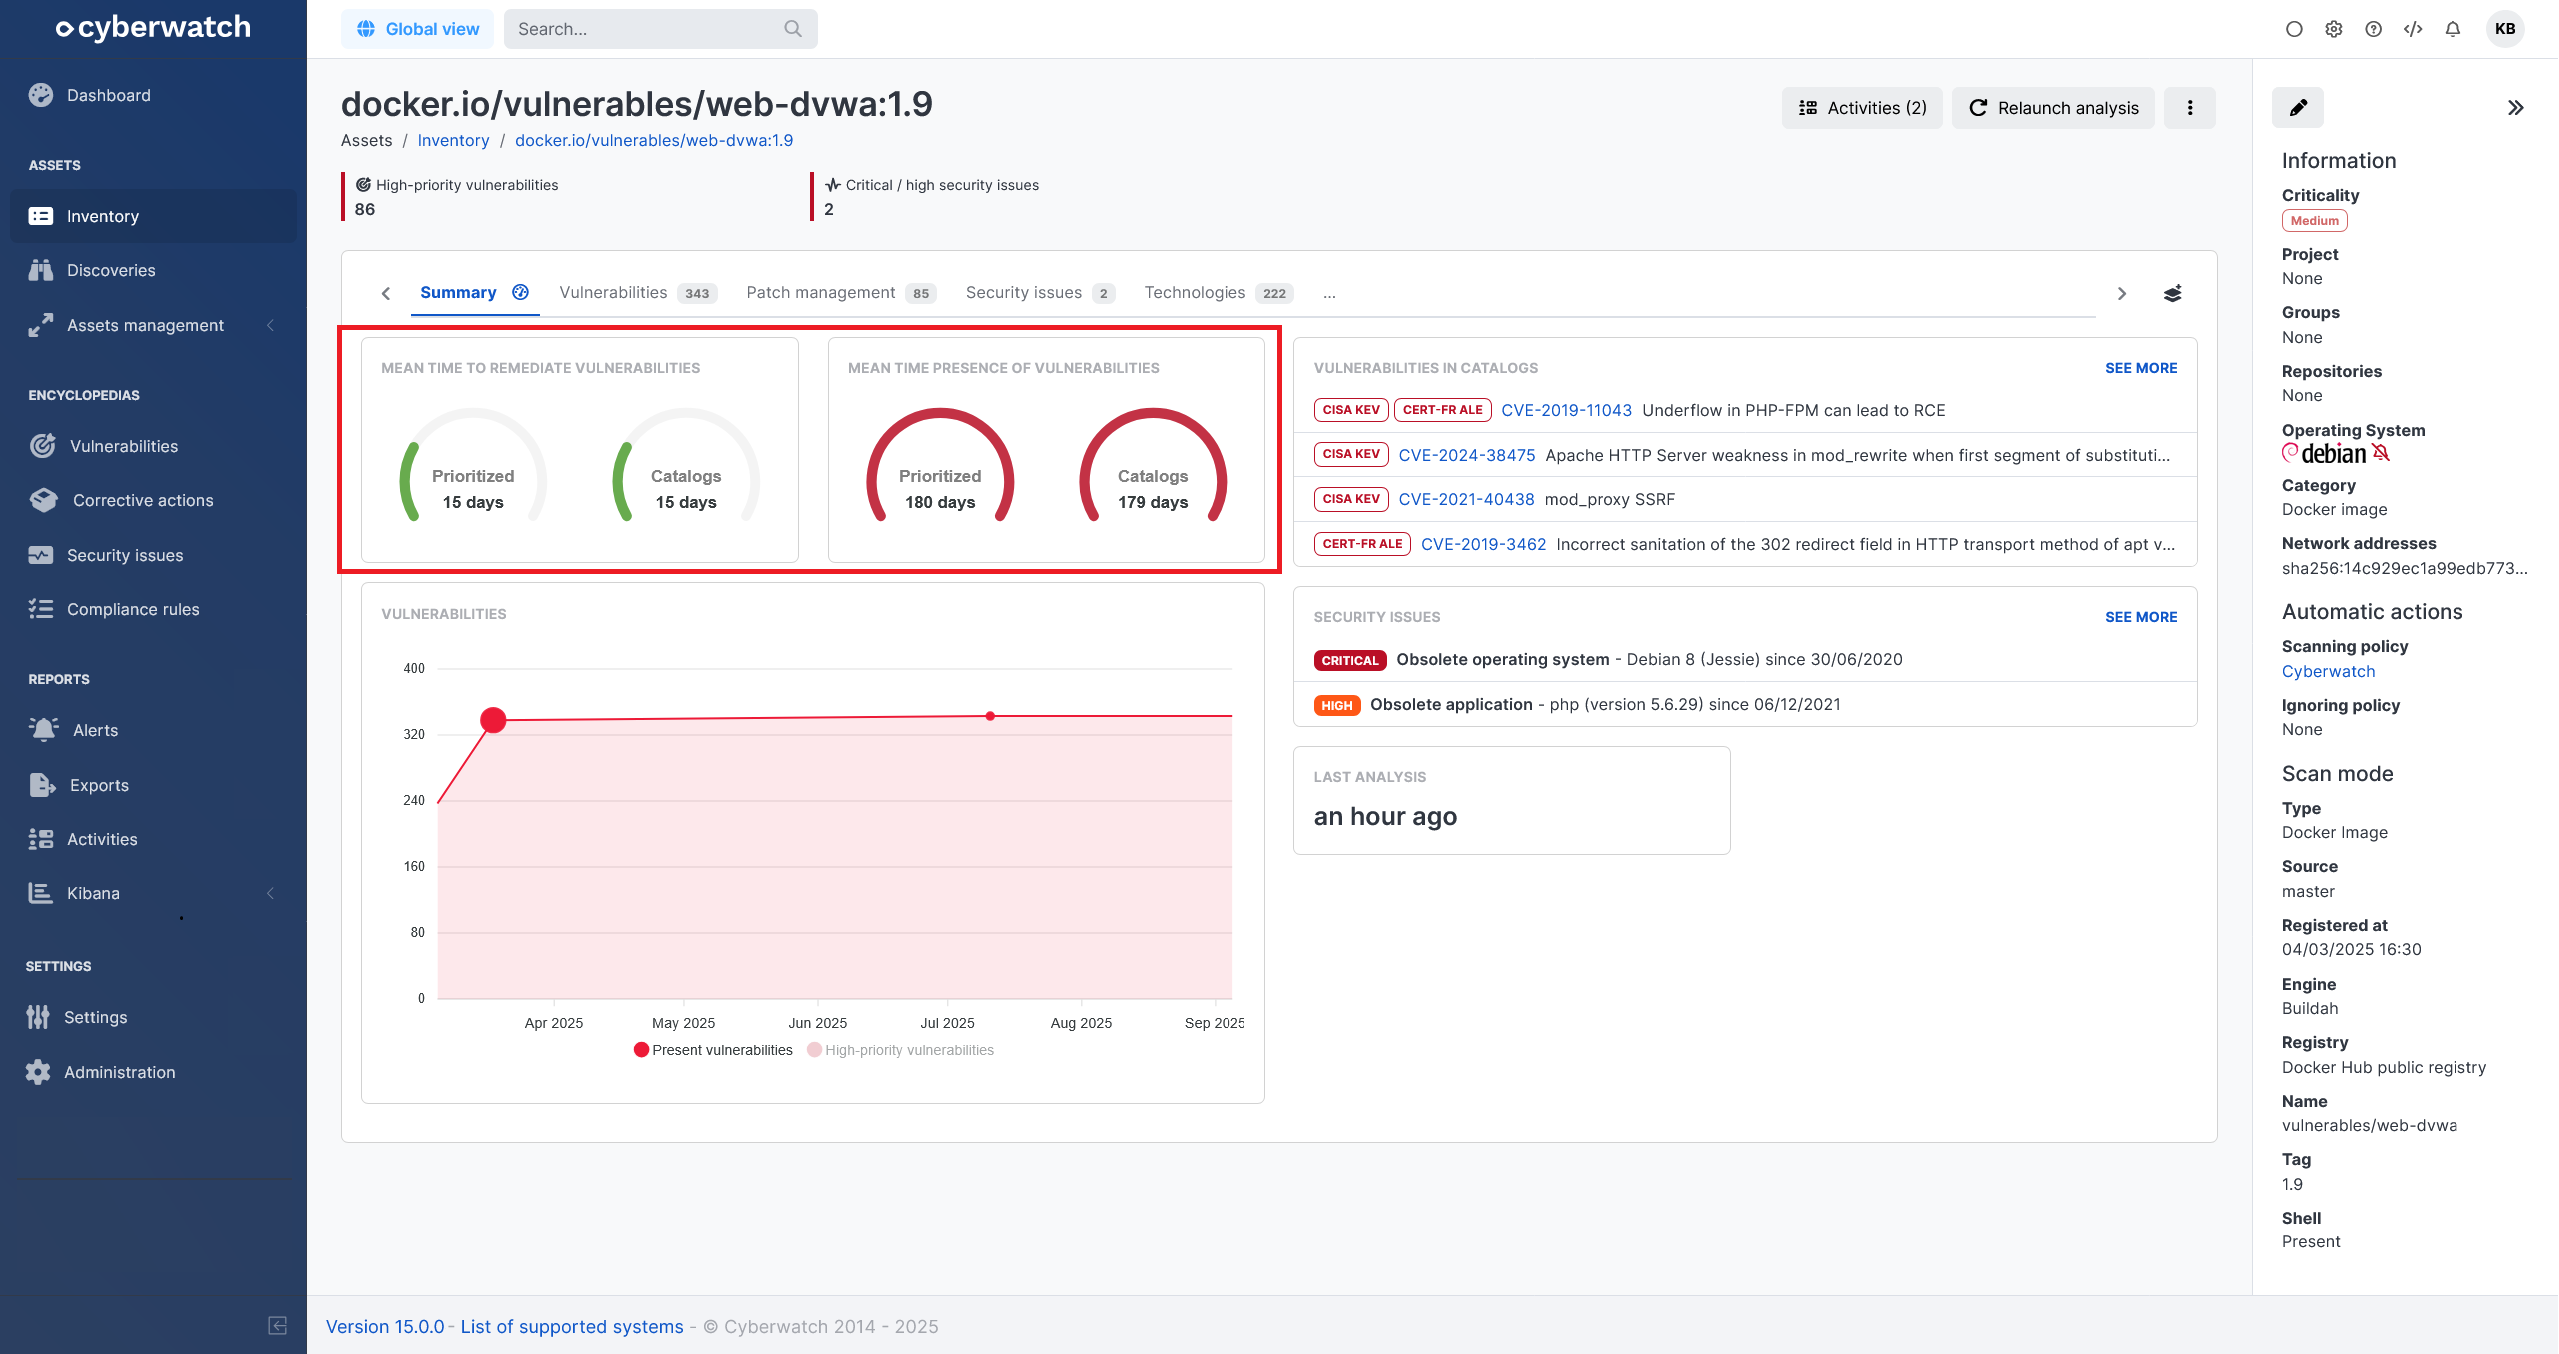
- Assets: add velocity indicators to track response times to vulnerabilities based on defined objectives (preview)
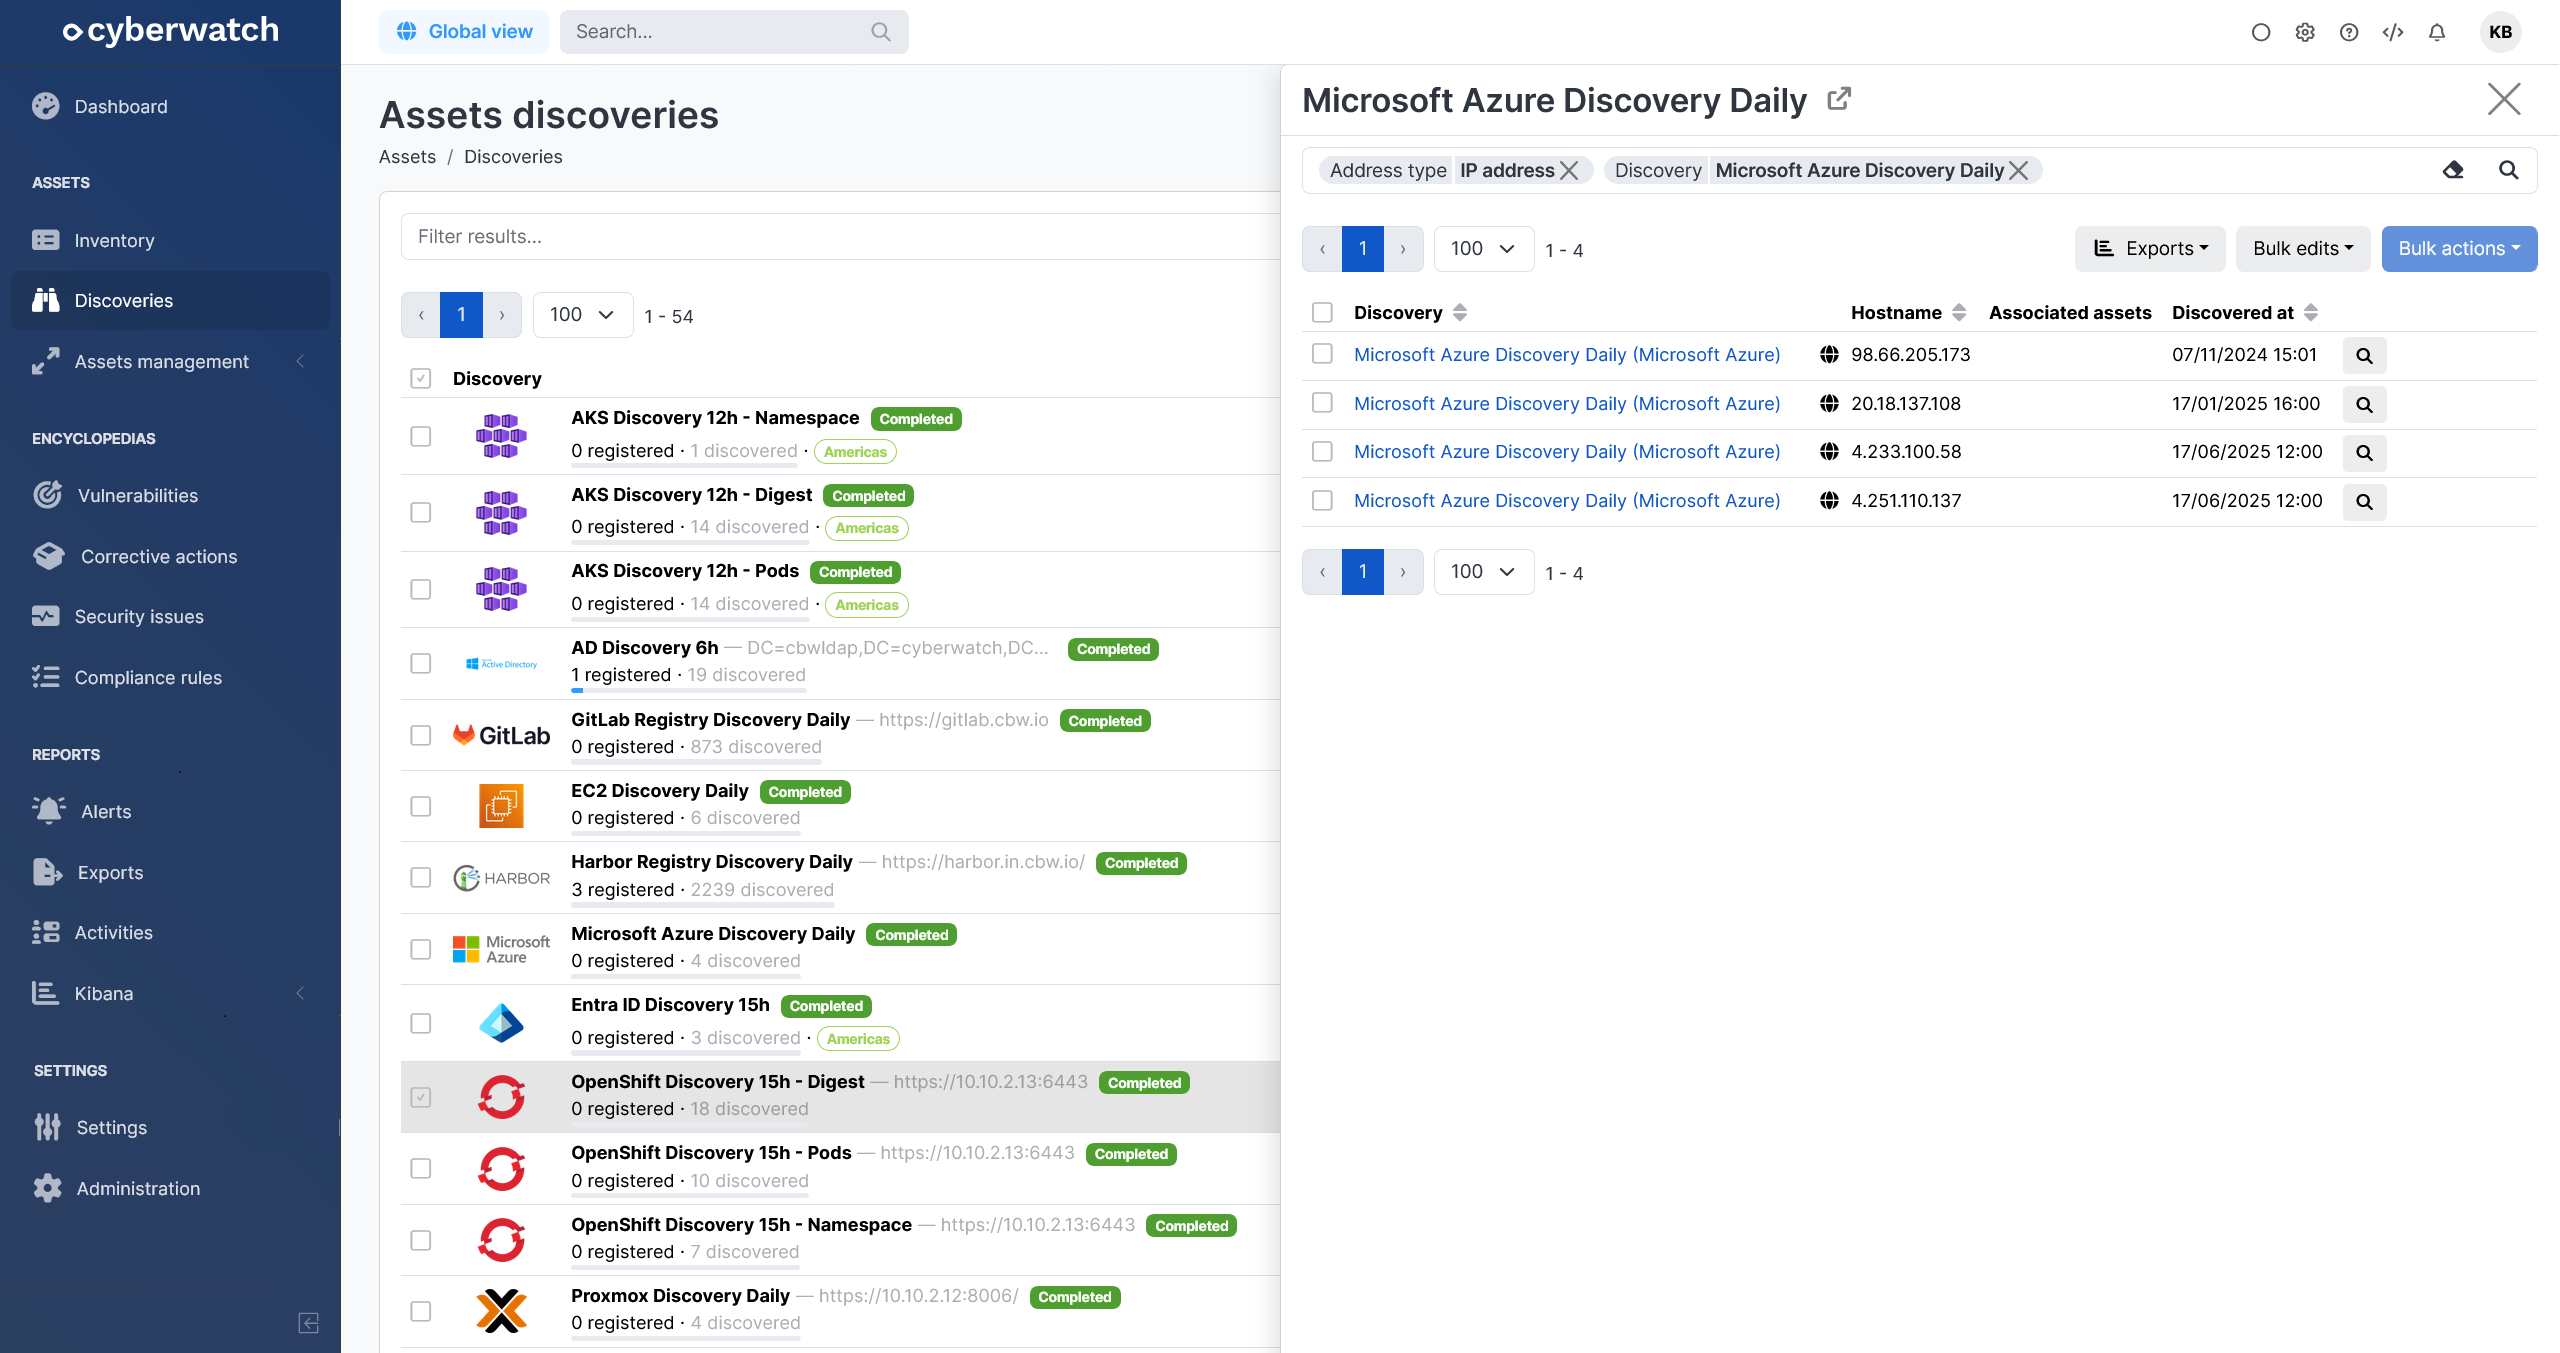
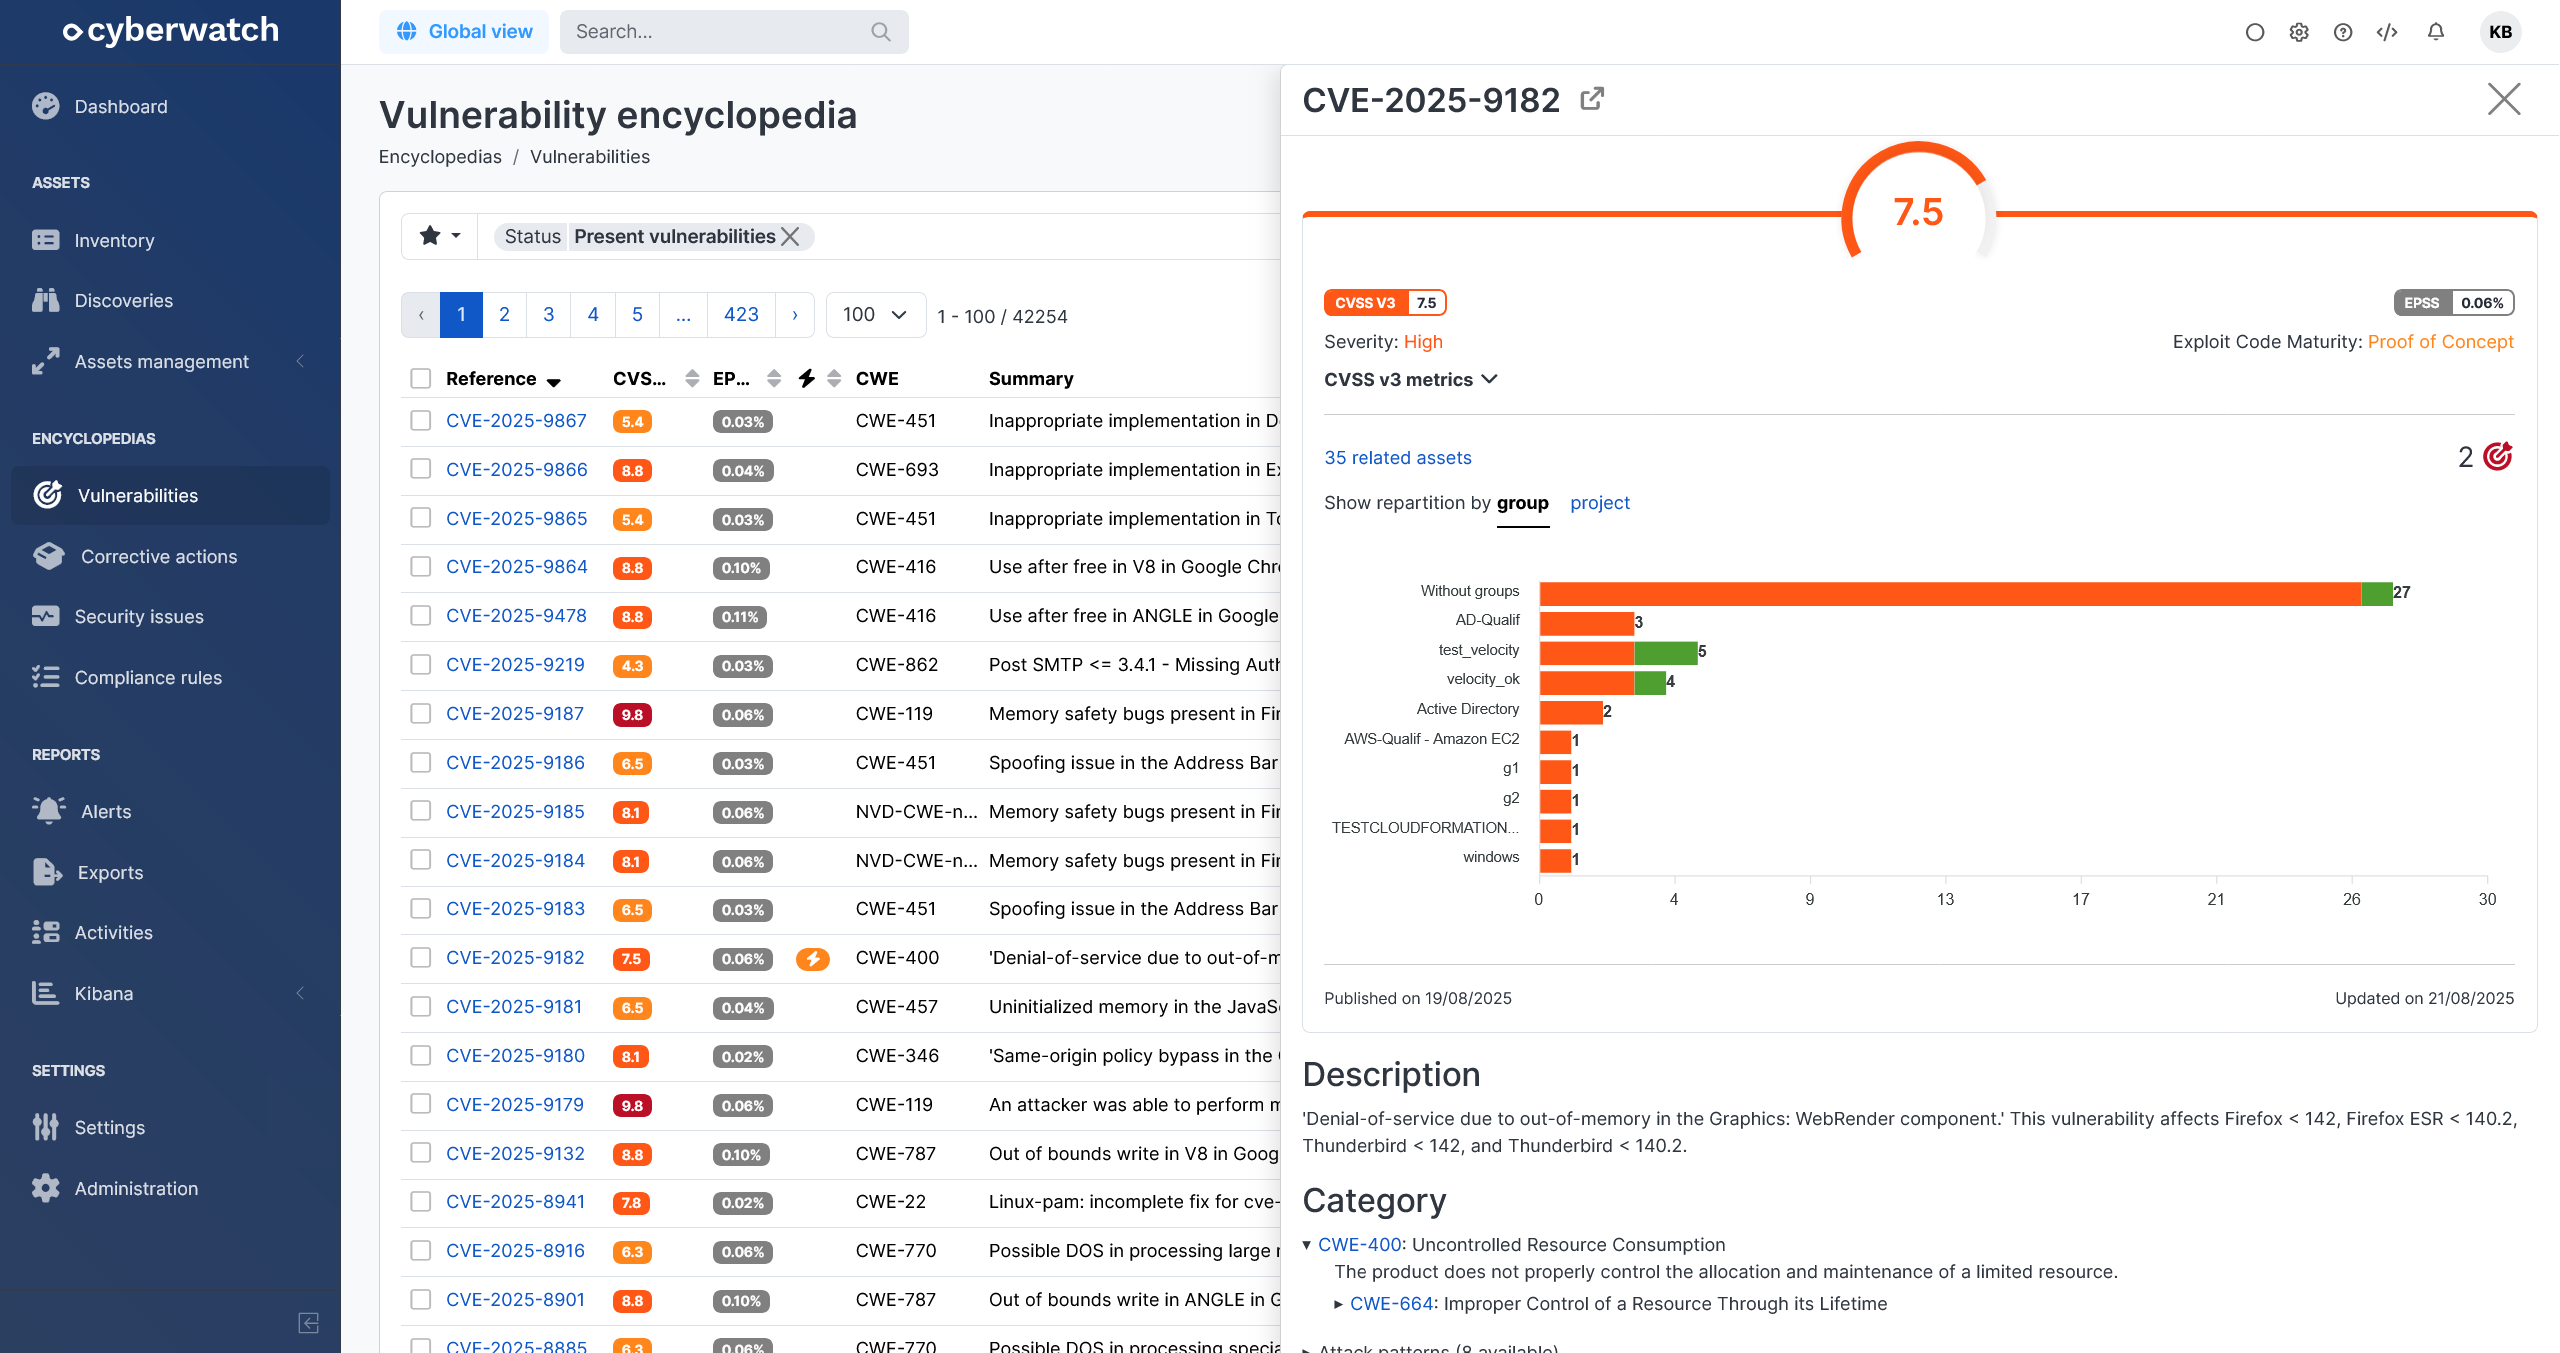
- UX: selecting a CVE, corrective action, security issue, compliance rule, or discovery from the list or the details of an Asset opens a side panel displaying the corresponding detailed information (preview) (preview)
- Projects: multiple improvements, including project-stored credentials, now offering system administrators with limited access the ability to add assets for all application scan modes
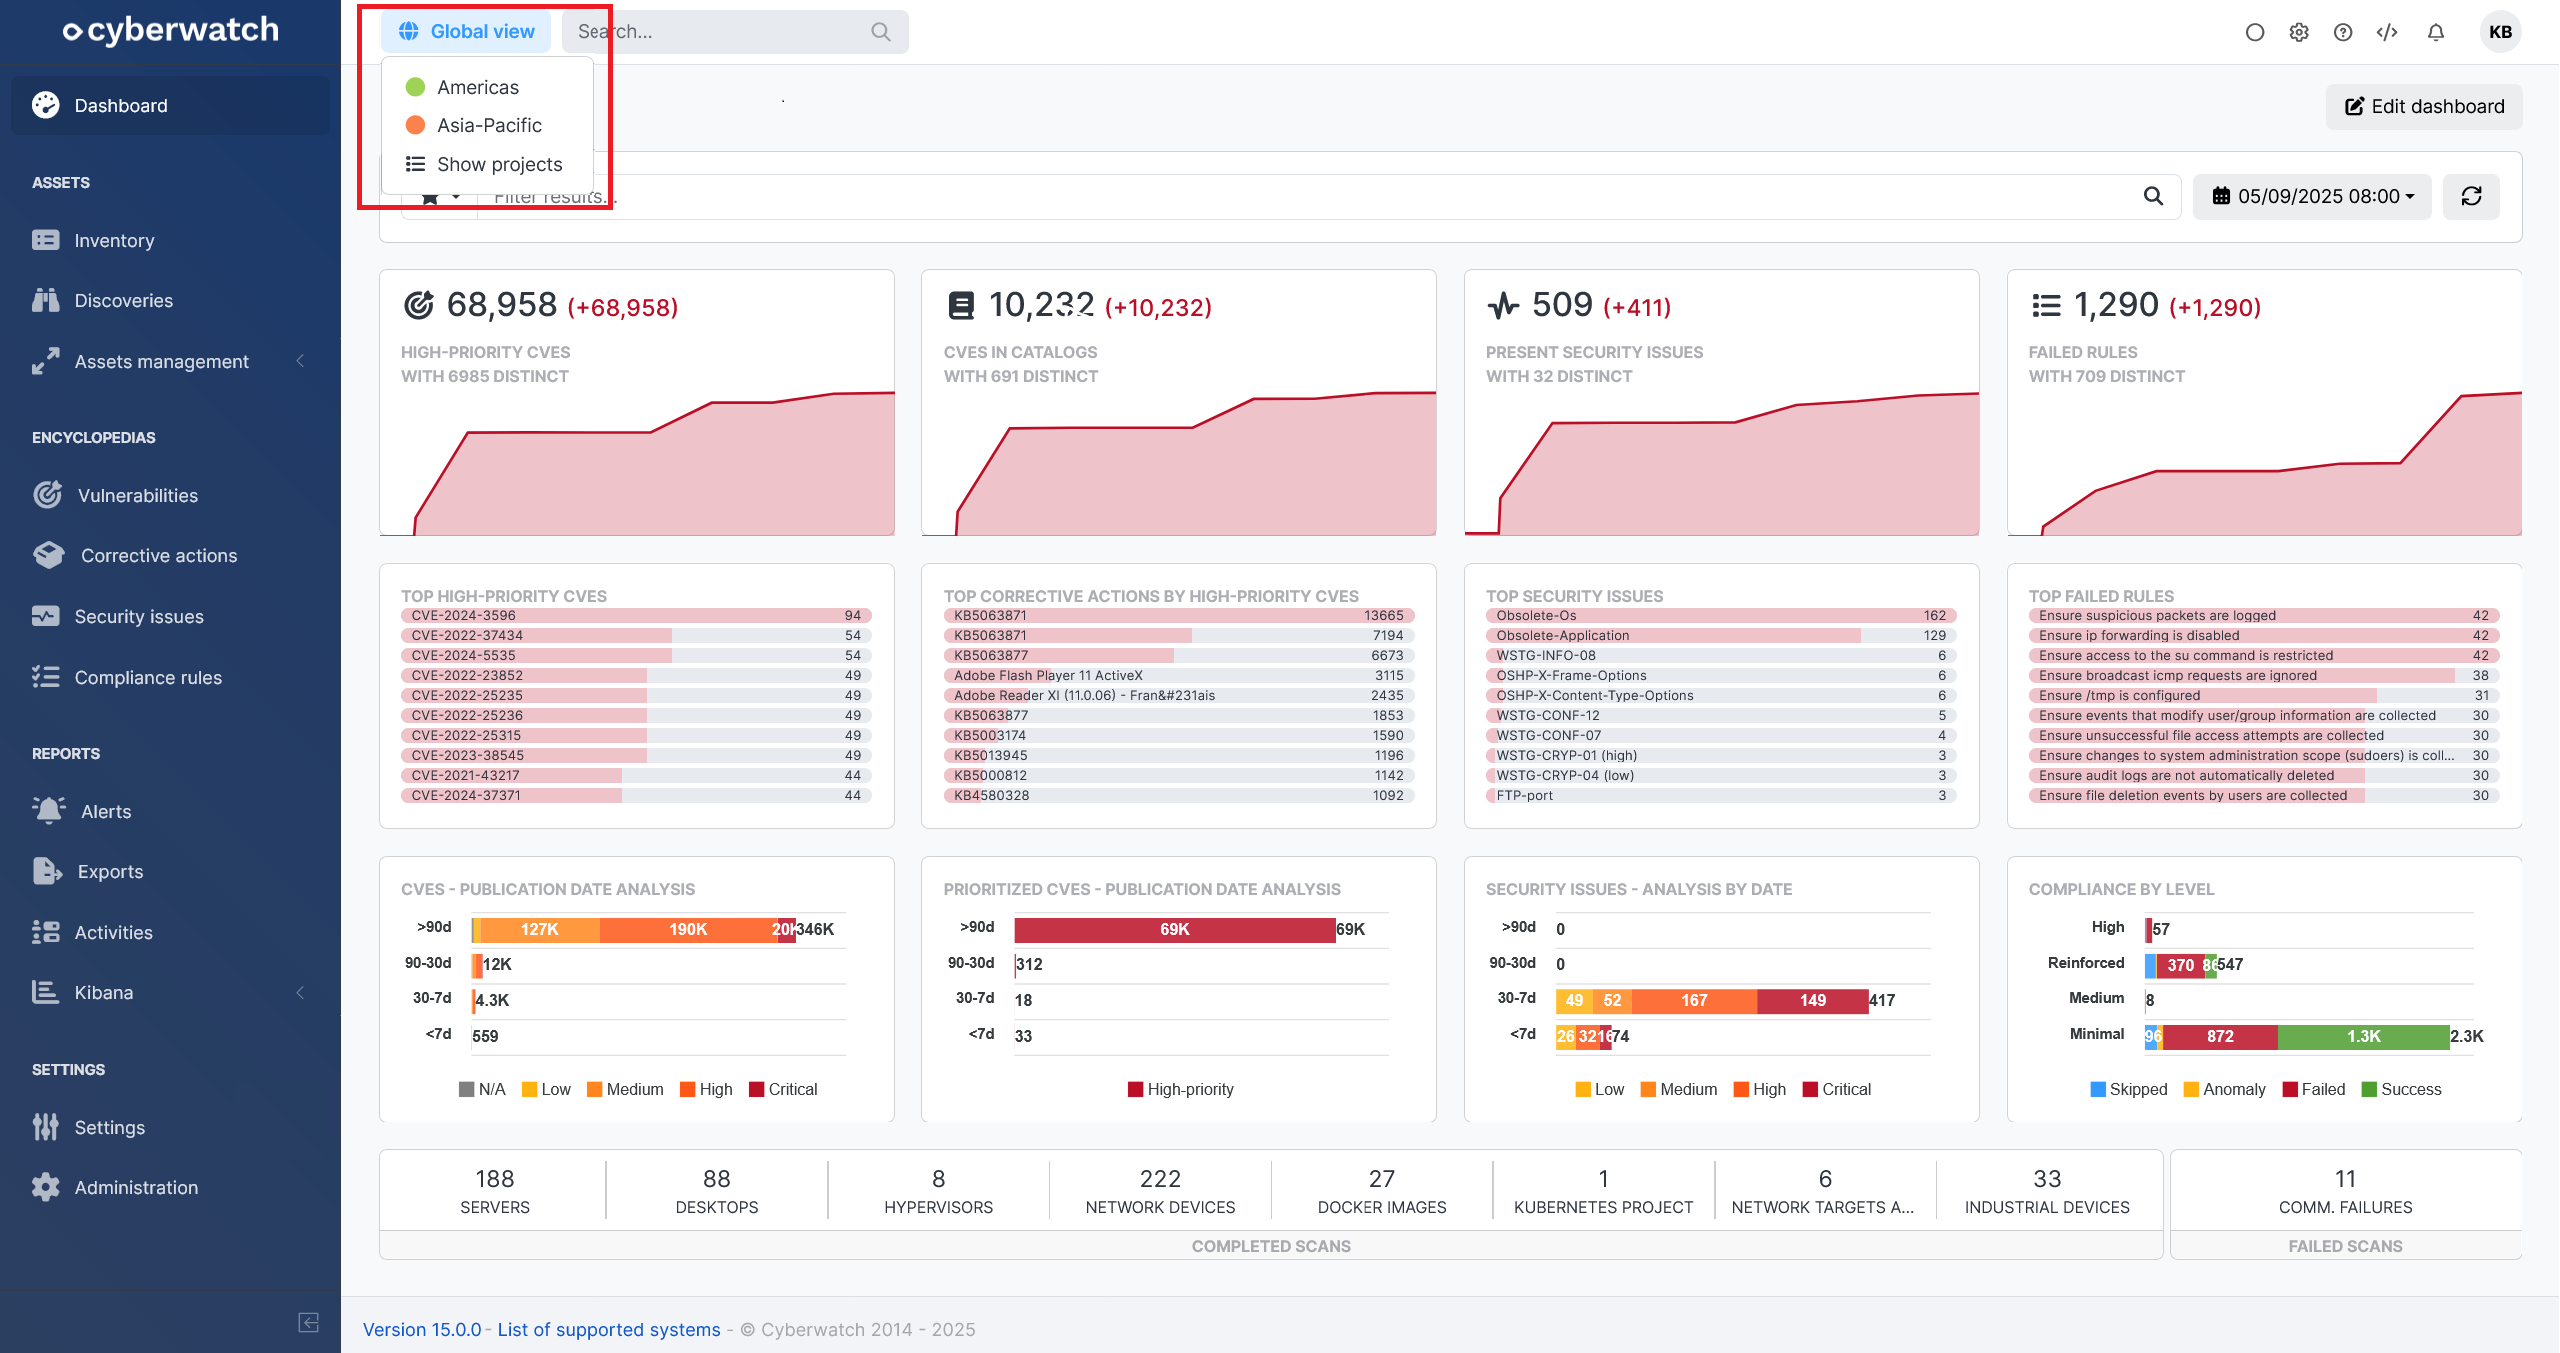
- UX: project activation in context is now more visible in the application (preview)
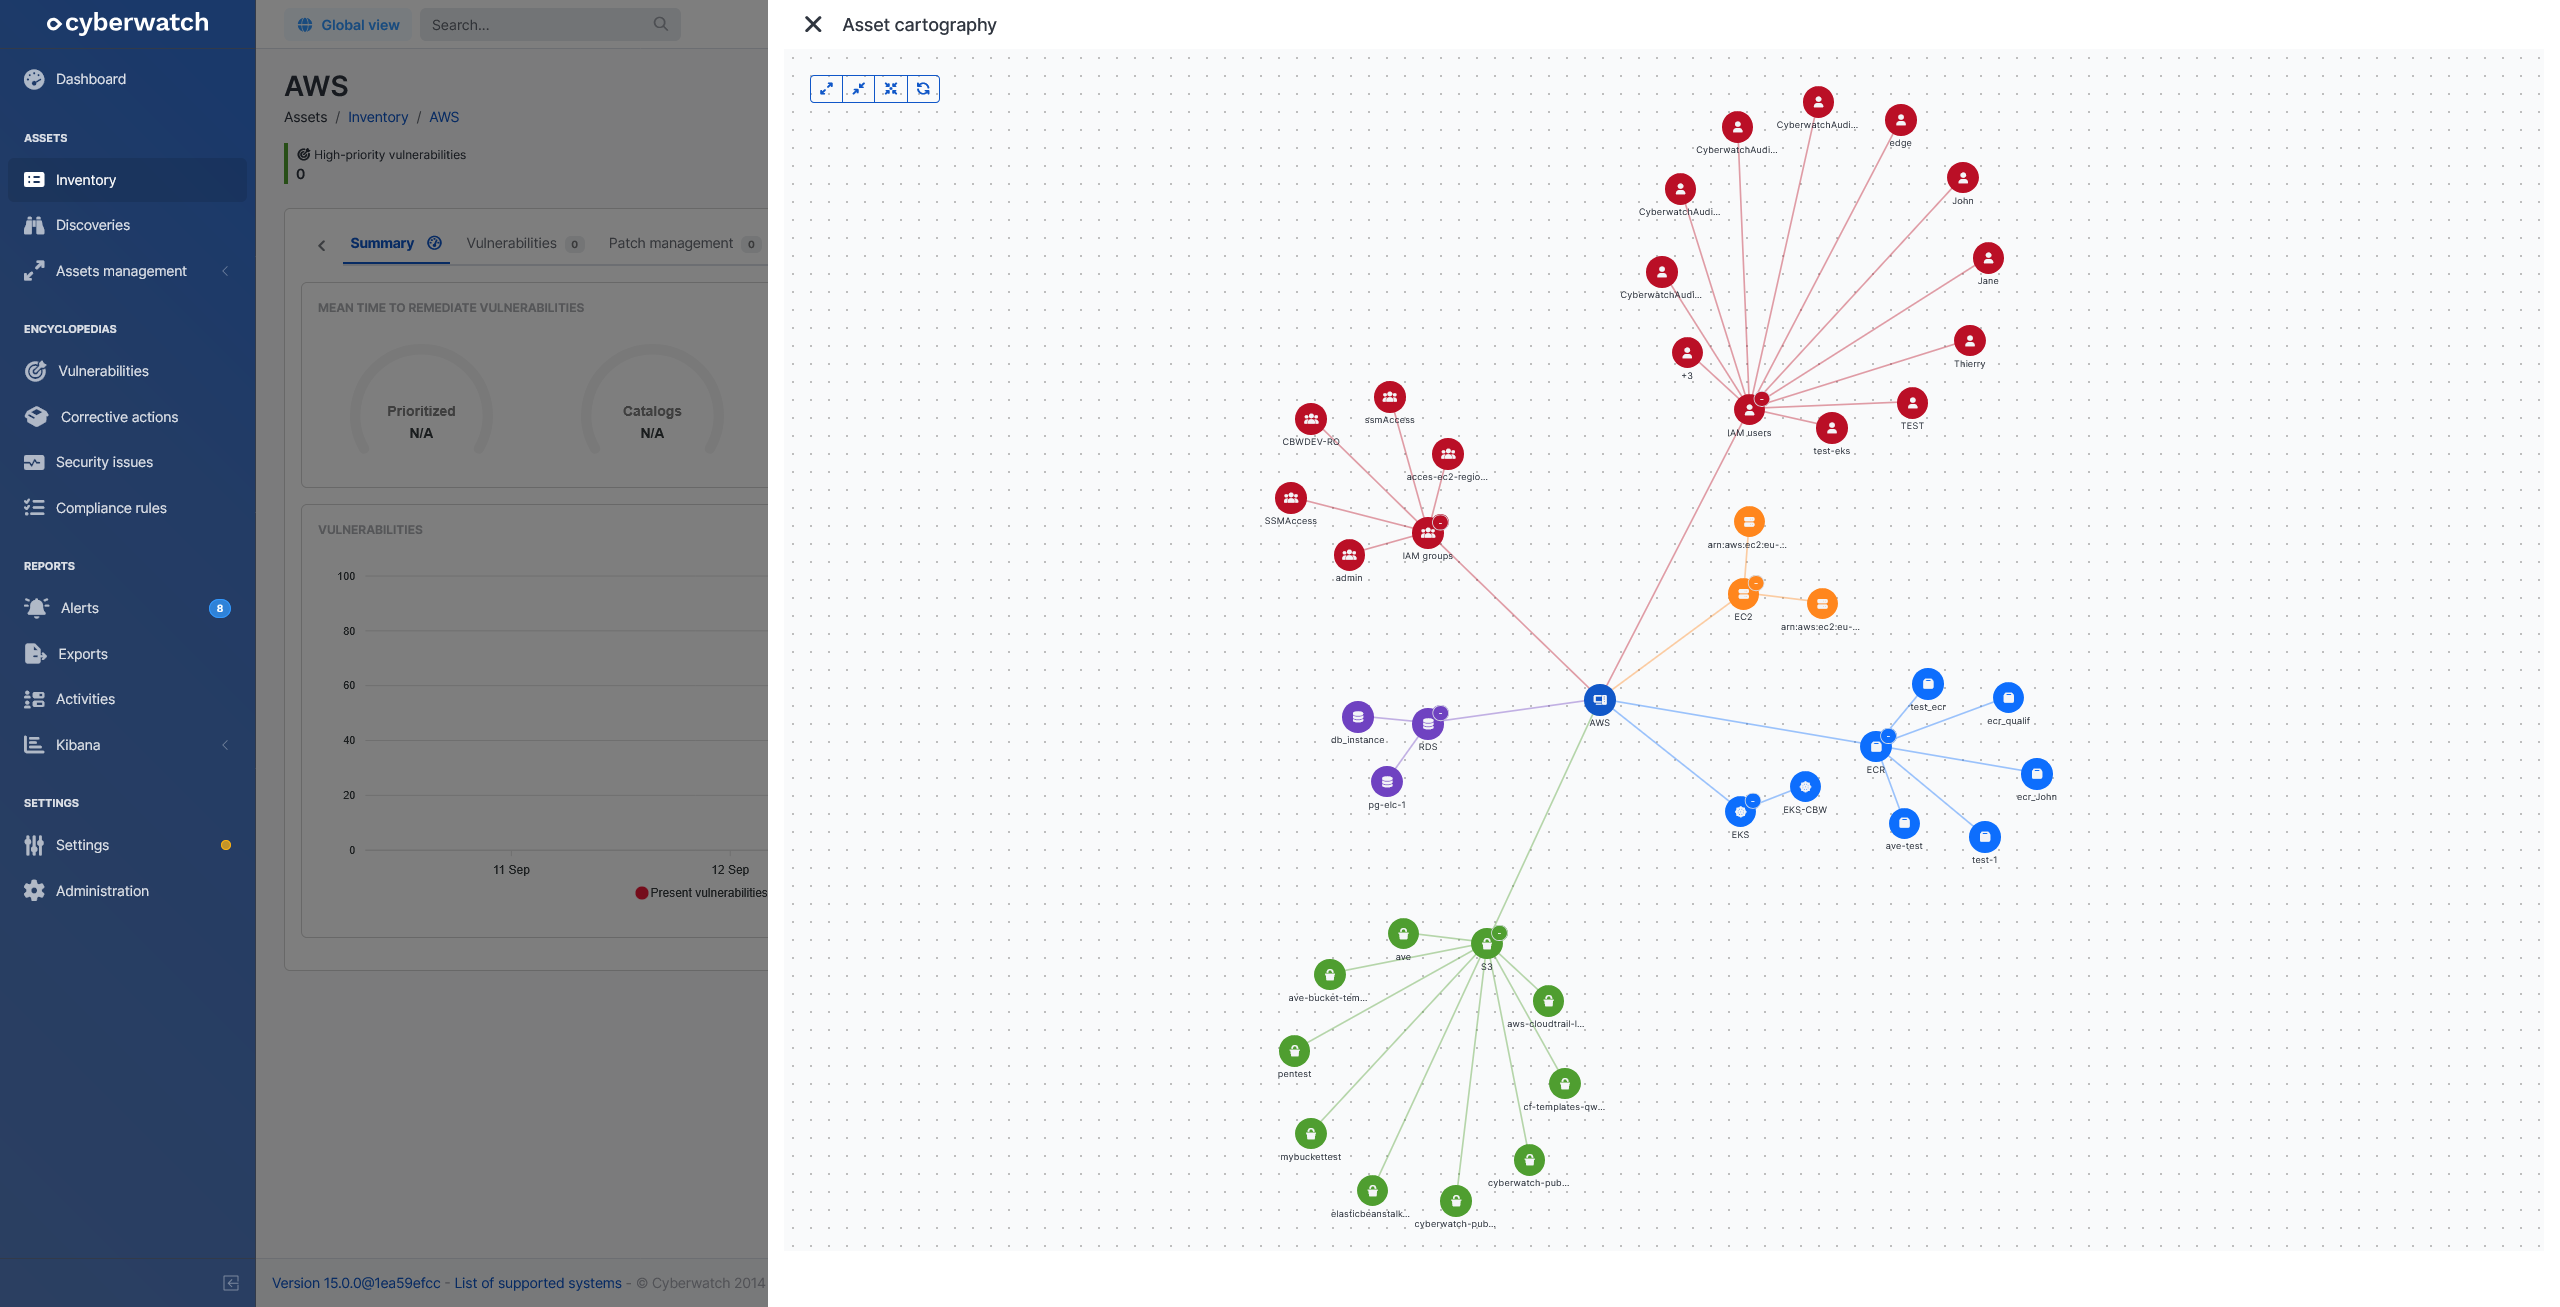
- Details of an Asset: added a map visualization of an asset and its relationships (preview)
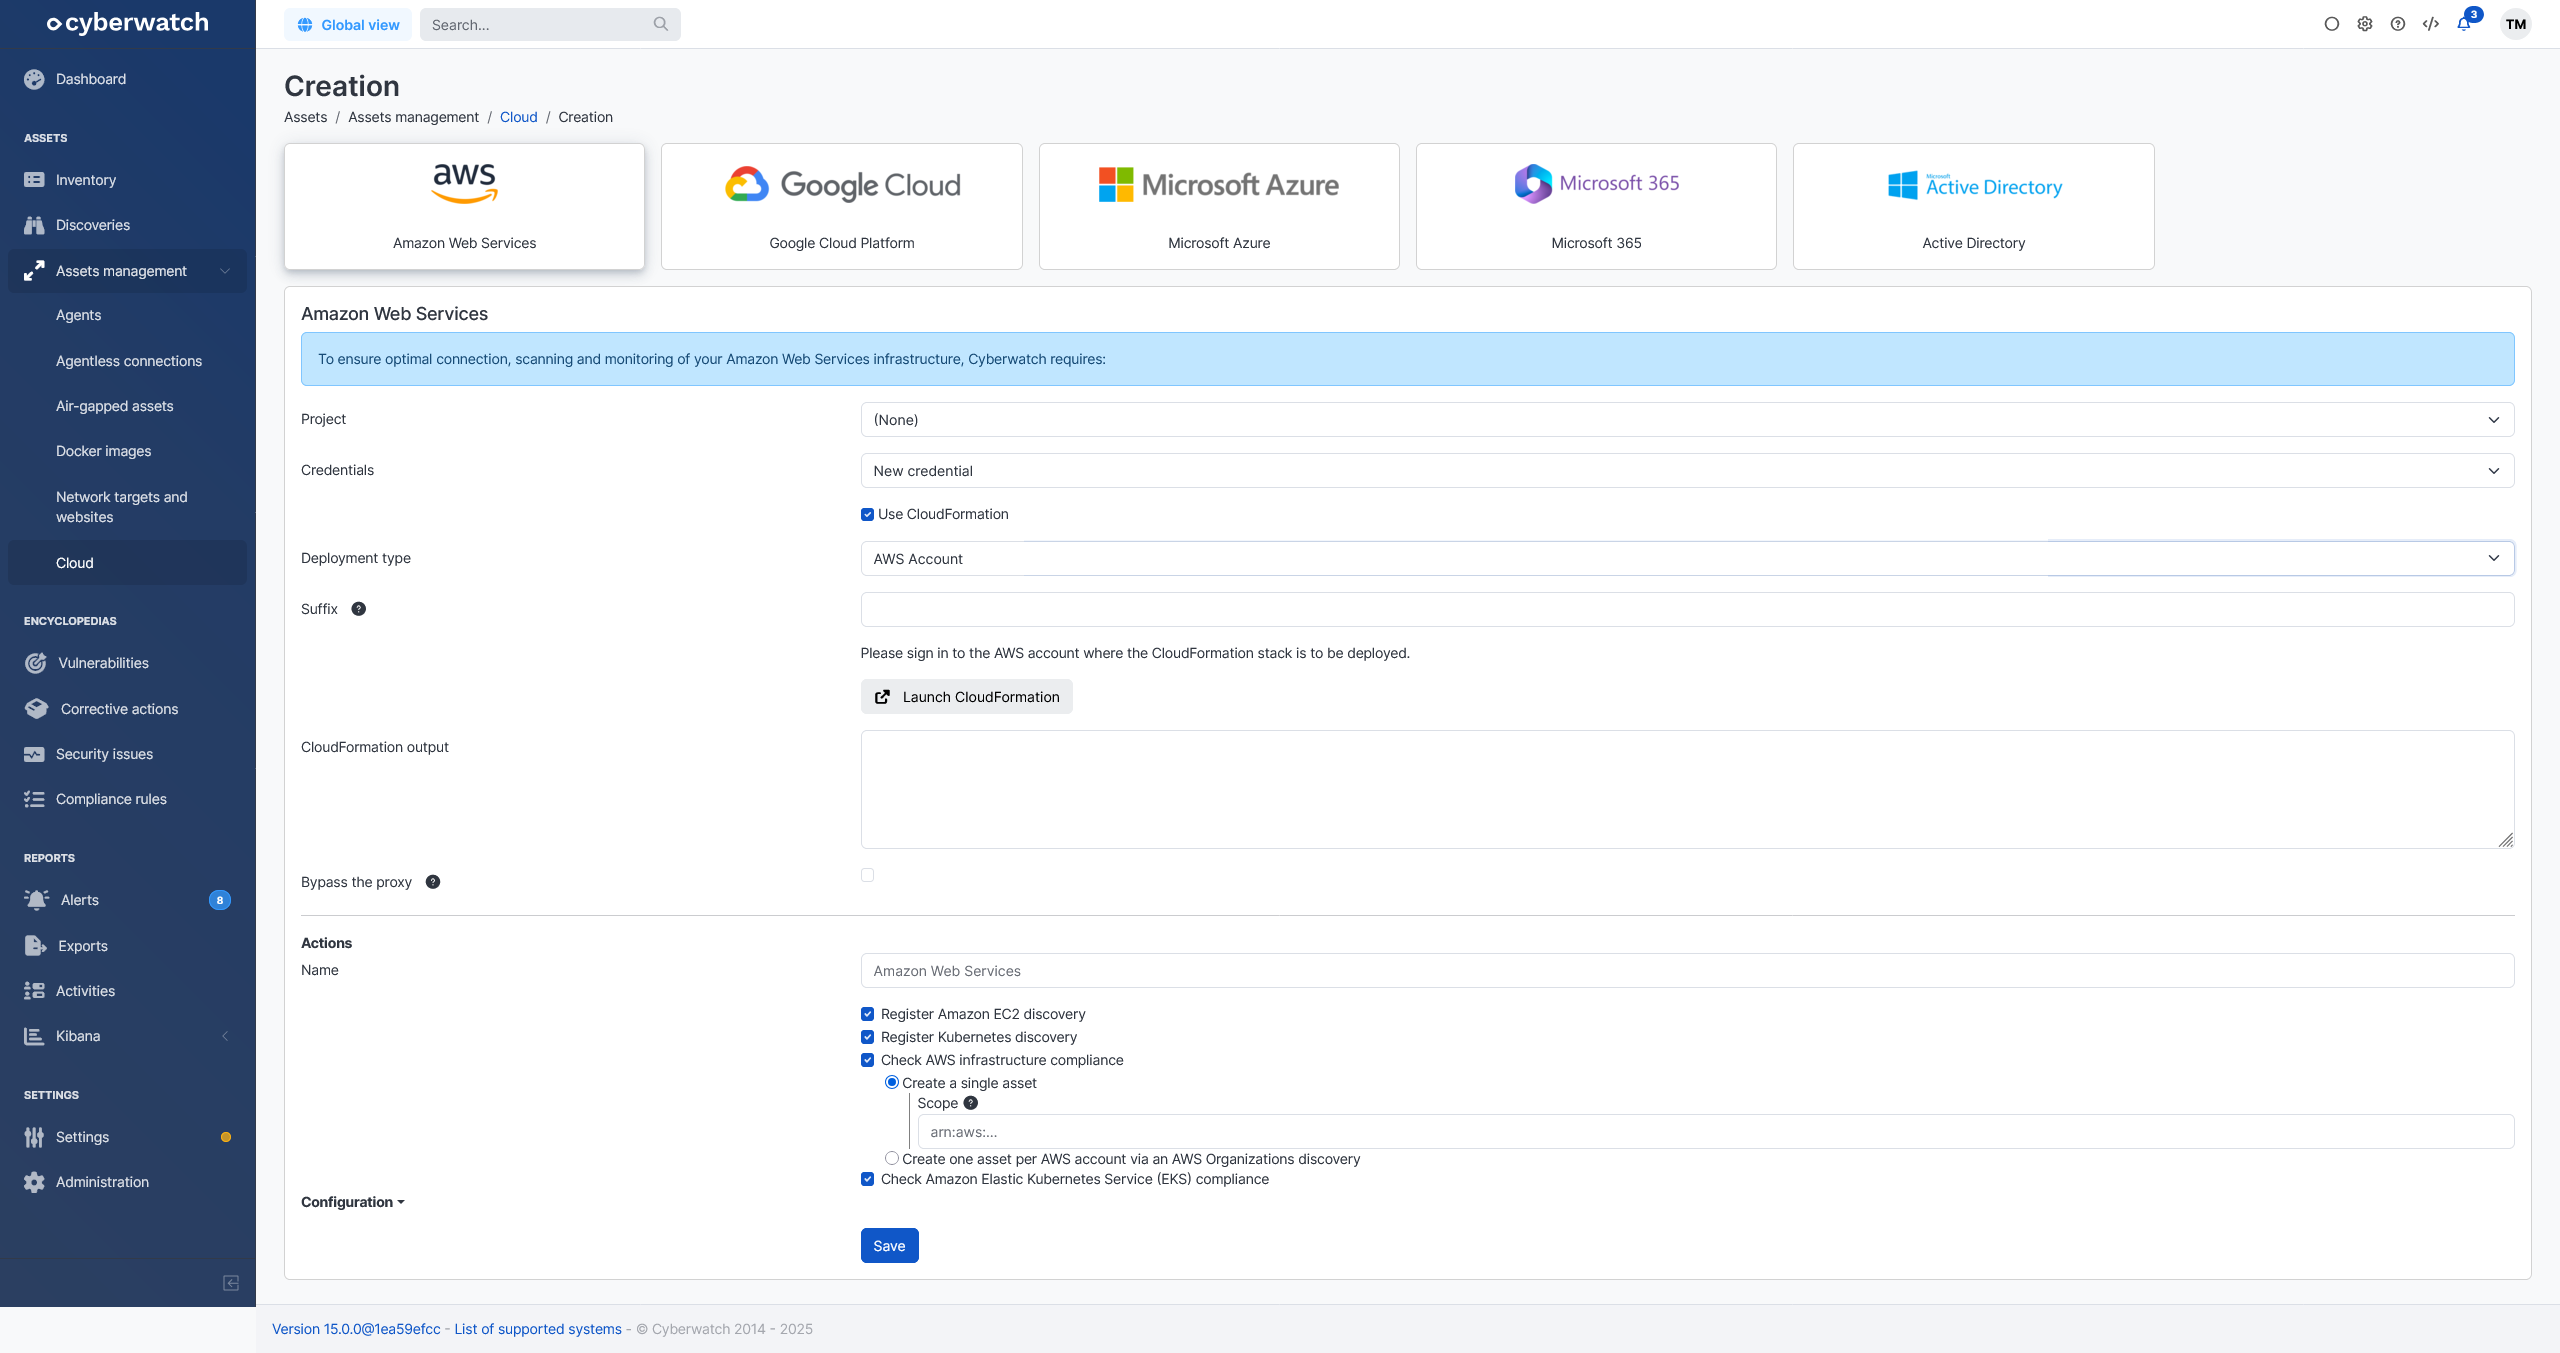
- Cloud: support for integration with CloudFormation, to simplify the addition of your AWS environments to Cyberwatch and gain enhanced visibility across all your resources (preview)
New features:
- API: all users can now access the API
- Authentication provider: you can set a time limit before users are deactivated or deleted
- Compliance: added CIS Amazon Elastic Kubernetes Service (EKS) Benchmark
- Docker images: you can now scan Podman containers on Linux assets
- Discoveries:
- Added AWS Organizations discoveries
- Added Microsoft Hyper-V discoveries
- Kibana: added a new dashboard dedicated to priority vulnerabilities
- Network targets and websites: pages scanned during a target scan are now displayed on the Web pages tab of the details of an Asset
- Scope:
- Added security advisories from Veeam Backup & Replication
- Added support for Amazon SSM Agent on Windows
- Added support for Debian 13
- Added support for Erlang OTP
- Added support for ManageEngine ADSelfService Plus
- Added support for Rocky Linux 10
Updated features and performance improvements:
- Agentless mode connection: the SNMP device detection feature has been refactored
- API: the
/api/v3/servers/{id}/cve_announcements/{cve_code}route also allows you to set a reactivation date for a vulnerability - Cloud: UX improvements to the assistant to facilitate the use of discovery and compliance features
- Compliance:
- Updated multiple CIS Benchmarks
- You can define project-specific compliance repositories, allowing system administrators with limited access to manage the compliance of their assets
- Discoveries:
- A system administrator with limited access can now create discoveries
- Amazon ECR discoveries now rely on the AWS API
- AWS discoveries are renamed to Amazon EC2
- DNS and Certificate Transparency discoveries now rely on Nmap
- Docker images:
- Failed analyses are automatically relaunched
- Support for images with UIDs and GIDs greater than 60000
- External tools: you can specify the body format of Syslog requests
- Vulnerability encyclopedia: extension of CVE catalogs to authorities other than CERT-FR ALE and CISA KEV
- MITRE ATT&CK: Cyberwatch now relies on attack techniques from ATT&CK version 17
- Scanning engine: improved the IBM AIX equipment analysis
- Scope: improved the Veritas Netbackup support
- Stored credentials: improved endpoint support for Amazon ECR registries
Bugfixes:
- Corrective actions: fixed the Windows Package Manager support to update third-party applications
- Compliance:
- Fixed the script of Microsoft Windows Server 2022 CIS Benchmarks rules
- Fixed the script of rule ICS-LIN-6.6.9
- Discoveries:
- Fixed an IP address retrieval problem for Proxmox discoveries
- Fixed an issue with uniqueness in group relationships that occurred when automatically adding groups to their associated assets in synchronization mode